ADCS-Attack: The Cheat Sheet That Turns PKI Misconfigurations Into a Map
A lightweight GitHub index for the ESC1 to ESC10 attack surface, and a sharp example of how offensive security knowledge gets standardized, searched, and reused.
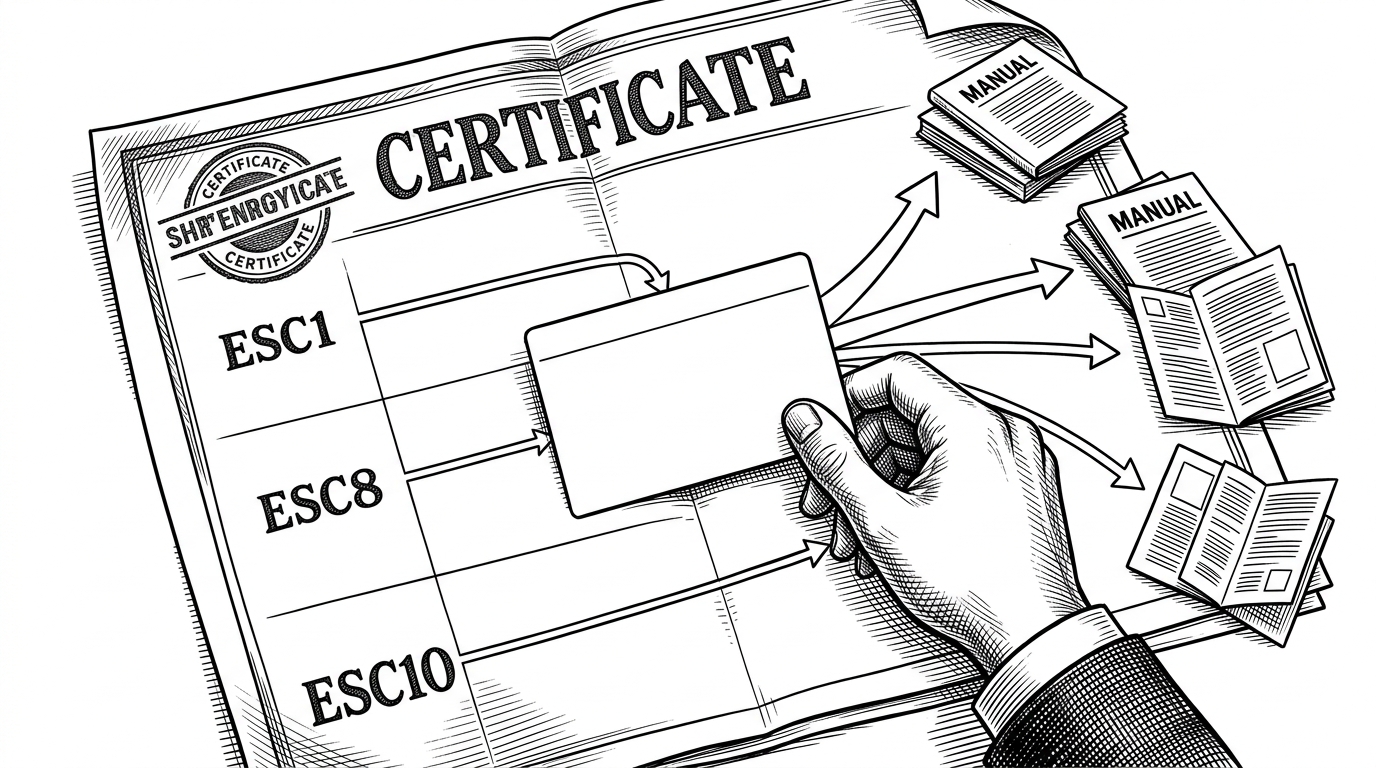
- ADCS-Attack is not an exploitation framework, it is a translation layer that turns ADCS abuse into a searchable ESC matrix.
- Its value comes from compression: one README points readers from a misconfiguration to the right deeper guide fast.
- The repo sits one level above tools like Certipy and Certify, which means it helps operators interpret findings before they execute anything.
- The project reflects a broader shift in security knowledge, where GitHub repos increasingly function as operational indexes for tradecraft.
ADCS is one of those Windows surfaces that looks ordinary until it isn’t. A certificate template, an enrollment setting, or a mapping quirk can become a durable identity primitive, which is why ADCS abuse has earned such a strong place in offensive tradecraft. The problem is not lack of material. It is friction. The knowledge exists, but it is scattered across research papers, blog posts, and tooling docs.
That is the niche Ignitetechnologies/ADCS-Attack fills. It does not try to replace the research or the tools. It turns the attack surface into an index, with ESC entries that point to the next thing you need to read. In practice, that makes the README feel less like a file and more like an interface.
When password attacks fail or are noisy, Active Directory Certificate Services (AD CS) often provides a quieter and more elegant road to domain compromise.
Why ADCS Becomes a Shortcut to Domain Compromise
The reason ADCS keeps showing up in red team writeups is simple. Certificates can impersonate identity in ways that feel cleaner than password reuse or spray-and-pray credential attacks. If a template is loose, or certificate mapping is weak, the attacker is no longer guessing who you are. They are borrowing the system’s own trust model.
That is what makes this repo useful. It starts from the reality that ADCS is hard to hold in your head, then collapses that complexity into named paths. Instead of forcing the reader to remember every nuance of every flaw, it gives them an entry point that matches how practitioners actually work: enumerate, classify, then drill down.
The Repo as a Living Attack Index
The main trick here is structural. The README is the product. Each ESC row behaves like a decision node: a short description, a label that practitioners already recognize, and a link out to a deeper guide. That means the repo is not competing with long-form research. It is packaging it for navigation.
| Artifact | Primary role | What it gives you | What it is not |
|---|---|---|---|
| ADCS-Attack | Curated index | A map from ESC labels to deeper guides | A standalone exploitation tool |
| Certipy | Active exploitation tool | Enumeration, certificate requests, and auth workflows | A taxonomy or reading guide |
| Certify | Windows operator tool | Native enumeration and exploitation for Windows environments | A cross-platform reference index |
| Certified Pre-Owned | Foundational research | The original language and threat model for ADCS abuse | A lightweight operational cheat sheet |
How the ESC Matrix Turns Abstraction Into Action
ESC1 through ESC10 work because they compress a messy domain into a vocabulary people can share. Once a tester sees a template issue, a relay path, or a mapping problem, the ESC label tells them what kind of failure they are looking at and where to go next. The value is not just naming. It is routing.
That is also why the repo is so lightweight. It does not need to restate the whole attack chain in every entry. It only needs to answer three questions quickly: what category am I in, why does it matter, and where is the deeper walkthrough? For a practitioner in the middle of an assessment, that is enough to move from uncertainty to action.
Active Directory Certificate Services (ADCS) has quietly become one of the most reliable paths to domain compromise we encounter during internal penetration tests. It’s deployed widely across enterprise environments, rarely hardened, and the attack techniques are well understood enough to be consistent — yet most organisations have never had their PKI infrastructure reviewed.
Why the External-Link Model Is the Point
The repo’s design tradeoff is obvious and intentional. It keeps the GitHub surface thin and points the reader outward for the full writeups. That makes maintenance easier and browsing faster, but it also means the repository is a gateway, not a library. Its power comes from being the front door to a larger knowledge set.
That model is useful because it mirrors how practitioners already consume security content. They do not want one giant monolith when they are triaging a finding. They want a fast index, a stable taxonomy, and a clean exit to the exact detail that matters. ADCS-Attack optimizes for that workflow.
| Approach | Strength | Tradeoff |
|---|---|---|
| Keep the repo as an index | Fast to scan, easy to maintain, easy to link | Depends on external articles being available |
| Put everything in one repo | Self-contained and offline-friendly | Harder to update and much noisier to browse |
| Rely on raw tooling output alone | Precise and immediate | Does not explain what the findings mean |
How It Fits the ADCS Tooling Ecosystem
The cleanest way to place this repo is by layer. SpecterOps defined the language of the problem. Certipy and Certify operationalize it. ADCS-Attack sits in between, organizing the map so a reader can move from a discovered weakness to the right branch of the taxonomy without losing context.
| Layer | Representative artifact | Best for |
|---|---|---|
| Research taxonomy | Certified Pre-Owned | Understanding the attack surface and naming the patterns |
| Operational tooling | Certipy | Finding, requesting, and using certificates in practice |
| Windows-native tooling | Certify | Operator-friendly enumeration and exploitation on Windows |
| Curated index | ADCS-Attack | Turning the whole field into a readable lookup table |
That layering matters because modern security knowledge rarely lives in one place anymore. It gets split into research, tools, and indexes. This repo is a good example of the third category. It does not steal the spotlight from the others. It makes them easier to use.
What This Says About Modern Security Knowledge
The bigger lesson is cultural. In security, the most valuable GitHub repos are often not the cleverest codebases. They are the ones that reduce search cost. They tell you what category you are in, what label to use, and what to read next. That is a product decision as much as a documentation choice.
ADCS-Attack shows how offensive knowledge becomes reusable once it is standardized. A complex compromise path stops looking like folklore and starts looking like a system. That is why this small repository matters: it does not just document ADCS abuse. It makes the domain navigable.