Separating the Eyes from the Hands: Inside NishithP2004/spectra
How a Kubernetes-native orchestration platform uses strict agent hierarchies and ephemeral sandboxes to safely unleash AI on offensive security tasks.
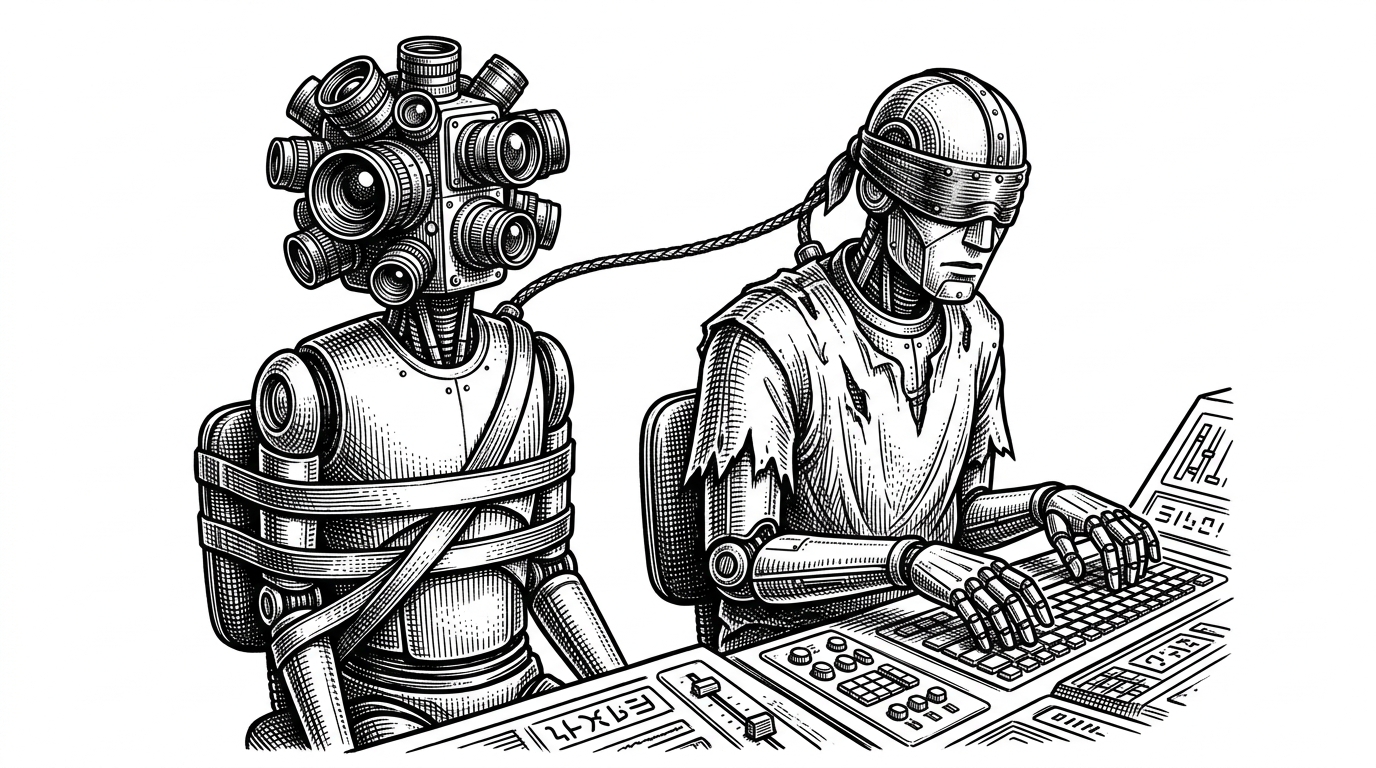
- Spectra resolves the AI browser automation hallucination loop by enforcing a strict hierarchy where the Planner agent only sees and the Clicker agent only acts.
- The system contains the blast radius of autonomous offensive security tasks by dynamically provisioning and destroying isolated Kubernetes namespaces for every session.
- By leveraging the Model Context Protocol (MCP), Spectra transforms complex security environments like Kali Linux and CyberChef into callable API primitives for LLMs.
The most common failure mode in autonomous web agents is the hallucination loop. An LLM predicts the existence of a "Submit" button, decides to click it, and executes a script to interact with the DOM element. If the button is not actually there, the agent crashes, gets confused, or worse, clicks something destructive.
Spectra addresses this physical reality of autonomous execution by lobotomizing its own agents. Built on Google's Agent Development Kit, it enforces a strict separation of concerns. The Planner agent is restricted entirely to taking screenshots. It serves as the eyes. The Clicker agent is explicitly instructed in its prompt to never make independent decisions. It acts strictly on coordinates provided by the Planner. It serves as the hands.
Spectra is a Kubernetes-native platform for orchestrating AI agents to safely execute complex, multi-step tasks inside sandboxed browser and system environments.
Sandboxing the Blast Radius
Most open-source agent projects are Python scripts meant to run locally. Spectra is designed from the ground up as a cloud-native platform. Because it is built to execute offensive security tasks, the blast radius of a rogue agent is a primary concern.
The architecture relies on a Node.js and Express router that acts as an orchestrator. When a user initiates a session, the router dynamically provisions a completely isolated Kubernetes namespace. It uses a template engine to inject unique credentials and spins up a private pod containing the entire Spectra stack. If an agent performs a destructive action, the entire environment is simply nuked. It is a crash-only, ephemeral design.
Penetration Testing as an API
Giving an LLM access to a raw shell is dangerous and unreliable. Spectra mitigates this by adopting the Model Context Protocol to wrap complex utilities into callable functions. It treats penetration testing as a set of high-level API primitives.
The project integrates a specialized Pentest agent with a Kali Linux environment, and a CyberChef agent for data transformation. Instead of writing raw Nmap or Gobuster commands, the LLM calls native Python functions exposed via a FastMCP server. This abstracts the complexity of shell execution and output parsing, allowing the agent to focus on semantic strategy rather than syntax.
The Platform vs. The Framework
Spectra contextualizes itself within the broader open-source AI ecosystem by offering an opinionated, deployment-ready architecture. It is not a build-it-yourself library like LangChain, nor is it a general-purpose agent like AutoGPT. It is a batteries-included operating system for specialized security automation.
| Feature | Spectra | AutoGPT | LangChain |
|---|---|---|---|
| Core Focus | End-to-end platform for sandboxed AI agents | General-purpose autonomous agent | Framework for building LLM apps |
| Primary Deployment | Kubernetes / Docker Compose | Docker / Local | Library (Flexible) |
| Built-in Sandboxing | Browser (noVNC) and System (Kali Linux) | Limited / Plugin dependent | None (Dependent on implementation) |
| Agent Hierarchy | Strict (Planner vs Clicker) | Monolithic | Developer defined |