Inside `Sumitd-26/Project-management-backend`: A Project App Backend Built Around Trust, Not Just Tasks
A modern Express 5 and MongoDB API that treats authentication, verification, and error handling as first-class architecture, revealing how serious backend foundations get built before the product surface exists.
- This repository is most interesting as a trust-first auth scaffold, not as a finished project-management product.
- Its strongest idea is the verification-token lifecycle, where the stored secret is hashed and the emailed secret is not.
- The codebase favors reusable primitives like standardized errors, response wrappers, validation, and token methods over ad hoc route logic.
- It is already preparing for RBAC and collaboration workflows, even though the task domain itself is still mostly absent.
The real product is the auth layer
At first glance, this looks like a backend for tasks, projects, and teams. Under the hood, the most developed system is identity: signup, verification, access tokens, refresh tokens, error handling, and templated email delivery. That is the real product today, and it is more interesting than a bare CRUD promise.
The repo’s internal name, "Basecampy," makes the intent clearer. This is scaffolding for collaboration software, but the scaffold is already opinionated about security and developer ergonomics. It is building the trust fabric before the workspace exists.
Why hashed verification tokens matter
The cleanest idea in the repo is the temporary verification token flow. The server generates a random token with `crypto.randomBytes(...)`, hashes one copy for storage, and sends the unhashed copy by email. That means the database never holds the exact value a user needs to complete verification.
This is a small move with a real security payoff. If the database leaks, the attacker gets a hash, not a working verification link. The system still works for the legitimate user, but the trust boundary is tighter than in the usual beginner backend.
How the repo keeps controllers clean
The architecture leans on a few small utility layers. `asyncHandler` removes repetitive `try-catch` blocks, `ApiError` gives failures a consistent shape, and `ApiResponse` keeps success payloads from drifting into one-off formats. That sounds mundane until you compare it with the average tutorial backend, where every controller invents its own habits.
import { asyncHandler } from "../utils/async-handler.js";
import { ApiError } from "../utils/api-error.js";
import { ApiResponse } from "../utils/api-response.js";

const registerUser = asyncHandler(async (req, res) => {
  const user = await User.create(req.body);

  if (!user) {
    throw new ApiError(500, "User creation failed");
  }

  return res.status(201).json(
    new ApiResponse(201, user, "User registered successfully")
  );
});
That structure is not just tidier. It is a signal that the repo is trying to become a platform, not a pile of routes. Once the surface area grows, standardized errors and responses pay back every decision they made early.
The middleware gate at the edge
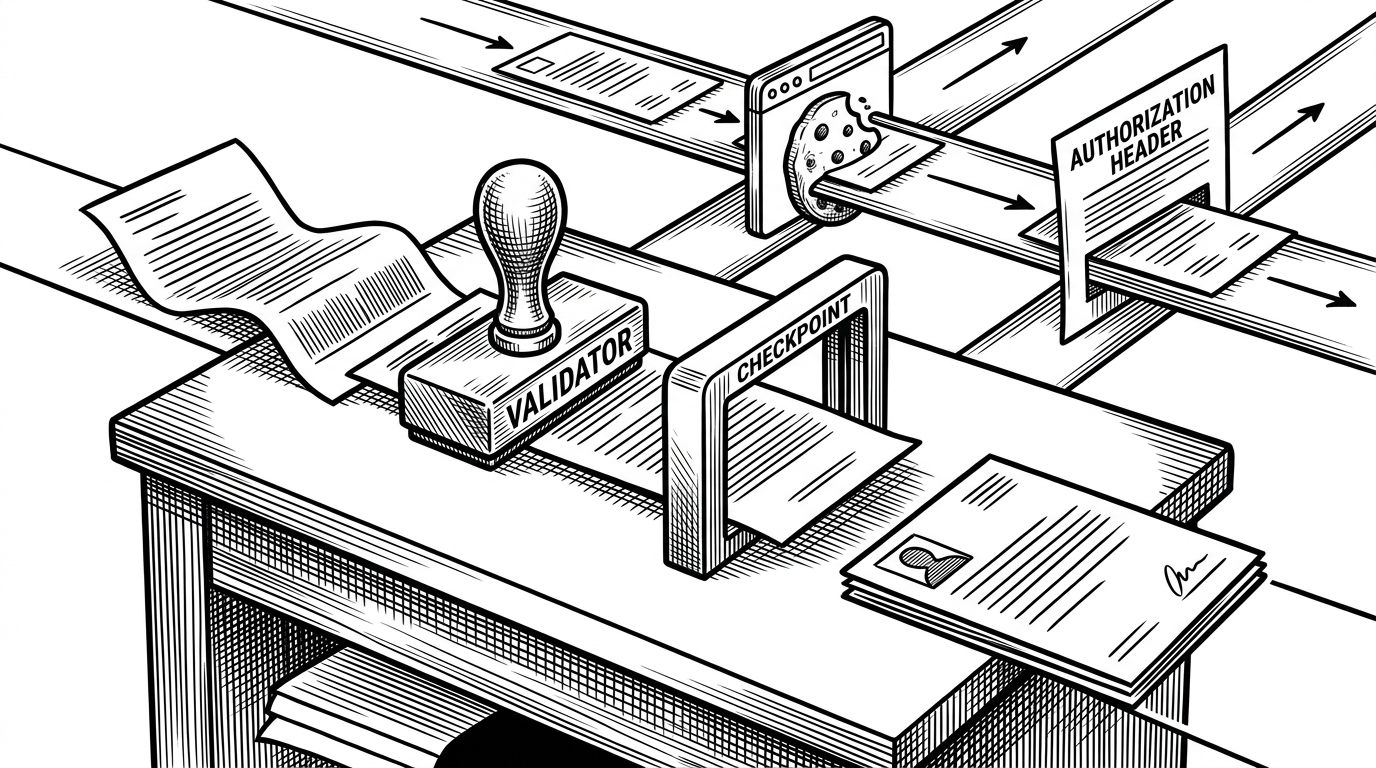
`verifyJWT` sits where it should: at the edge. It checks for an access token in either the cookie or the Authorization header, which means the same backend can support browser sessions and programmatic clients without rewriting the auth story.
That dual-path lookup matters more than it sounds. Cookie auth is convenient for web apps. Header auth is cleaner for external clients. The middleware lets the repo serve both without splitting into separate authentication systems.
What the repository is preparing for
`UserRolesEnum` and `TaskStatusEnum` tell you where this is headed. The repo is already naming the permission model and the workflow states, even before the project and task CRUD is fully there. That is how you lay rails for RBAC without overbuilding the rest of the app too early.
| Area | Typical tutorial backend | This repository |
|---|---|---|
| Authentication depth | Basic login and logout | Access tokens, refresh tokens, verification flow, and middleware gates |
| Verification token handling | Plain token stored or ignored | Random token generated, hashed for storage, unhashed value sent to email |
| Error standardization | Ad hoc status codes and messages | Shared `ApiError` and `ApiResponse` wrappers |
| Email handling | Raw nodemailer text | Templated HTML email flow with Mailgen |
| Validation | Light request checks | Schema-driven validation with `express-validator` |
| RBAC readiness | Usually absent | Enums already hint at roles and task states |
| Product maturity | Proof of concept | Reusable backend foundation |
How this differs from a typical tutorial backend
Most Node tutorials prove a concept and stop. This repo is more deliberate. It separates concerns, standardizes outputs, and uses the model layer for token behavior instead of scattering it through controllers. That makes it easier to grow, but it also makes the code more readable now.
The difference is structural, not cosmetic. The repo is already thinking in primitives: token lifecycle, validation, middleware, email templates, and enums. A tutorial proves you can ship a login form. This codebase is trying to make login one dependable subsystem inside a larger product.
| Question | Tutorial-grade answer | This repo’s answer |
|---|---|---|
| Where does the important logic live? | Inside route handlers | In models, middleware, and shared utilities |
| How are failures handled? | Per-controller `try-catch` blocks | A common async wrapper and typed error class |
| How are emails sent? | Plain text or quick templates | Structured verification mail templates |
| What gets persisted for verification? | Usually the token itself | Only the hash of the temporary token |
| What can the app grow into? | A demo | A collaboration backend with roles and state flow |
What it still is, and what it is not
It is a strong starter kit for a trust-heavy backend. It is not yet a project-management system in any meaningful product sense, because the actual project, task, and collaboration surfaces are still waiting to be built. That gap is not a flaw in the code. It is the current shape of the repository.
Viewed honestly, the repo’s value is foundational. It shows how to build the part most teams postpone: the secure identity layer that every real collaboration app eventually depends on.