wloc: How a Proxy Turns Apple’s Location Service Into a Ghost API
A clever iOS spoofing tool hides in MITM seams, rewrites Apple’s WLOC responses, and uses a web map plus Shortcuts to make system-level location control feel local.
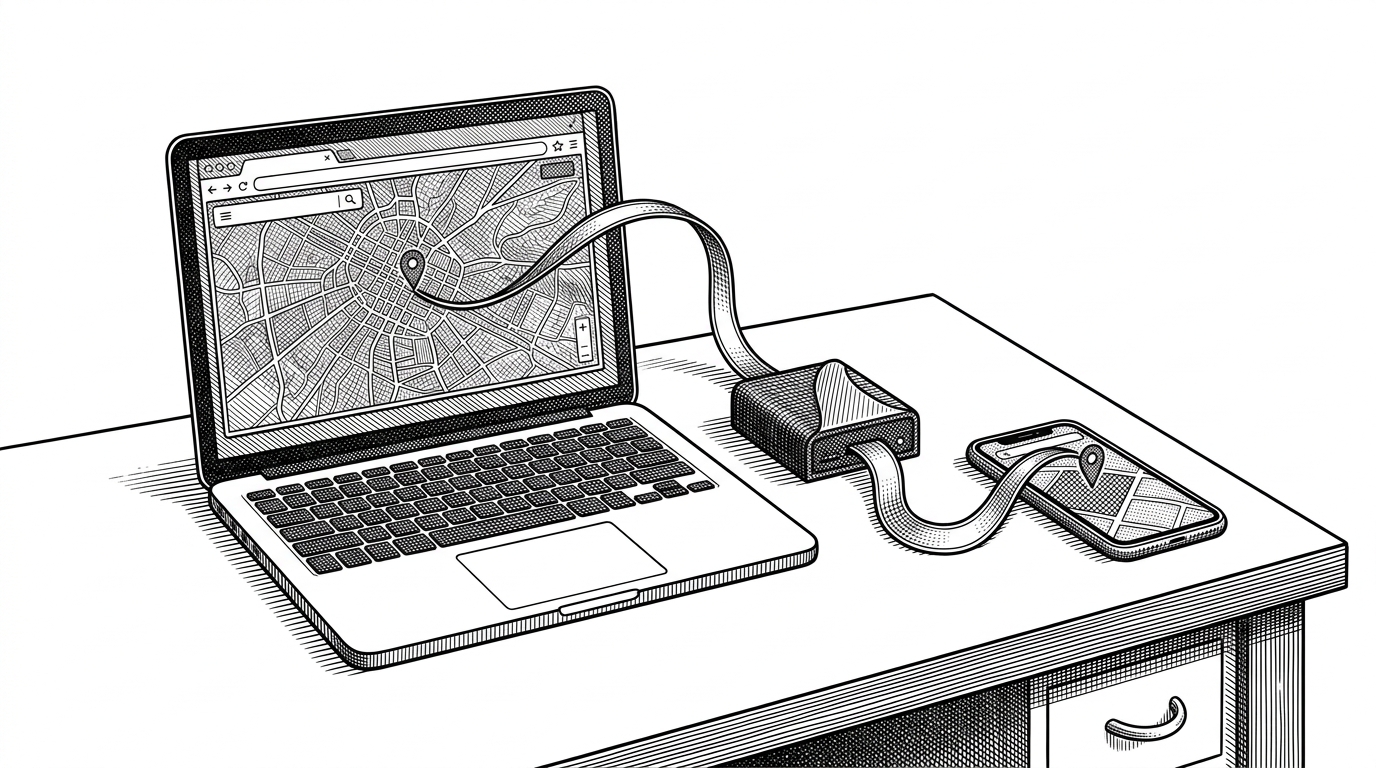
- wloc is not a GPS faker so much as a trust-boundary exploit that rewrites the answer Apple’s own location pipeline receives.
- Its real novelty is the ghost API pattern, where a browser UI communicates through a proxy without needing a conventional backend.
- The project’s hardest technical work is not the map UI but the parsing and coordinate normalization that make real-world inputs usable.
- Apple’s tighter location caching turns the tool into an ongoing negotiation with the platform, not a one-time trick.
Most location spoofing tools try to impersonate hardware. wloc takes a stranger route. It wedges itself into the path between a web UI, a proxy app, and Apple’s own WLOC response, then edits the answer before iOS can trust it.
That makes the project feel less like a utility and more like a systems heist. The browser is not merely a front end. It is a control surface that speaks through a domain the proxy is already watching.
The browser that controls a system service
修改 Apple 网络定位(gs-loc)返回坐标 · 支持 Surge / Quantumult X / Loon / Stash · 快捷指令一键设置/恢复定位
The core move is simple to describe and elegant to use. A map page lets you choose coordinates, then sends a save request to a fake Apple endpoint, gs-loc.apple.com/wloc-settings/save. The proxy catches it, stores the values locally, and later rewrites the next WLOC response with those coordinates.
No desktop app needs to stay open. No database sits in the middle. The proxy module and the web Worker act like two halves of a hidden API, with Apple’s own hostname providing the seam.
Why wloc is not just another spoofing tool
| Method | Jailbreak | PC required for daily use | Route simulation | System-layer behavior | Setup friction |
|---|---|---|---|---|---|
| wloc | No | No | No | Rewrites Apple WLOC responses through MITM | Medium |
| Desktop tethered tools | No | Usually yes | Yes | Changes location through a connected computer | Medium to high |
| Jailbreak injectors | Yes | No | Sometimes | Directly hooks system or app behavior | High |
| Hardware dongles | No | No | Limited | Simulates GPS at the hardware layer | High |
The comparison is what makes the niche obvious. wloc is not trying to win on raw feature count. It is trying to occupy the gap between full jailbreak control and clunky tethered desktop tools.
That gap matters. If you already live inside Surge, Quantumult X, Loon, Stash, or Shadowrocket, then a proxy-native location tool feels native to your workflow instead of bolted on.
The trick behind the curtain
// Conceptual flow inside the proxy module
if (request.url.includes('/wloc-settings/save')) {
  $persistentStore.write(JSON.stringify(coords), 'wloc');
}

if (request.url.includes('gs-loc.apple.com/clls/wloc')) {
  const saved = $persistentStore.read('wloc');
  body = rewriteProtobufResponse(body, saved);
}
The implementation is split cleanly. wloc-settings.js acts like a sink for the save action. wloc.js catches the real Apple response and patches it before the OS sees it. The worker-side UI is just the control panel.
That separation is the reason the tool feels light. The map and the proxy do different jobs, and neither one has to pretend to be a full app server.
The geometry problem nobody expects
The map UI is more forgiving than it looks. It can ingest Apple Maps links, Amap short links, and raw text, then normalize them into usable coordinates. That is the difference between a demo and something people can actually use.
The standout detail is the GCJ-02 to WGS84 correction loop. Instead of a single blunt transform, the worker iterates toward a better answer. The result is a smaller residual error, which matters when the system is picky about what counts as plausible.
This is the article’s quiet surprise. The repo is marketed as a spoofing tool, but part of its intelligence is pure data wrangling.
Why Apple’s caching changed the game
The project’s most important constraint is not the proxy. It is locationd. According to the repository notes, newer iOS versions cache real location data more aggressively, which means toggling settings is no longer enough to force a fresh read.
That turns the tool into a moving target. The spoof still works, but the path from save action to visible system state now depends on how stubborn Apple’s cache is. On newer systems, the project recommends a reboot to clear it.
This is where the metaphor stops being cute. wloc is not a permanent jailbreak-style rewrite of the platform. It is an exploit of the platform’s current memory model, and Apple can harden that model at any time.
What this project says about modern iOS customization
wloc is a good example of seam-based software. It does not fight the OS head-on. It routes around the parts that are easiest to trust, then uses them against each other.
That is why the project is interesting even if you never plan to spoof a phone. It shows how much power still lives in the gaps between browser, proxy, and system service.