Prostore: The Next.js Ecommerce Stack That Treats Cart Ownership as a First-Class Problem
A deep look at how one unified app handles anonymous shopping, account sign-in, orders, and admin control without a separate API layer.
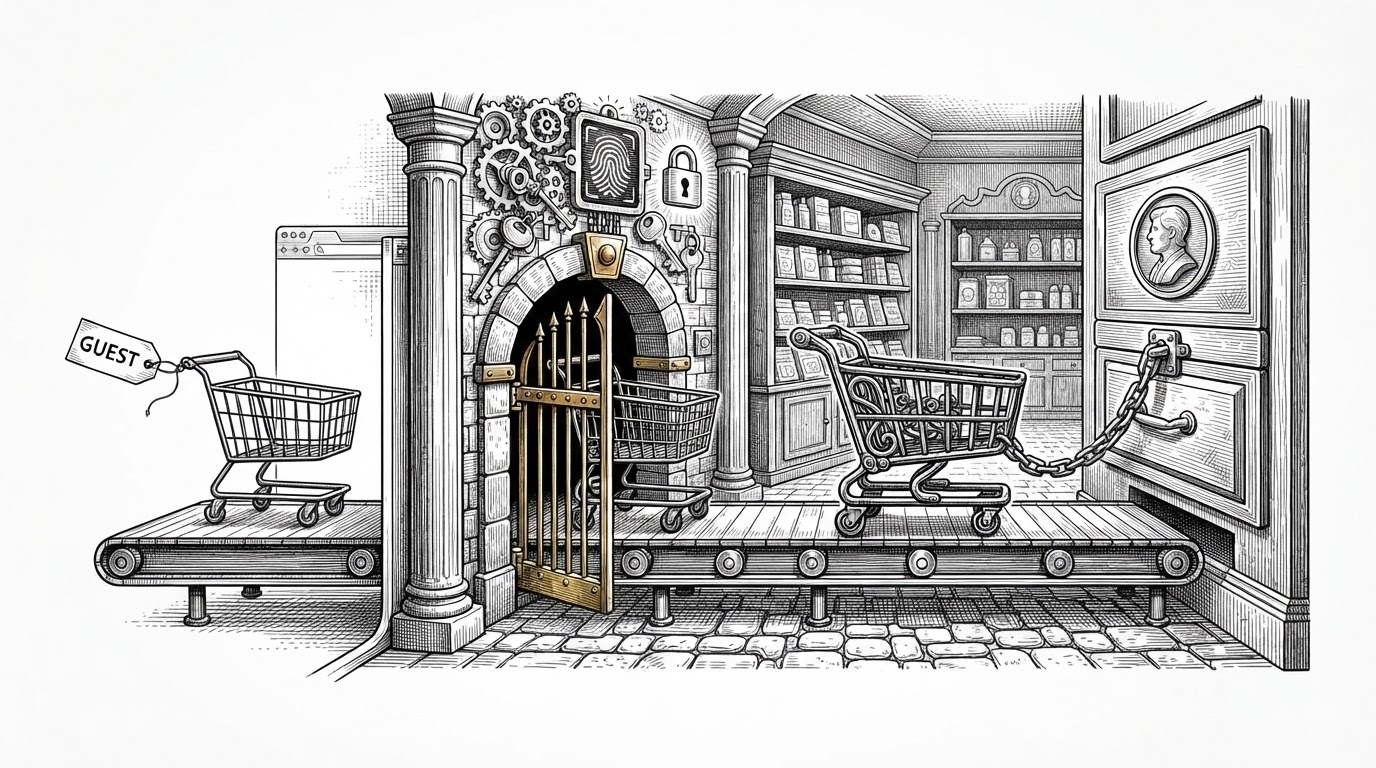
- Prostore’s core insight is that ecommerce is a state problem first and a UI problem second.
- The guest cart handoff turns login into a continuity feature instead of a broken moment in the purchase flow.
- Server Actions, Prisma, and NextAuth keep the business logic close to the interface without a traditional API layer.
- The project is most valuable as a blueprint for building a real store that stays teachable.
The Invisible Problem Most Stores Get Wrong
Most ecommerce demos look finished until you test the one behavior that matters: a visitor adds items as a guest, signs in later, and expects the cart to survive. That is where a lot of store starters quietly fall apart.
Prostore treats that handoff as the main event. The app is not just showing products and checkout buttons. It is preserving commerce state across identity changes, which is what makes a store feel real.
Prostore’s Core Move Is a State Handoff
In practice, the app starts with a cookie-backed sessionCartId for anonymous users. When sign-in happens, the auth callback checks whether that session cart exists, then reassigns it to the authenticated userId so the cart does not reset at the worst possible moment.
That is a small behavior with a large effect. It makes guest browsing, account creation, and checkout feel like one continuous flow instead of three disconnected screens.
Why the App Has No Traditional API Layer
Prostore leans on Next.js Server Actions instead of scattering business logic behind a conventional REST layer. Cart updates, checkout, product mutations, and admin actions live close to the UI that triggers them.
That choice reduces ceremony. The app does not spend time marshalling data into fetch calls just to bounce it back into the server. The mutation logic stays readable because the code that asks for an action is close to the code that performs it.
The Data Model Does the Real Work
model Product {
  id        String   @id @default(cuid())
  name      String
  price     Decimal
  rating    Decimal?
  images    String[]
  userId    String?
  user      User?    @relation(fields: [userId], references: [id], onDelete: Cascade)
  createdAt DateTime  @default(now())
  updatedAt DateTime  @updatedAt
}

model Cart {
  id        String   @id @default(cuid())
  userId    String?
  sessionId String?
  items     CartItem[]
  createdAt DateTime @default(now())
}

model Order {
  id        String      @id @default(cuid())
  userId    String
  total     Decimal
  items     OrderItem[]
  createdAt DateTime    @default(now())
}
The schema is where the app becomes trustworthy. Prisma models use relational integrity, Decimal types for money, and cascade behavior that keeps dependent records from drifting out of sync.
That matters because ecommerce data is fragile. Prices should not wobble on floating point math, orphaned rows should not linger after deletions, and carts should not exist in some half-owned state that the UI has to guess about.
Transactions Make Checkout Feel Atomic
Checkout is where the database stops being abstract. Prostore uses prisma.$transaction so the order, its line items, and the cart clear happen together or not at all.
That is the right guarantee for a purchase flow. A user never sees a success screen for an order that only half-exists, and the cart does not remain dirty after payment is recorded.
Type Safety Is Not Just a Compile-Time Story
TypeScript helps, but it is not the whole defense. Prostore layers Zod validation on top of server actions before the data ever reaches Prisma, which means bad input has to survive multiple checkpoints to do damage.
That is a stronger pattern than relying on the frontend alone. The UI can be wrong, the request can be forged, and the database still gets a final say before anything is written.
const formSchema = z.object({
  productId: z.string().min(1),
  qty: z.coerce.number().int().positive(),
});

export async function addItemToCart(input: unknown) {
  const data = formSchema.parse(input);

  await prisma.cartItem.create({
    data: {
      productId: data.productId,
      qty: data.qty,
    },
  });
}
What Prostore Has That Other Starters Don’t
| Project style | Backend ownership | Cart flow | Auth complexity | Learning curve | Best fit |
|---|---|---|---|---|---|
| Prostore | Unified Next.js app with Prisma | Guest cart migrates into user ownership | Handled inside the same codebase | Moderate | Learning a production-shaped store |
| Medusa | Headless commerce engine | Flexible, API-driven | Usually integrated separately | Higher | Teams that want a commerce backend first |
| Next.js Commerce | Frontend-first starter | Depends on external commerce provider | Delegated to provider flows | Lower | Fast storefront prototypes |
| UI-only shadcn builds | Developer-defined | You build it yourself | You build it yourself | Variable | Design systems and custom experiments |
Prostore is less open-ended than a headless commerce engine, but that is the point. It is more opinionated, easier to trace end to end, and much closer to a complete working model of how a store behaves.
ProStore is a free, open-source modern ecommerce platform developed by Brad Traversy, designed to help developers build full-featured online stores with a focus on clean architecture and user experience.
Why This Is a Strong Blueprint for Learning
The best thing about Prostore is not that it uses the latest stack. It is that the stack is arranged around a real business problem, and every layer has a reason to exist.
If you want to study how modern Next.js apps can handle identity, state, validation, and checkout without scattering the logic across half a dozen services, this is a useful map. It is a teaching project, but it behaves like a serious one.