Limen and the End of Prompt-Based Security
Why deterministic middleware, not better system prompts, is the only way to safely give autonomous agents access to your production database.
- Limen secures AI agents by moving authorization logic entirely out of the LLM's context window.
- It functions as deterministic middleware that evaluates Model Context Protocol tool calls against hard-coded PostgreSQL rules.
- Bidirectional channels allow the system to pause execution and request human-in-the-loop approval via WhatsApp or Slack.
The Agentic Blast Radius
Autonomous agents are increasingly being handed the keys to production databases and live APIs. The prevailing security model relies on system prompts and secondary LLMs to act as guardrails. Developers instruct the model to behave, hoping it follows directions when parsing user input.
This approach is fundamentally flawed. Placing security rules inside the same non-deterministic environment it is trying to protect creates an inevitable vulnerability to prompt injection and hallucination. When an agent holds your Stripe API keys, a single hallucination can drain an account.
The Key Outside the Thief's Head
Limen introduces a paradigm shift by stripping the agent of its authority. It treats the LLM purely as a reasoning engine, completely isolating it from the actual execution of tasks. The system is designed around the philosophy that the lock must be entirely inaccessible to the potential thief.
The rules governing what an agent can and cannot do live in a PostgreSQL database, managed via TypeScript and Drizzle ORM. Because these rules exist outside the LLM's context window, they cannot be bypassed through clever prompting or unexpected edge cases.
The Deterministic Proxy
Architecturally, Limen sits directly between the Model Context Protocol (MCP) and the target APIs. Every tool call initiated by the agent is intercepted by this Node.js middleware layer before it reaches the outside world.
Before any execution occurs, Limen evaluates the request against its deterministic ruleset. If an agent tries to execute a command that violates a policy, the proxy blocks it outright. The LLM never touches the target API directly.
Human-in-the-Loop 2.0
For sensitive actions that require human oversight, Limen abandons the traditional dashboard model. Instead, it utilizes bidirectional channels to integrate directly into existing workflows.
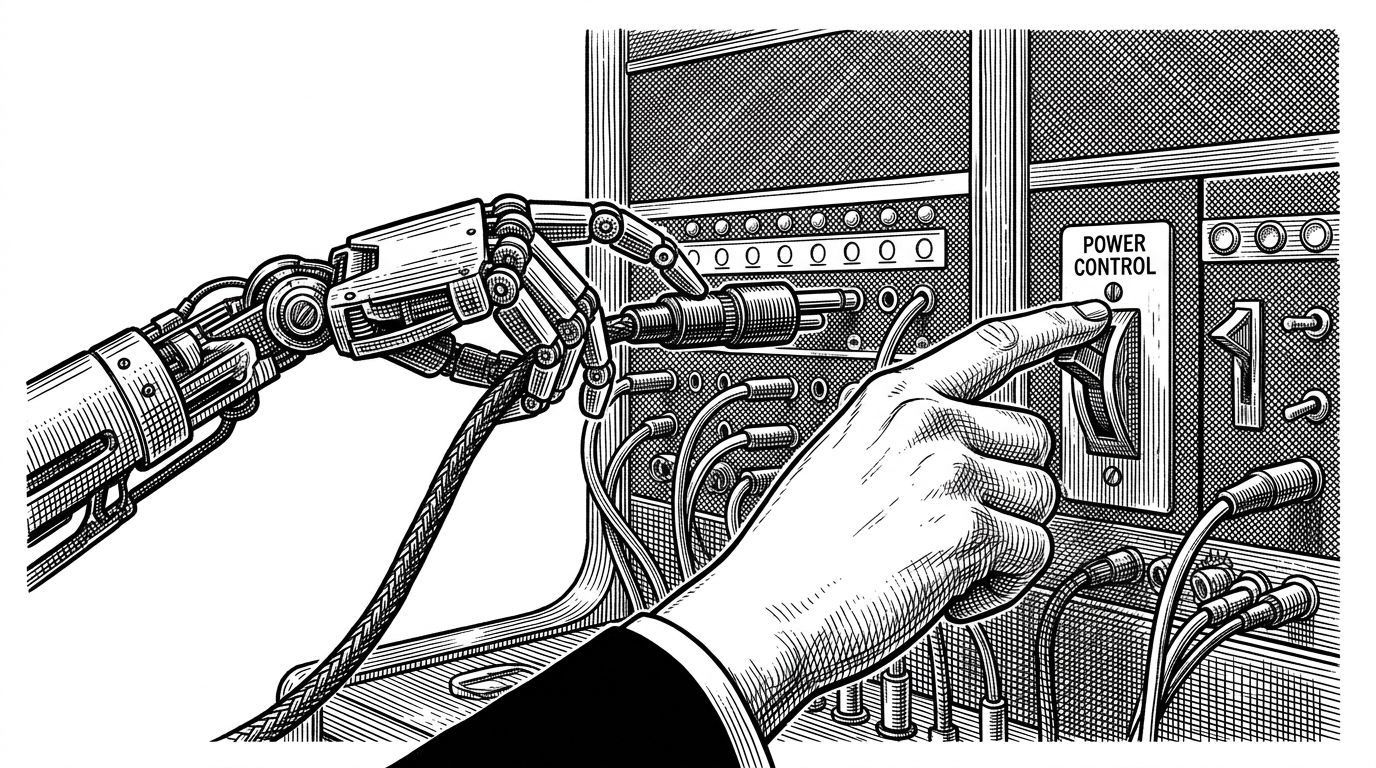
When a high-risk action is requested, Limen pauses the execution and pings an administrator on WhatsApp or Slack. A simple yes or no response dictates whether the proxy allows the packet to proceed to the target API. It transforms abstract security into a tangible, immediate decision.
Probabilistic vs. Deterministic Security
The distinction between prompt-based guardrails and Limen's middleware is the difference between asking an agent to behave and physically preventing it from misbehaving.
| Feature | Prompt-Based Guardrails | Limen Middleware |
|---|---|---|
| Execution Environment | Inside LLM Context Window | Node.js and PostgreSQL |
| Failure Mode | Hallucination or Bypass | Strict Denial |
| Vulnerability | Susceptible to Prompt Injection | Immune to Prompt Injection |
| Auditability | Reading chat logs | Querying a database table |