auth-api: The Anatomy of a Secure Login
How a comprehensive Node.js blueprint uses Express 5 and refresh token rotation to bridge the gap between fragile DIY scripts and expensive managed services.
- The auth-api repository serves as a production-grade blueprint for stateless Node.js authentication.
- It secures sessions by keeping access tokens in memory and rotating refresh tokens via httpOnly cookies.
- Strict environment validation prevents the server from booting without critical cryptographic secrets.
- Upgrading to Express 5 eliminates tedious manual promise rejection handling in the middleware pipeline.
The DIY Authentication Trap
Authentication is a solved problem that developers continually solve badly. The ecosystem forces a harsh choice. You can pay exorbitant fees for managed SaaS like Auth0, wrestle with complex enterprise monoliths like Keycloak, or fall into the DIY trap of wiring together low-level libraries.
Every time I start a new Node.js backend, authentication ends up being the most repetitive and fragile part of the project.
The auth-api repository by sayyedaaman2 is not a massive new framework trying to disrupt the industry. It is a highly opinionated reference implementation. By dissecting this repository, we expose the anatomy of proper refresh token rotation and the advantages of modern Node.js practices.
The Refresh Token Dance
The most complex part of stateless authentication is maintaining stateful security. The repository tackles this using a dual-token strategy found in controllers/user.controller.js. Access tokens are short-lived and passed via Authorization headers. They belong strictly in client memory.
Refresh tokens are long-lived and dangerous. The application stores them in the database and delivers them to the client via httpOnly cookies. When an access token expires, the refresh endpoint validates the secure cookie against the database and issues a new pair. This creates a sliding session that can be revoked server-side.
Fail-Fast Security and Express 5
A secure application must refuse to run if its environment is compromised. In config/server.config.js, the developer implemented a fail-fast mechanism. If critical secrets like the JWT signature key are missing, the process throws an immediate error.
The project also adopts Express 5.1.0. This major version upgrade fundamentally changes error handling. Express 5 automatically handles rejected promises in routes and middleware. This eliminates the need to manually wrap every asynchronous database call in boilerplate try-catch blocks.
The Admin-First Pattern
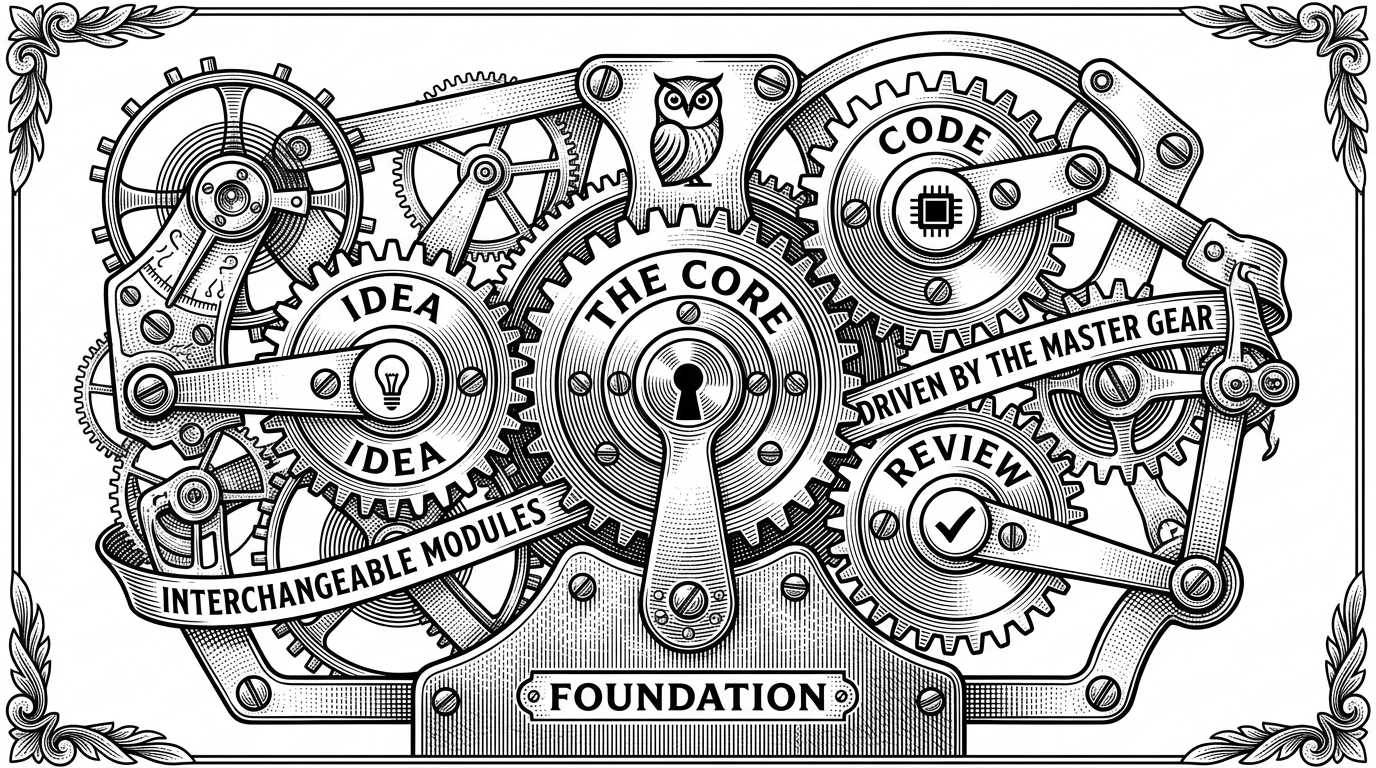
Bootstrapping a new system often presents a chicken-and-egg problem for role-based access control. The utils/init.js logic solves this by automatically seeding a default admin user on the first run. This ensures the system is never locked out upon deployment.
The Boilerplate vs. The Ecosystem
Choosing the right authentication strategy depends entirely on a team's budget, timeline, and data sovereignty requirements. A reference boilerplate sits uniquely between bare libraries and managed services.
| Approach | Setup Time | Data Ownership | Cost at Scale |
|---|---|---|---|
| Raw Libraries (Passport.js) | High | Complete | Low |
| Managed SaaS (Auth0, Clerk) | Low | Vendor Lock-in | Very High |
| Modern Frameworks (Better Auth) | Medium | Complete | Low |
| The Blueprint (auth-api) | Low | Complete | Low |