Md Shariar Shanaz Shuvon
Building open-source security infrastructure for the AI era. CEO @Awarexone
Explained projects
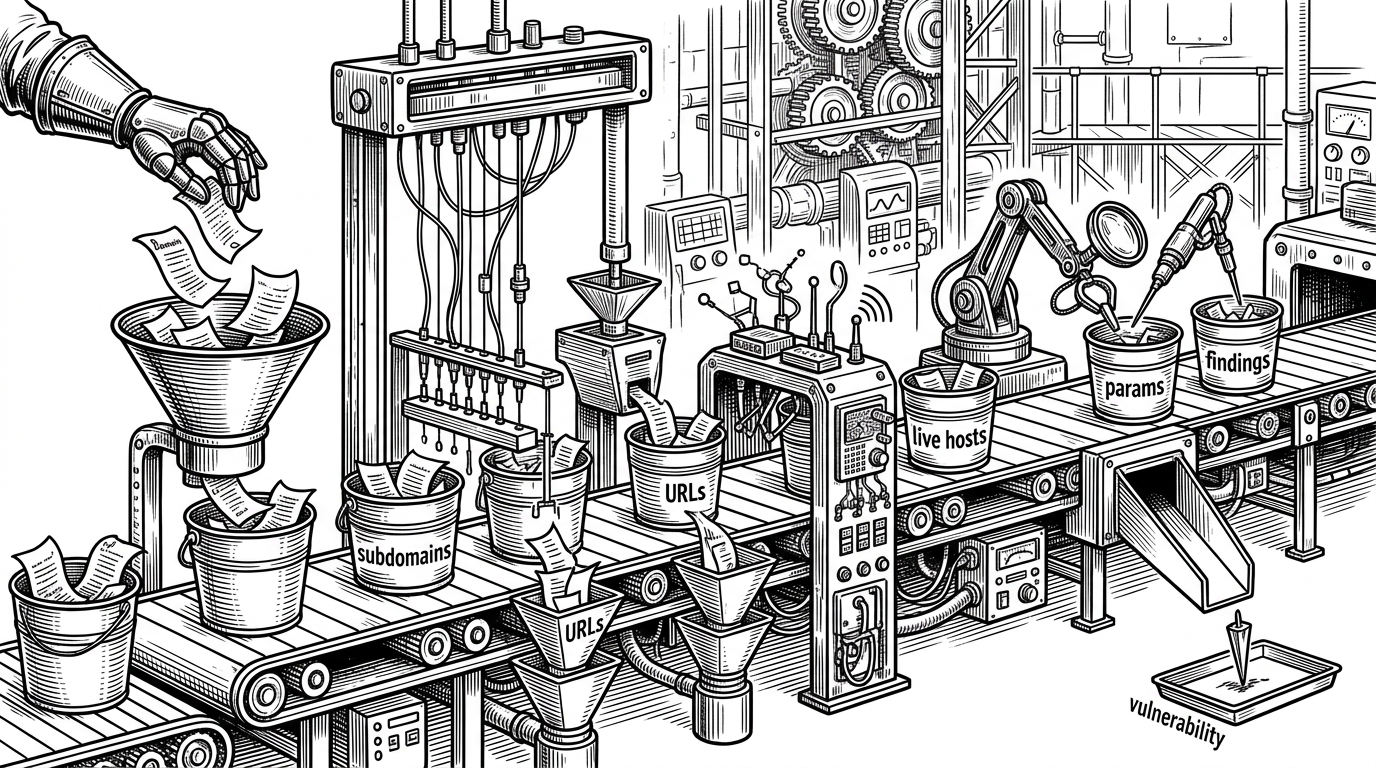
`full-hunt-pipeline`: The Bash Glue That Turns Recon Into a One-Command Workflow
A compact shell orchestrator that chains subdomain discovery, content hunting, and vulnerability scanning into a file-driven bug bounty pipeline, with quick mode and authenticated testing built in.
bug-bounty-installer: claude-bug-bounty: The bug bounty harness that makes Claude ask for proof
A Claude Code wrapper with agents, commands, memory, and proxy visibility, built to move from recon to report without skipping the evidence.
`ai-copilot-probe`: The Burp Suite for AI copilots
A tiny Python tool that fingerprints what an embedded assistant can see, what it can do, and whether its context layer leaks data across permission boundaries.
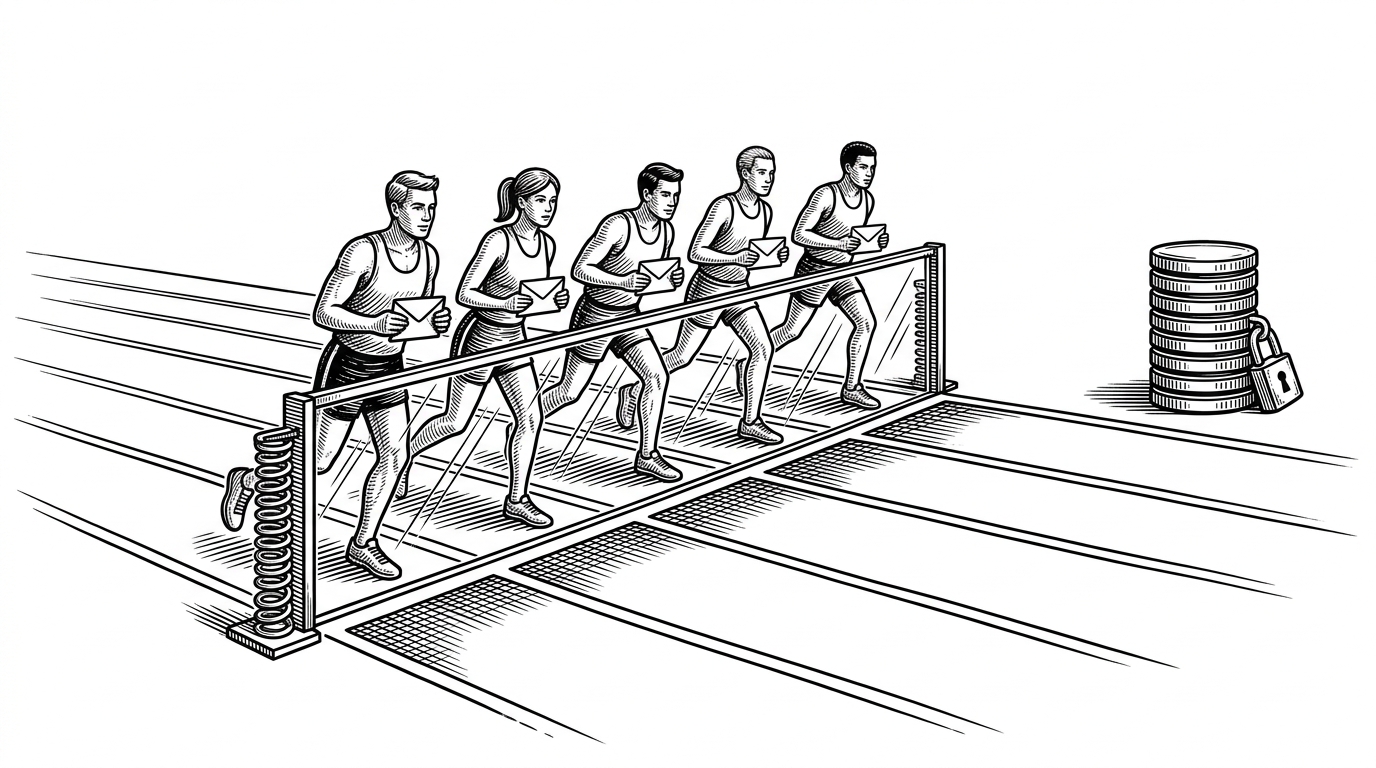
`shuvonsec/race-condition-tester`: The Small Python Script That Makes Threads Hit All at Once
A zero-dependency race-condition tester for bug bounty work, built around one idea that matters: synchronize every request, then let the server blink first.
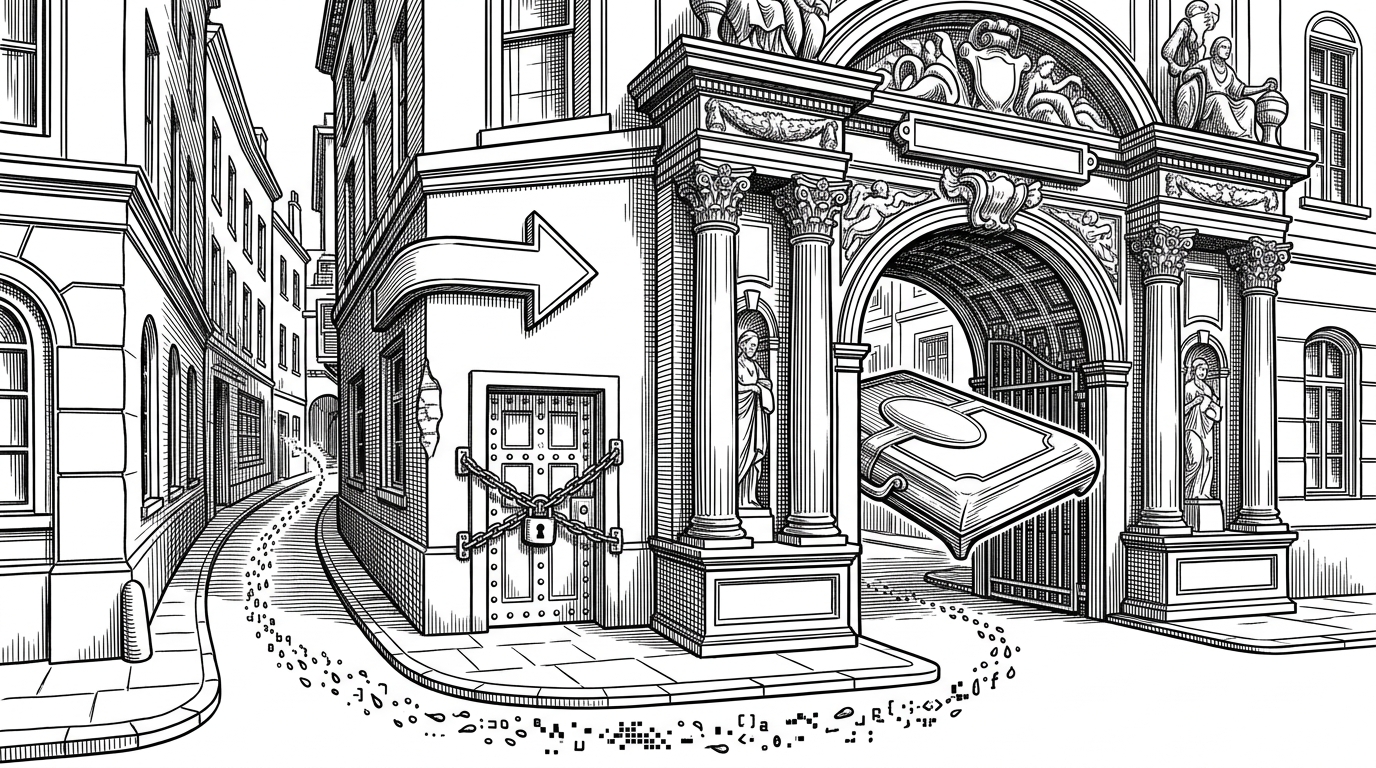
Inside shuvonsec/nextjs-ssrf-poc: the Next.js image optimizer trap that turns redirects into data leaks
A tiny local lab shows how an allowlisted image URL, a trusted redirect, and BMP passthrough combine into a much nastier SSRF than a blocked request.
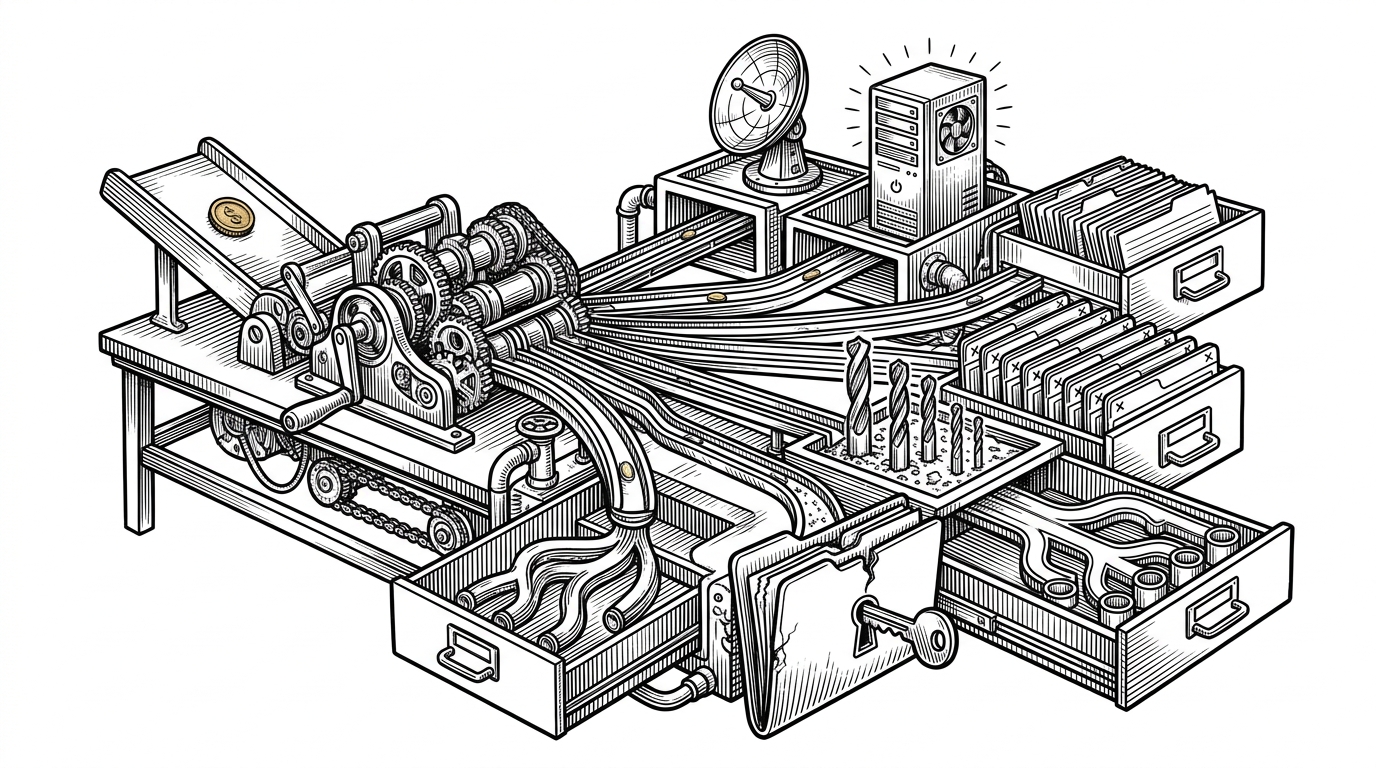
recon-engine: The Bash Script That Turns One Domain Into a Recon Dossier
Seven phases, graceful degradation, and a practical way to map attack surface without a heavyweight platform.
The Zero-Dependency Hunter: Unpacking shuvonsec/graphql-mutation-idor
How a minimalist Python script abandons external libraries to automate the discovery of complex logic flaws in modern GraphQL APIs.
Compiling the Hacker's Intuition: Inside shuvonsec/web3-bug-bounty-hunting-ai-skills
How a strictly orchestrated collection of Markdown files turns generic LLMs into economically-aware Web3 security auditors.
The End of the Script Kiddie: Unpacking shuvonsec/claude-bug-bounty
How a Python harness, strict logic gates, and persistent memory turned Claude Code into an autonomous security researcher.
bug-bounty-runner: Beyond the Grep: Inside Shuvonsec's Autonomous Security Agent
How claude-bug-bounty bridges the gap between raw network packets and human-level vulnerability reasoning.
The Ghost in the Tokenizer: ai-copilot-payload-builder
How invisible Unicode "Sneaky Bits" turn benign documents into high-privilege AI exploits.
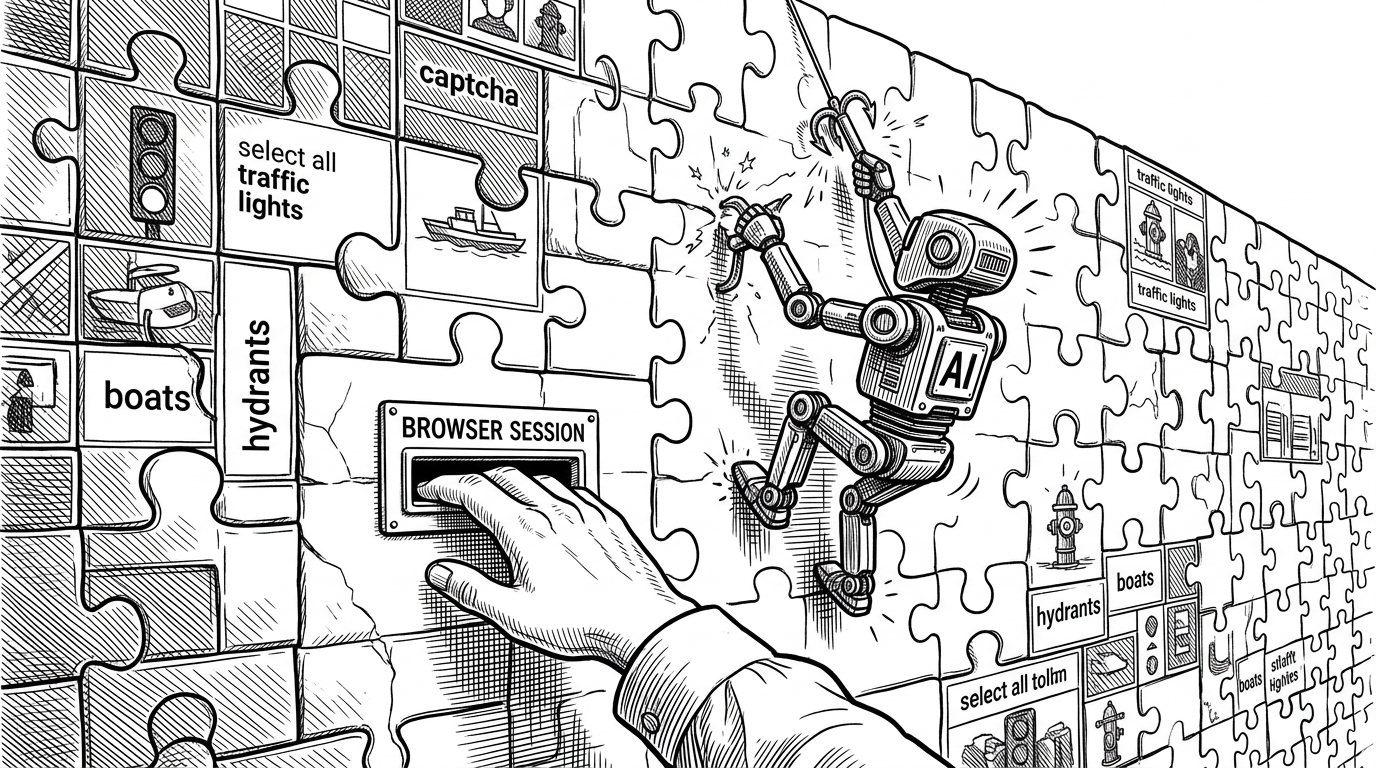
The Browser is the Bypass: How google-dork-runner Solves the Cat-and-Mouse Game of Search Recon
By abandoning the automated scraper in favor of a generated "Query Factory," this zero-dependency tool turns Google's bot detection into a non-issue.
oauth-security-tester: The Zero-Dependency Ghost in the OAuth Machine
How oauth-security-tester audits complex authentication chains using nothing but the Python Standard Library.
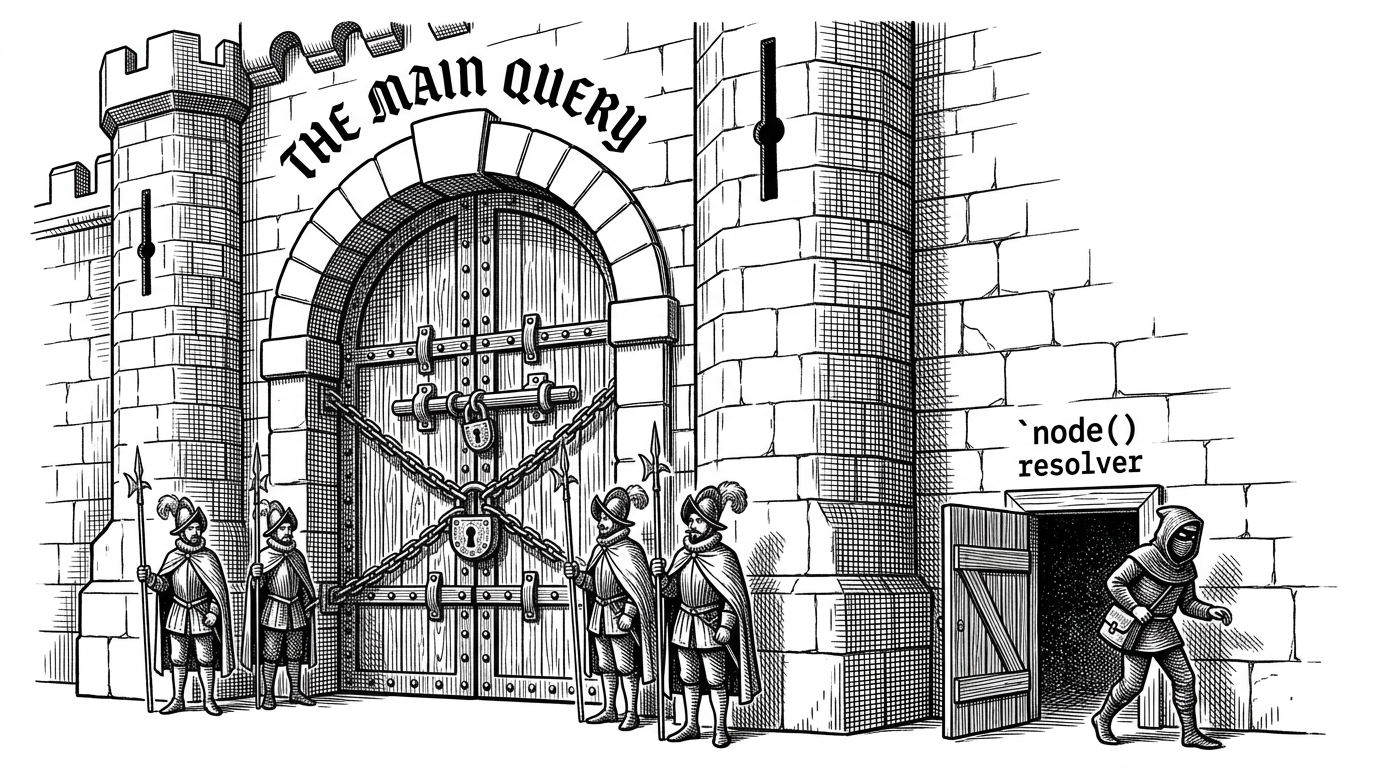
shuvonsec/graphql-idor-scanner: The Differential Engine for GraphQL Identity Theft
Moving beyond status codes to detect cross-tenant data leakage through automated session comparison.
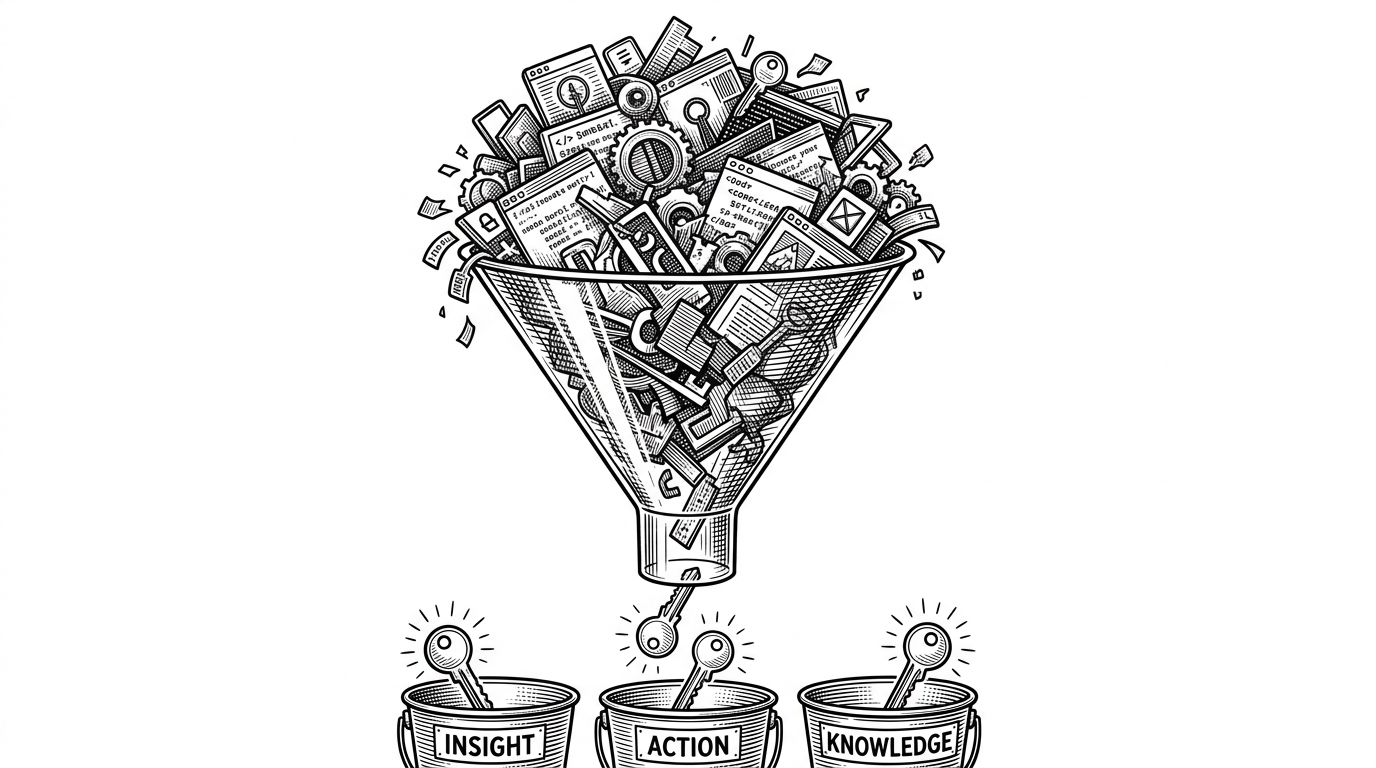
vuln-scanner: The Glue Code of the Bug Bounty
How vuln-scanner transforms raw reconnaissance into a prioritized hit list for elite security researchers.
ax-agent: AX: Building the Fireproof Kitchen for Autonomous Agents
How a security-first architecture and signature-based prompting are turning untrusted LLMs into reliable, always-on digital employees.
ax-ai-agent-mvp: Project AX and the Architecture of the Fireproof Agent
How a Trust Zone proxy and a 34k-line audit-first codebase solved the security crisis that nearly killed the autonomous assistant.
public-skills-builder: Mining the Collective Memory of Bug Hunters
How a specialized ETL pipeline transforms disclosed vulnerabilities into a high-signal Shadow-Brain for AI security agents.