E-commerce-Backend-System: The Checkout Engine That Refuses to Lie
A Spring Boot backend that treats inventory, identity, and schema changes as production problems, not tutorial afterthoughts.
- The repo’s real lesson is that checkout should behave like a consistency contract, not a controller method.
- Its strongest design choice is explicitness: Flyway, JWT, specifications, and DTO boundaries replace hidden framework magic.
- The project earns credibility by making failure safe, especially where stock, order creation, and cart state collide.
- This is not a commerce platform trying to be everything, only a believable backend that refuses optimistic shortcuts.
The moment e-commerce becomes hard
Most e-commerce tutorials make the same promise: products, carts, orders. This repo starts where those demos usually get vague, at checkout, because that is where a backend either tells the truth or quietly invents it. Once money and inventory are coupled, every shortcut becomes a bug with a receipt.
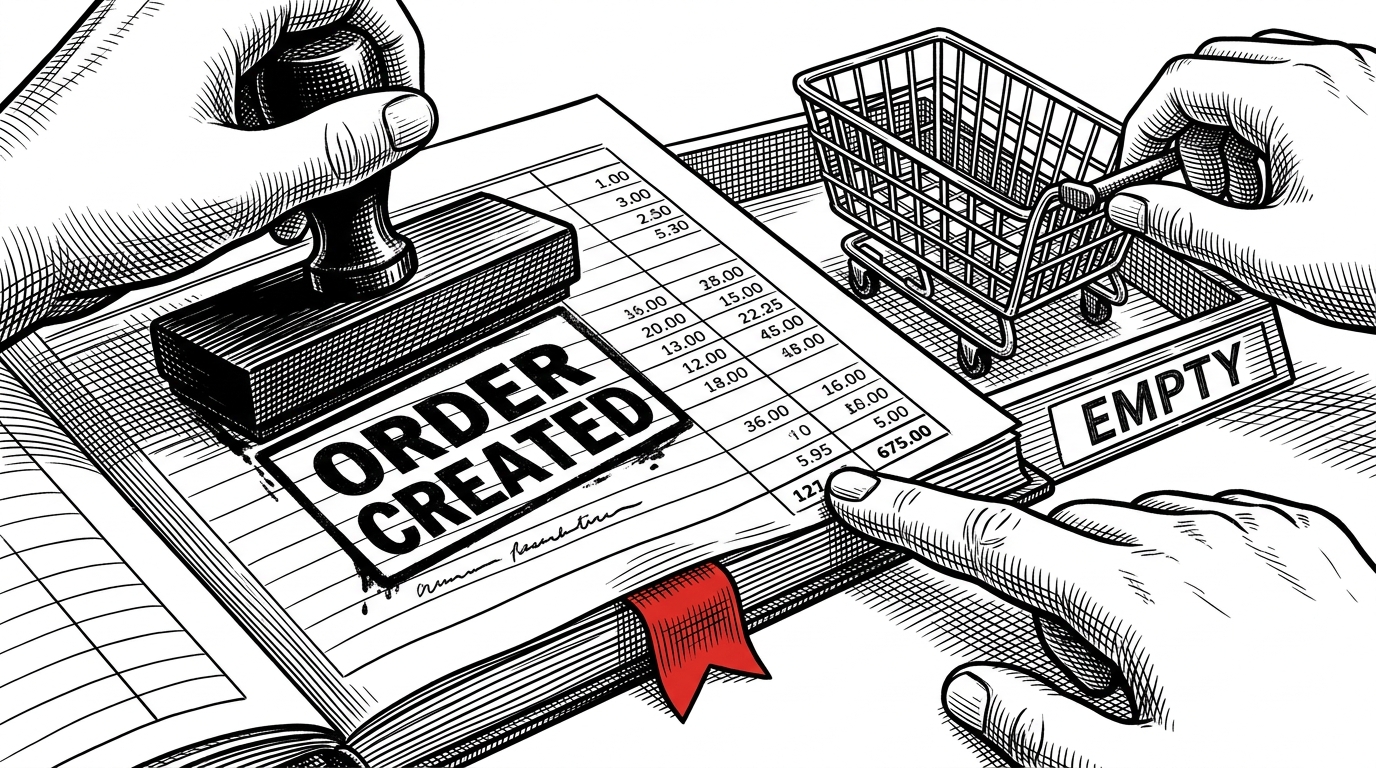
That is why the most interesting thing here is not the presence of an order API. It is the way the system treats checkout as an atomic sequence. If stock is missing, the order should not exist. If the order cannot be created, the cart should not be cleared. The whole chain has to move together.
Why this backend feels production-minded
The architecture is conventional on purpose. Spring Boot, JPA, Flyway, JWT, OpenAPI, and Maven give the project a familiar backbone, but the important part is how little it hides. DTOs stay separate from entities. Security is centralized. Database changes are versioned. That is the posture of something meant to be maintained, not merely run once.
Java 21 records tighten the API surface. Centralized configuration keeps environment concerns in one place. Flyway replaces schema guessing with ordered migrations. Even the bootstrap logic suggests deployment reality, because it can seed the system on first run instead of assuming a person will click around an admin panel forever.
Identity without session state
The security model is stateless JWT, which means the backend does not lean on server memory to remember who a user is. A filter extracts the bearer token, validates it, and reconstructs identity from claims. The payoff is operational simplicity. The trade-off is that the token boundary has to be crisp, because there is no session crutch to fall back on.
The cleaner design choice is how registration is handled. User creation and cart creation happen together inside a transaction, so identity and commerce state start in sync. That matters more than it sounds like. A user record without a cart is not a dramatic failure, but it is a bad one. The system avoids that mismatch from the first write.
Checkout as a consistency contract
`OrderServiceImpl.checkout` is the center of gravity. It validates the cart, checks stock line by line, computes totals, decrements inventory, creates the order, and clears the cart. The sequence is ordinary only if you ignore the stakes. The point is not that these steps exist. The point is that they are forced to succeed or fail as one unit.
That is what `@Transactional` earns here. It is not decorative. It is the boundary that keeps the repository from drifting into half-finished reality. A failed stock check should not leave a new order behind. A successful order should not preserve stale cart state. The annotation is doing architectural work.
The human value of that design is trust. A checkout that lies creates support tickets, reconciliation work, and inventory drift. A checkout that rolls back cleanly tells the rest of the system where the truth begins.
State machine view
Search that does not explode into repository sprawl
Dynamic filtering is handled with the Specification pattern, which is exactly the right answer when query combinations start multiplying. Category, price range, and text search do not need their own repository methods for every possible permutation. They need composable predicates that can be assembled at runtime.
That keeps the codebase smaller and the intent clearer. The repository layer stays focused, while the specification layer absorbs the combinatorial mess. It is a quiet sign of maturity. Instead of encoding the shape of every possible query in method names, the project builds a query only when the user asks for one.
| Concern | Tutorial CRUD backend | This repo |
|---|---|---|
| Checkout safety | Often assumes success and focuses on happy-path order creation | Uses a transactional sequence so stock, order, and cart state move together |
| Schema management | Commonly relies on auto schema updates | Uses Flyway migrations with explicit versioned changes |
| Filtering | Usually fixed repository methods for each search shape | Uses Specifications to compose filters dynamically |
| Authentication | Often a thin login demo | Uses JWT with a security filter and UserPrincipal bridge |
| Deployment readiness | Works locally, but keeps many assumptions implicit | Adds Docker, centralized config, and bootstrap logic |
| Scope | Good for learning endpoints | Good for learning how to make a backend believable |
Migrations, indexes, and the difference between toy and durable
Flyway is one of the clearest signals in the repository. It means schema changes are part of the codebase, not a side effect of booting the app. The index migration sharpens that signal further. Someone looked at the query paths and chose to optimize them intentionally instead of hoping the database would absorb the pain.
That is the difference between a demo and a backend you can hand to a team. A demo proves that tables can be created. A durable system proves that change can be tracked, rolled forward, and reasoned about after the fact. The repo leans hard toward the second category.
| Dimension | CRUD demo | E-commerce-Backend-System |
|---|---|---|
| Schema evolution | Implicit or ad hoc | Versioned Flyway migrations |
| Data access | Simple repositories everywhere | Specifications for composable search |
| State safety | Happy-path order flow | Transactional checkout with rollback discipline |
| Auth model | Often mocked or omitted | Stateless JWT security |
| Operational posture | Local-first assumptions | Bootstrap and deployment-aware configuration |
What this repo is really teaching
This project is not trying to out-Medusa Medusa or out-Shopify Shopify. It is teaching a narrower, more useful lesson: how to assemble a credible backend with the right seams. You need transactional order flow. You need explicit schema evolution. You need stateless auth. You need service boundaries that can be tested without the whole world attached.
That is why the repo feels more serious than many portfolios that look busier on the surface. It understands that commerce software is mostly about reducing ambiguity. When the system is honest about failure, it becomes easier to trust its success.
| Question | Typical platform | This repo |
|---|---|---|
| What is it for? | A full commerce ecosystem | A focused backend template with strong guarantees |
| What is the hardest part? | Scale, extensibility, ecosystem | Correctness at checkout |
| What is the main value? | Breadth of features | Engineering discipline |
| Who should study it? | Teams building commerce products | Developers learning how to make backend state dependable |