roots/allow-svg: The WordPress Plugin That Treats SVG Like a Security Boundary
A zero-config Roots plugin lets WordPress accept SVG uploads by rejecting suspicious files before they ever reach the Media Library.
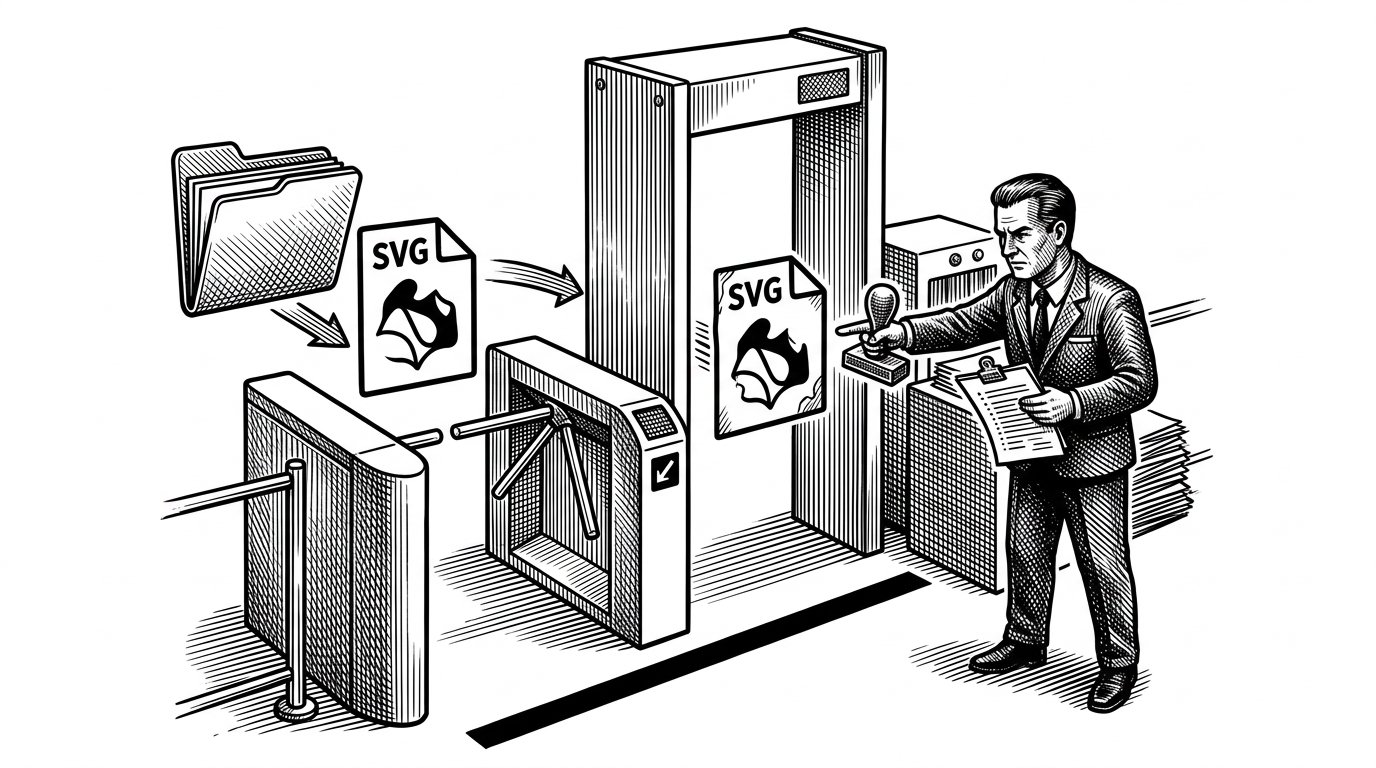
- roots/allow-svg treats SVG uploads as a policy decision, not a feature request, and its whole design revolves around refusing suspicious files early.
- The plugin’s narrow scope is the point: zero settings, zero production dependencies, and a small audit surface make it easier to trust.
- Its real strength is not just validation, but the discipline of testing the threat model with malicious fixtures and end-to-end coverage.
- In a legacy platform, modern PHP and strict CI can matter as much as the security logic itself.
WordPress has always had an awkward relationship with SVG. The format is useful, compact, and scalable, but it is also XML. That means an SVG can carry executable behavior, not just pixels. For a CMS that has spent years avoiding native support, the problem was never “how do we let it in,” but “how do we keep it from becoming a payload?”
We’re excited to introduce Allow SVG, a minimal, security-first WordPress plugin that enables SVG file uploads with zero configuration.
SVG uploads were never really about images
That distinction is the whole story. A PNG is a bitmap. An SVG is code-shaped content that browsers interpret. If the file contains scripts, hostile entities, or embedded foreign markup, the risk is no longer theoretical. It is the reason WordPress core has stayed cautious for years.
Most SVG plugins respond by adding more machinery: a settings screen, a sanitizer, maybe a few convenience features. `roots/allow-svg` goes the other way. It makes one decision well. If the file looks dangerous, it does not get uploaded.
Roots turns the question into a gate
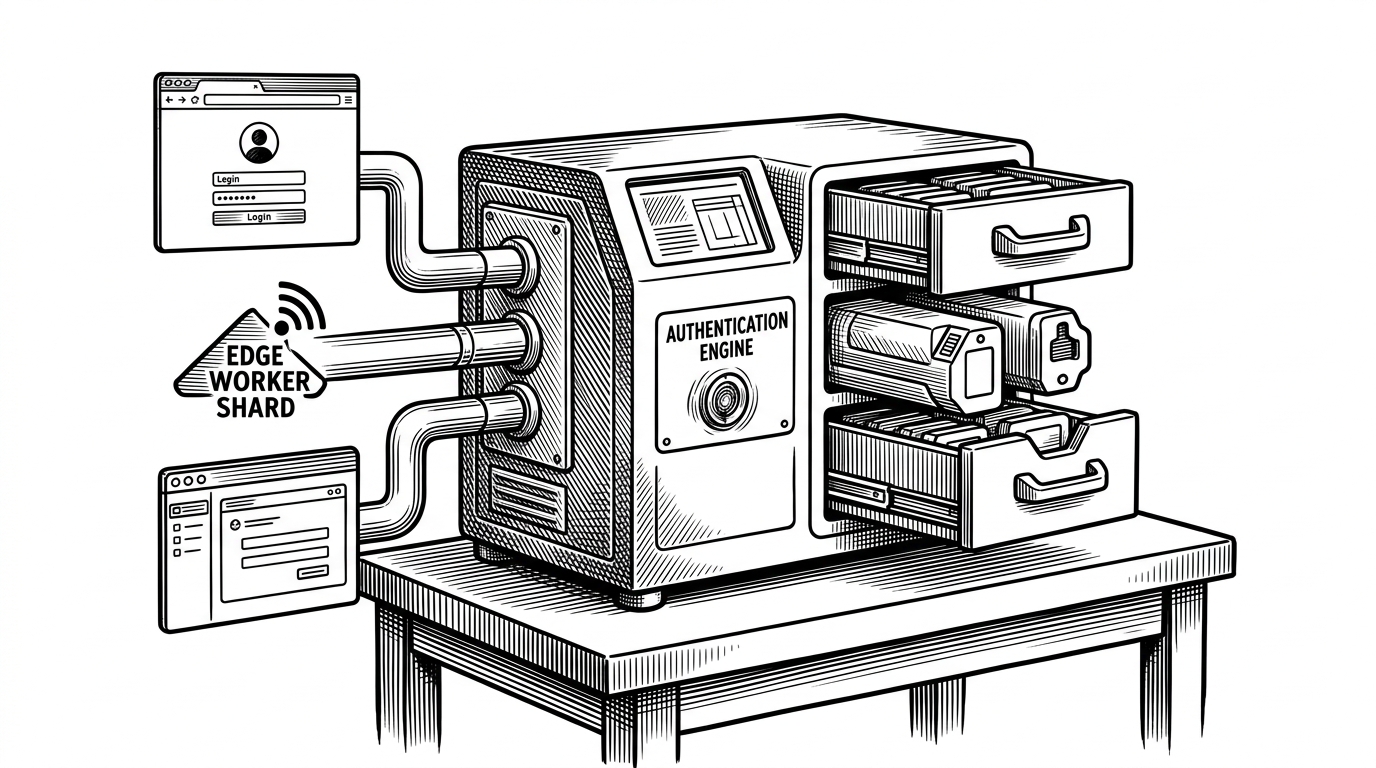
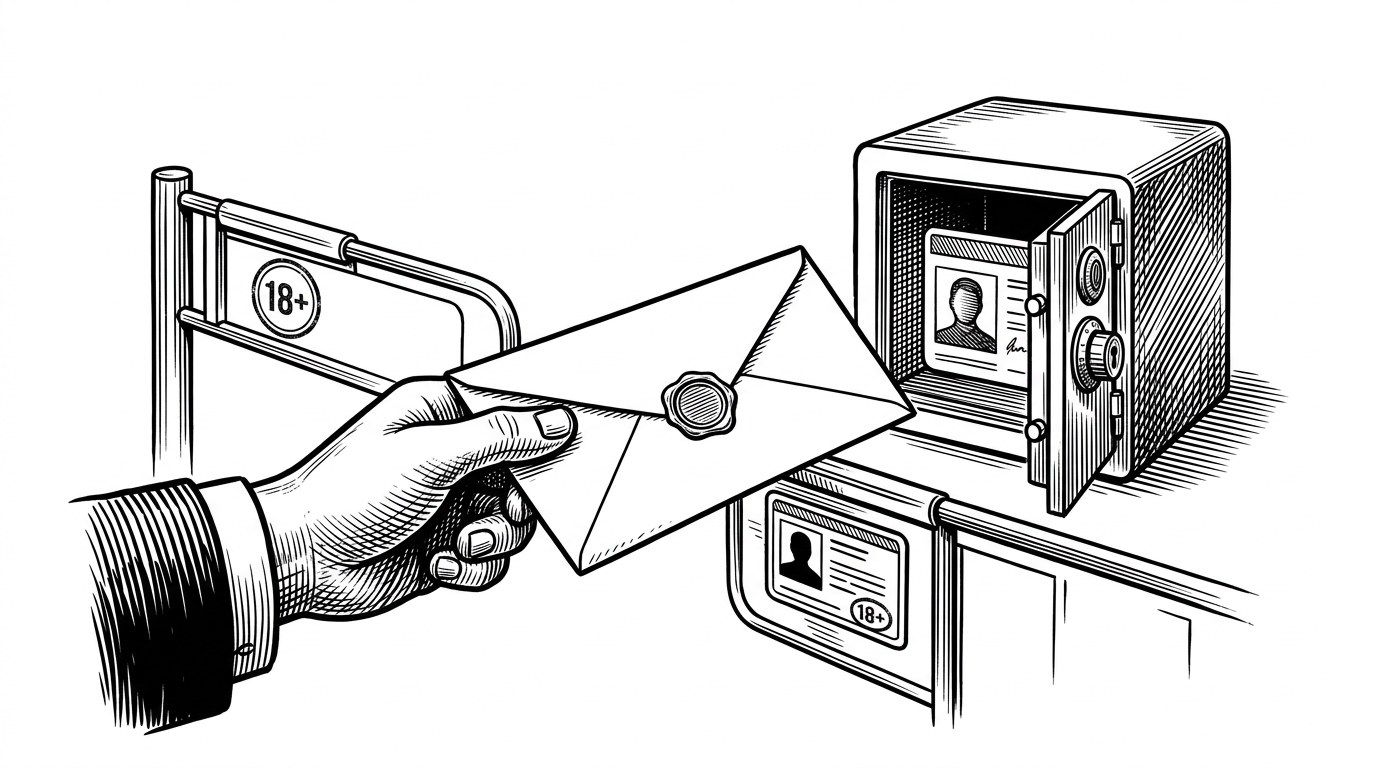
The plugin’s thesis is blunt. It is not trying to repair broken SVGs or massage risky ones into safety. It sits in the upload path and acts like a checkpoint. Clean files pass. Suspicious files are rejected before they reach the Media Library.
That matters because the upload boundary is the only place where WordPress can still make a clean yes or no decision. Once a malicious file is stored and distributed, the platform is already downstream of the mistake.
What the validator is actually looking for
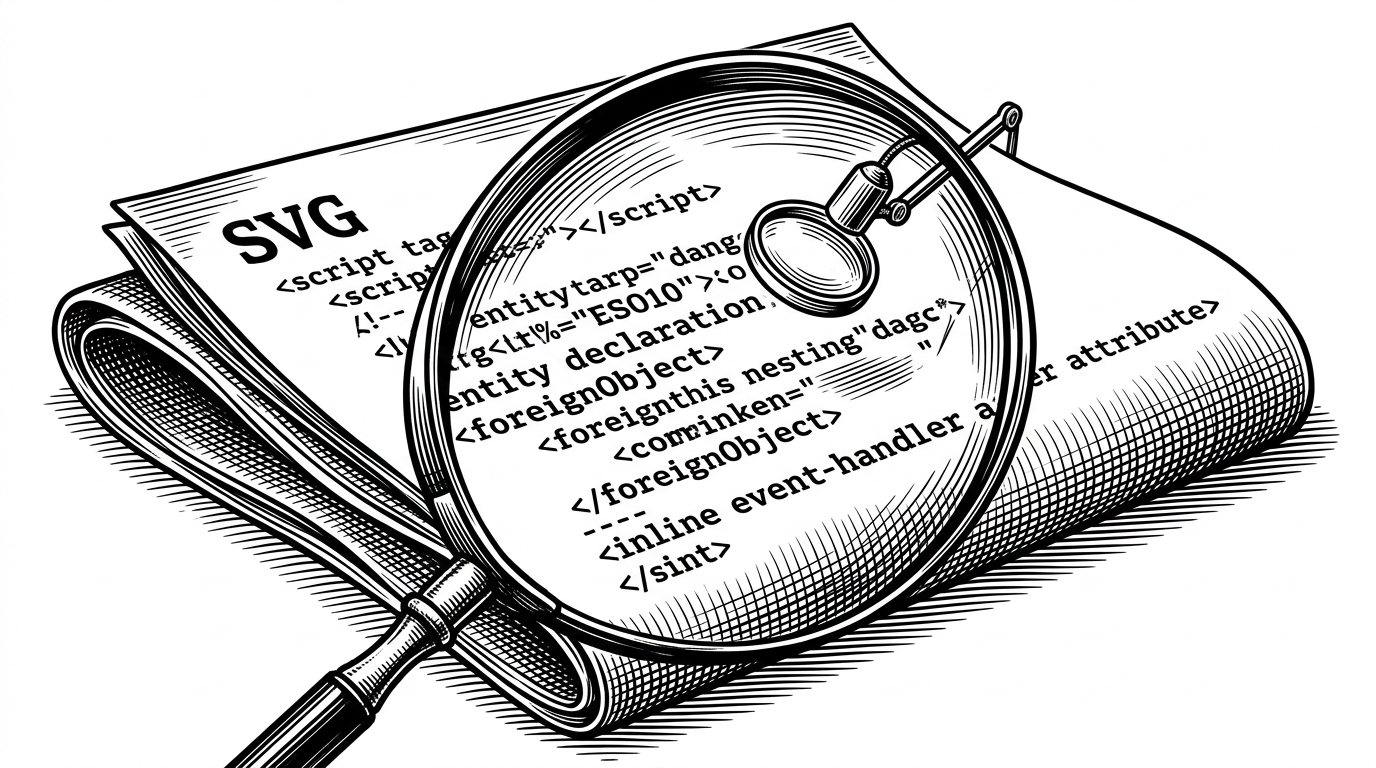
The interesting part is not just that the plugin checks for bad SVG. It checks for classes of abuse that matter in XML. Script tags are obvious. Inline event handlers are obvious. But the list also reaches into `DOCTYPE`, `ENTITY`, `foreignObject`, namespaced variants, and obfuscation tricks that try to hide hostile behavior in plain sight.
That makes the implementation feel more like a threat model than a convenience layer. The file is not being beautified or cleaned. It is being interrogated.
That design keeps the plugin auditable. There is no hidden remediation step, no background rewrite, no second system deciding what “safe enough” means after the fact. The trade-off is clear too: a deny-first system can reject some legitimate files if they resemble hostile ones. Roots is choosing certainty over convenience.
Why deny-first beats sanitize-first
| Approach | Config | Security posture | Dependencies | Developer experience | Risk of false positives |
|---|---|---|---|---|---|
| Deny-first validation | None | Rejects suspicious files before upload | Zero production dependencies | Very simple | Moderate |
| Sanitize-first filtering | Often a settings page | Attempts to clean files after upload | Usually heavier libraries | More flexible | Lower, but with hidden transforms |
| Block SVG entirely | None | Eliminates SVG risk by forbidding the format | None | Safest but least useful | None |
This is why the comparison is philosophical as much as technical. Sanitizing says, “I can make this usable.” Deny-first validation says, “I am not going to guess.” For a file format that can carry executable structure, that is a strong and defensible boundary.
The test suite is the real product
The fixtures tell you what the maintainers fear. Malicious XXE samples. Entity bombs. ForeignObject payloads. Corrupted XML. That test corpus is more than QA. It is a documented attack surface.
A WordPress plugin that enables SVG uploads with validation to block malicious files.
That matters because security plugins are often vague about their coverage. Here, the threat model is visible in the repository itself. The tests are not just proving that SVG uploads work. They are proving which failures must never slip through.
How it compares to the rest of the SVG plugin world
| Plugin stance | Primary move | Trade-off | Best for |
|---|---|---|---|
| roots/allow-svg | Validate and reject suspicious files | Less forgiving, fewer features | Teams that want a narrow security gate |
| Sanitize-first SVG plugins | Strip dangerous content after upload | More moving parts and hidden transforms | Sites that want convenience and broader compatibility |
| Feature-heavy SVG plugins | Add UI and extra rendering options | More surface area than the upload problem really needs | Users who value configuration over minimalism |
| No SVG support | Disable the format entirely | Maximum safety, minimum usefulness | Organizations that can live without SVG |
`allow-svg` does not try to win every category. It wins the one that matters to its audience: trustability. The plugin is small enough to inspect, strict enough to matter, and opinionated enough to avoid pretending that every SVG can be made safe.
A modern PHP plugin in a legacy ecosystem
The other quiet story here is implementation discipline. This is a WordPress plugin, but it reads like a modern PHP project. Strict types, PHP 8.2, GitHub Actions, Playwright, and no production dependencies all suggest the same thing: the team is optimizing for maintainability, not breadth.
That is a useful reminder. In older ecosystems, modern engineering practice can be the differentiator. Security is not only about the validator logic. It is about how easy the code is to reason about, test, and keep honest over time.
Sources: roots/allow-svg, Roots announcement, Roots discourse thread. For a close read on the implementation and tests, the repository itself is the best source.