MEV-Arbitrage-Bot: The Self-Custody Bot That Outsources the Hard Part
A Solidity vault, an off-chain trigger loop, and a deceptively simple promise: make arbitrage feel copy-paste friendly without turning the user into passive infrastructure.
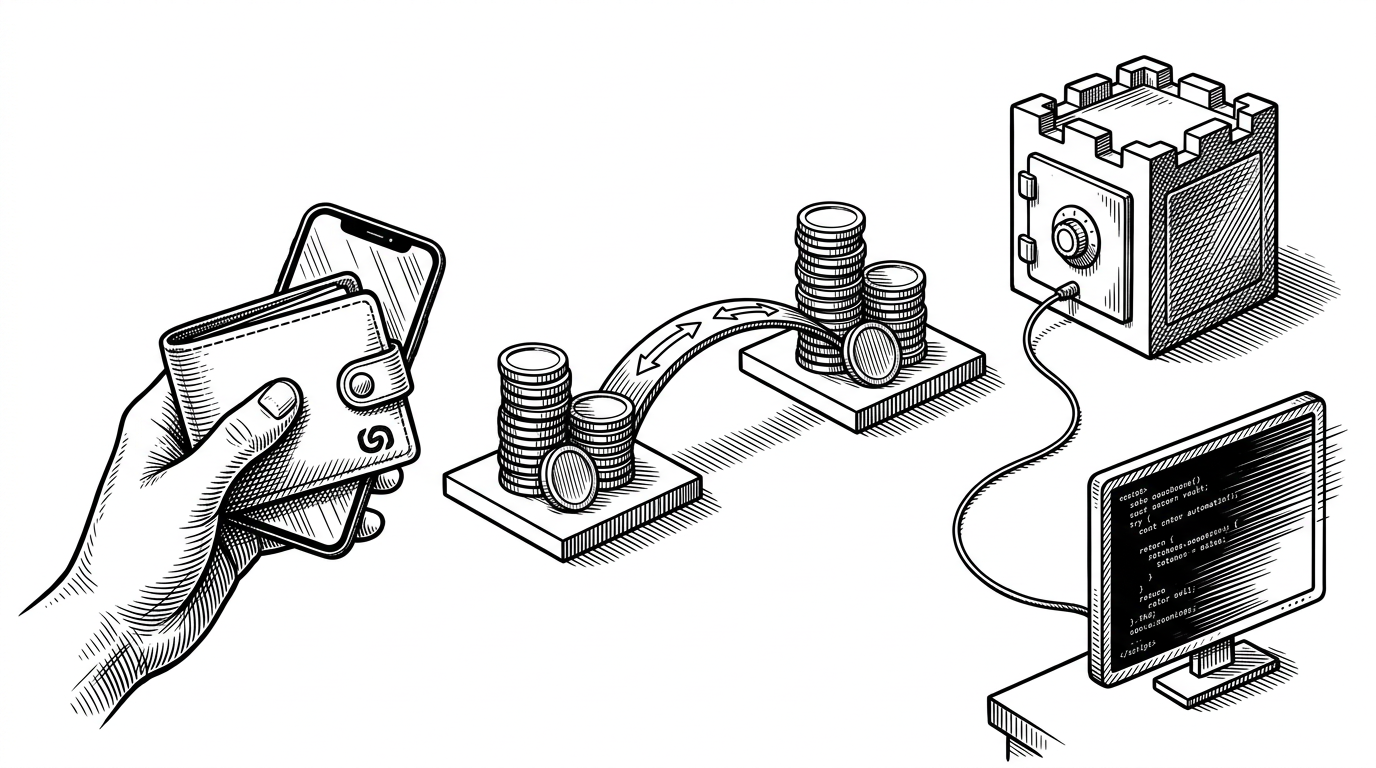
- MEV-Arbitrage-Bot is less a bot than a split system, with a small on-chain vault and a larger off-chain decision layer that decides when a trade is worth sending.
- Its real novelty is the trust model, because the user keeps custody while relying on external automation to detect, simulate, and trigger execution.
- The contract is deliberately narrow, using ownership checks, whitelists, and a reentrancy lock to act as a constrained execution surface rather than a full trading brain.
- The repo is approachable by design, but that accessibility comes with hardcoded assumptions and a lot of trust in tooling the user does not fully control.
The Bot That Is Really a Contract Plus a Workflow
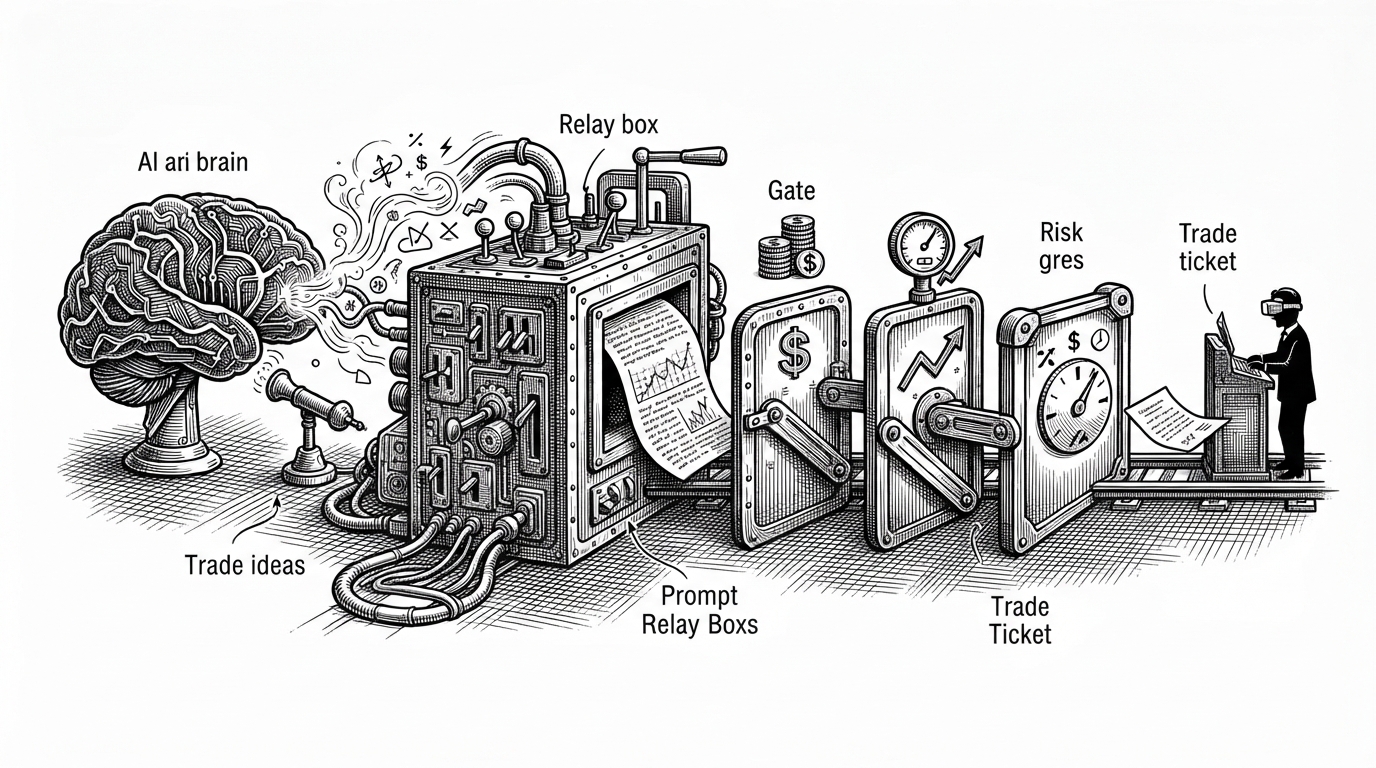
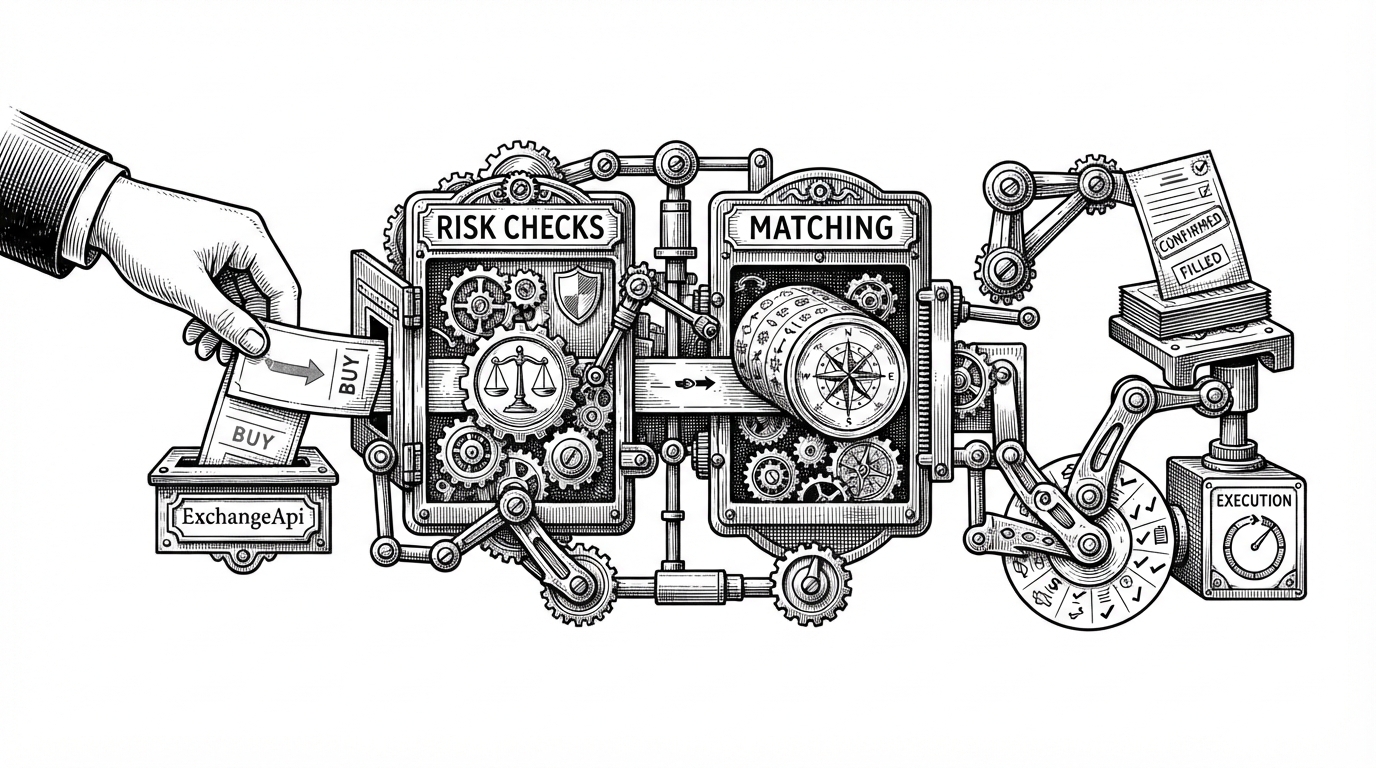
The repo presents itself like a trading bot, but the architecture tells a different story. The contract holds funds and executes swaps, while the monitoring and trigger logic live outside the chain in a separate automation layer.
That split is the whole thesis. The on-chain piece is small enough to inspect, but the system only works if you trust the off-chain workflow to notice an opportunity, simulate it honestly, and decide when to pull the trigger.
An arbitrage bot is a smart contract connected to an external automation script that controls its operation.
Why Self-Custody Is Doing a Lot of Work Here
The README leans hard on self-custody language, and the claim is technically true in a narrow sense. The user deploys the contract, funds it, and keeps ownership over withdrawals and execution permissions.
But the system still depends on a third-party interface and automation path to turn opportunities into transactions. That means the user owns the vault, yet still trusts an external layer to decide what counts as a valid trade and when the contract should move.
Repository voice: MIgHTy-alIeN/MEV-Arbitrage-Bot
The Contract Is Small on Purpose
The Solidity file is the center of gravity, but it is not a complete trading system. It is a guarded execution shell with ownership checks, token and router whitelists, a manual reentrancy lock, and a narrow set of functions for funding, withdrawing, and arbitrage execution.
That matters because the contract’s job is not to invent strategy. It simply limits who can move money, where swaps can go, and which external paths are allowed to touch the vault.
function executeArbitrage(address tokenIn, address tokenOut, uint256 amountIn) external onlyOwner nonReentrant {
    require(allowed[tokenIn] && allowed[tokenOut], "Token not allowed");
    require(allowedRouters[ROUTER], "Router not allowed");

    // swap logic routed through whitelisted DEX path
}

function depositEth() external payable onlyOwner {
    require(msg.value > 0, "No ETH sent");
}

function withdraw() external onlyOwner {
    payable(owner).transfer(address(this).balance);
}
The Clever Part Is the Simulation Loop
The repo’s smartest move is not the swap logic. It is the dry-run filter, where the automation layer uses eth_estimateGas before sending anything real.
That turns arbitrage into a funnel instead of a firehose. Most candidate trades die in simulation, which means the user avoids paying for transactions that were likely to revert or fail to clear the spread.
This is where the system feels practical. The off-chain script is not just watching the market, it is judging whether the trade survives a preflight check well enough to be worth the fee.
What This Repository Gets Right, and What It Hides
The design is approachable. A user can understand the deployment story without building a full MEV stack, and the on-chain surface stays small enough to audit quickly.
But the trade-off is obvious. Hardcoded router and WETH addresses narrow flexibility, and the off-chain layer introduces a trust boundary the README cannot erase with friendly deployment steps.
| Project | Trust model | Execution style | Best fit |
|---|---|---|---|
| MEV-Arbitrage-Bot | User-owned contract plus external automation | Remix-style deployment with off-chain triggers | Accessible entry point for exploratory users |
| Flashbots Searcher-Examples | Searcher-operated infrastructure with private bundle flow | Professional MEV pipeline | Users who want stronger anti-front-running posture |
| TypeScript / Hardhat arbitrage bot | Explicit dev tooling and visible control flow | Scripted monitoring and transaction orchestration | Builders who want transparency and testability |
| Rust arbitrage bot | Performance-first, low-latency engineering | Fast execution loop with tighter runtime focus | Teams optimizing for competitive speed |
The table says it plainly: this repo is optimized for accessibility, not institutional-grade MEV performance. That makes it interesting, but it also means the user should read every convenience as a design choice with a cost.
How It Compares to Serious MEV Tooling
Placed next to Flashbots examples, a TypeScript bot, or a Rust implementation, MEV-Arbitrage-Bot looks less like infrastructure and more like a guided workflow. That is not a flaw by itself, but it is a different category of tool.
The comparison is not about which project is better. It is about what each one expects the user to understand, and how much of the hard part it refuses to hide.
The Strange Signals in the Repo Metadata
The repo also leaves odd breadcrumbs. The LICENSE file is not a normal license text, and the surrounding metadata looks more like a generated or heavily templated project than a handcrafted one.
That does not prove bad intent, but it does justify caution. In a category where users are being asked to fund contracts and trust automation, metadata weirdness is not a cosmetic detail.
The maintainers may have built a genuinely useful teaching tool, or they may have wrapped a risky workflow in unusually polished packaging. Either way, the architecture is more revealing than the marketing copy.