mimic: The Tool That Turns Private API Traffic Into a Python Client
It intercepts mobile and web requests, extracts durable auth state, and uses an LLM to generate code that can replay the app’s behavior, then heal itself when credentials expire.
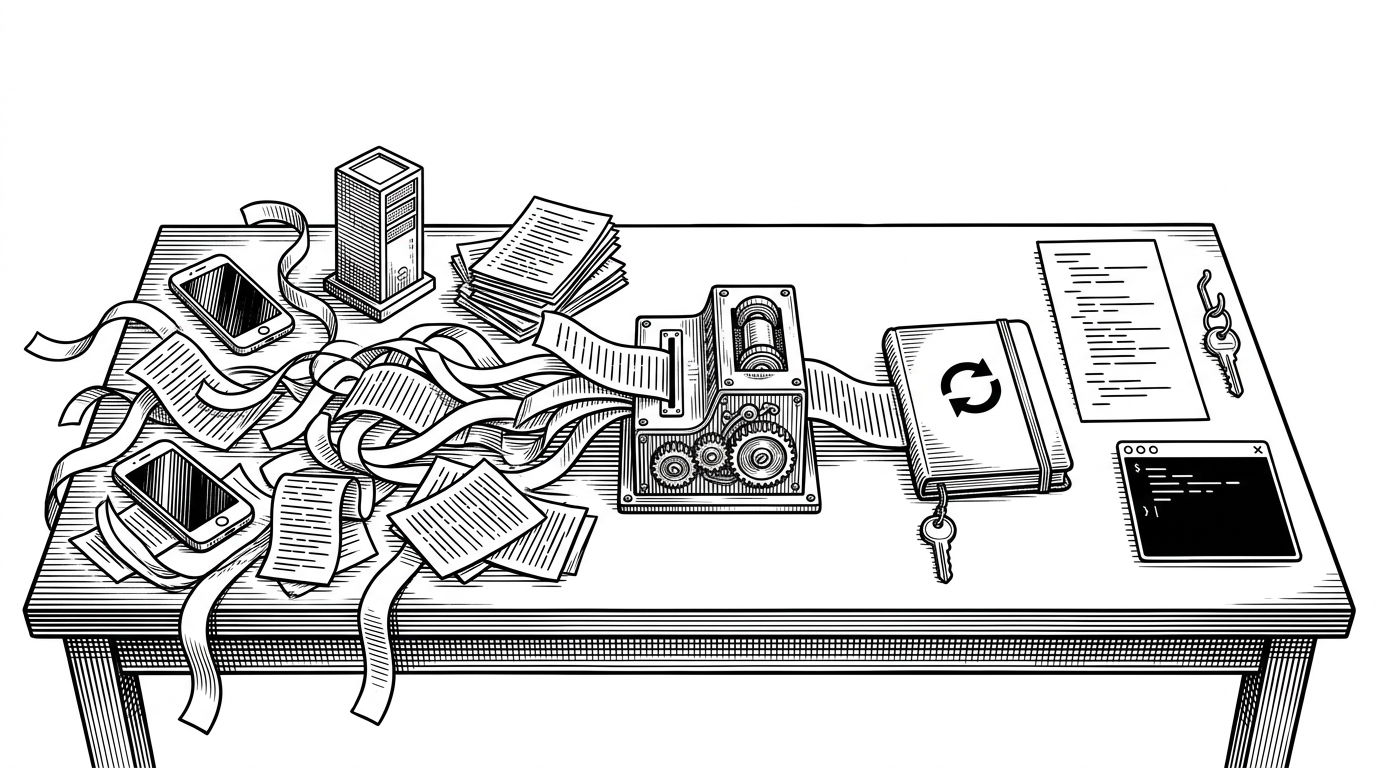
- mimic’s real novelty is not traffic capture, but the jump from captured requests to a reusable Python client.
- The generated client stays useful because it can refresh expired auth from the live capture layer and retry automatically.
- The project treats an LLM as a compiler stage, with traffic normalization and prompt shaping doing most of the heavy lifting.
- Its limits are structural: pinned apps, shifting auth schemes, and external AI tooling can all break the pipeline.
From Packet Sniffer to Python Library
Most proxy tools stop at visibility. `mimic` is trying to cross a line: it takes private API traffic and emits something you can edit, import, and keep using. That turns interception into a kind of compiler pass, where the output is not a trace, but a client.
That is why the project feels odd in a good way. The capture step matters, but the payoff is the generated library. It is the difference between reading the wire and shipping code.
Most apps authenticate every request with the same bundle of values: a bearer token, some device ids, a session id, cookies. They're stable across calls. Capture them once from a real request you made, and you can replay them on new requests to the same API.
The Core Bet: Most Apps Have a Stable Identity
The project rests on a practical hypothesis: many apps send the same identity bundle over and over. Bearer tokens, cookies, device identifiers, and `x-` prefixed metadata often stay stable enough to replay requests successfully. `mimic` leans into that reality instead of pretending every request is unique.
How the Generated Client Stays Alive
The smartest part of `mimic` lives in `session.py`. The generated client is not a thin wrapper around `requests`. It parses JSON, raises on failures by default, and when a request comes back with 401, it reaches back into the capture layer for fresh headers and retries.
That is the crucial move. A lot of tools can replay traffic once. Fewer can keep going after credentials age out. Here, the code generator and the runtime session layer are designed to cooperate, so the output behaves more like a living client than a disposable script.
How Traffic Becomes a Prompt
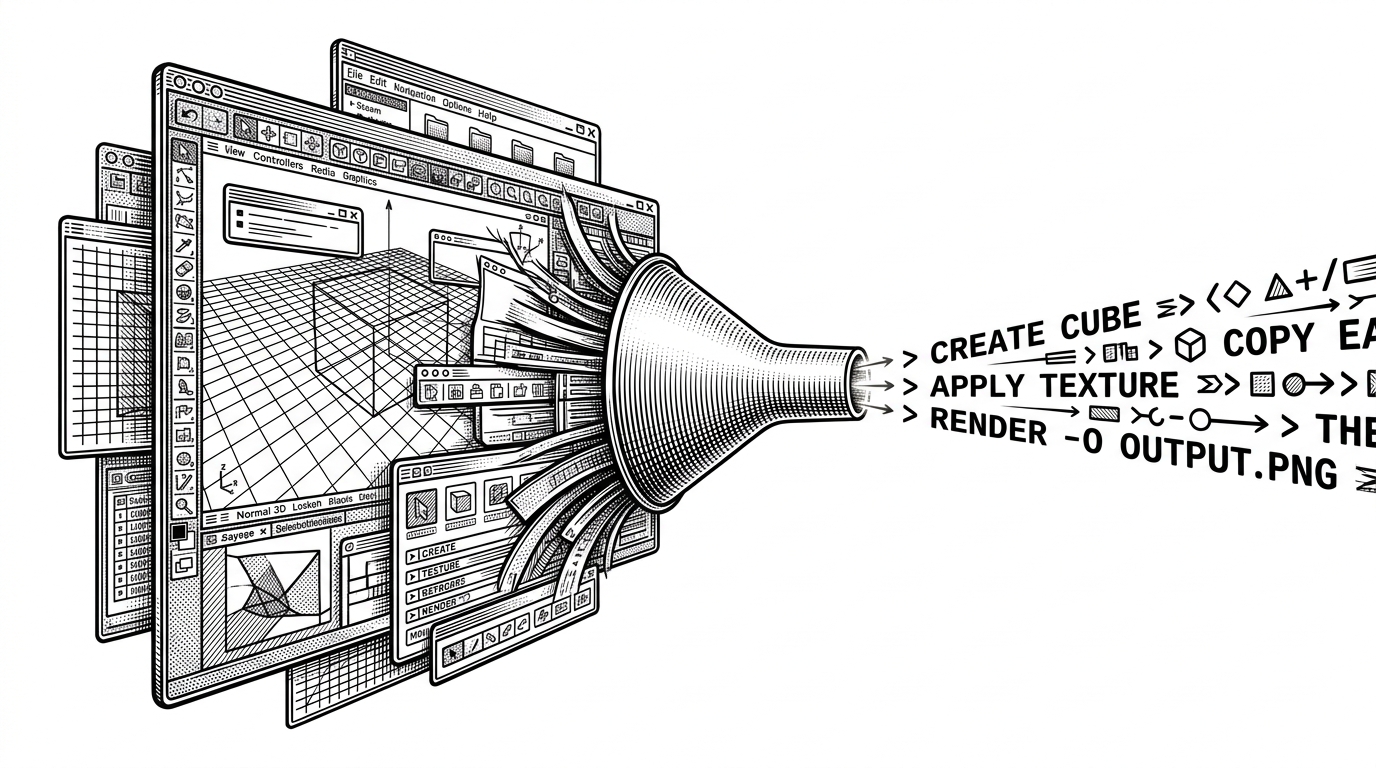
`mimic` does not feed raw network noise straight into an LLM and hope for the best. The traffic pipeline normalizes input from live proxying or HAR files, extracts endpoints, trims oversized bodies, and packages the result into a prompt that asks the model to produce readable code.
# Conceptual flow from the repository
flows = load_flows(source)
endpoints = normalize(flows)
endpoints = truncate_large_bodies(endpoints, limit=4000)
prompt = build_prompt(endpoints)
client_code = run_generator(prompt)
The design choice matters. The model is not acting like an oracle. It is one stage in a deterministic pipeline. The surrounding code decides what gets preserved, what gets dropped, and how the output should be shaped.
| Tool | What it gives you | What it does not give you |
|---|---|---|
| mitmproxy | Live interception and inspection | A reusable Python client |
| Postman / Insomnia | Manual replay and API organization | Automation from captured traffic |
| mitmproxy-mcp | AI access to live traffic for agents | A standalone human-editable library |
| mimic | Captured traffic plus generated client code | A general-purpose proxy UI |
Why SSL Pinning Is the Real Gate
Before code generation matters, interception has to work. That is why `unpin.py` exists. SSL pinning is the wall that blocks standard MITM flows in many mobile apps, so the bypass path is not a bonus feature. It is the entry fee.
mimic unpin
mimic record
mimic hosts
mimic gen <host>
The repo does not make pinning sound glamorous, because it is not. It is just the obstacle you have to clear before the interesting part can begin.
What mimic Is For, and What It Is Not
`mimic` sits in a narrow lane. It is not a replacement for mitmproxy, Charles, Postman, or Insomnia. Those tools help you inspect, replay, and document traffic. `mimic` tries to take the next step and produce a maintainable Python client for ongoing use.
| Tool | Primary mode | Output |
|---|---|---|
| mitmproxy | Inspect and intercept | Traffic view and scripts |
| Charles Proxy | Debug and replay | Manual session analysis |
| Postman / Insomnia | Organize and call APIs | Collections and requests |
| mimic | Compile traffic into code | Editable Python client |
That niche is the point. It fills the gap between seeing a private API and living with it in code.
The Limits of the Magic
- The generator depends on external AI CLI tools, so the pipeline inherits their fragility.
- Auth schemes change, and some apps use defenses that stable header capture cannot solve.
- Pinned apps still need an unpinning path before any replay can happen.
- The output is still only as good as the captured traffic and prompt shaping behind it.
The Ethics Are Part of the Design
`mimic` is interesting because it is useful and uncomfortable at the same time. It is built for personal automation, testing, and reverse engineering, which means it lives close to terms-of-service risk. That tension is not a side note. It is part of the product shape.
The project’s appeal is that it makes the user feel powerful without hiding the trade-offs. It gives you a path from private traffic to code, but it also asks you to think hard about what you are automating, and why.