Security & Supply Chain
Open-source security, dependency auditing, supply-chain safety, and agent guardrails
227 explainers
Security & Supply Chain
bug-bounty-installer: claude-bug-bounty: The bug bounty harness that makes Claude ask for proof
A Claude Code wrapper with agents, commands, memory, and proxy visibility, built to move from recon to report without skipping the evidence.
Security & Supply Chain
lunduke-retarded: GitHub Becomes a Compliance Ledger
A community tracker turns distro statements into a source-linked map of who will comply with OS-level age verification laws, and who will not.
Security & Supply Chain
`ai-copilot-probe`: The Burp Suite for AI copilots
A tiny Python tool that fingerprints what an embedded assistant can see, what it can do, and whether its context layer leaks data across permission boundaries.
Security & Supply Chain
`shuvonsec/race-condition-tester`: The Small Python Script That Makes Threads Hit All at Once
A zero-dependency race-condition tester for bug bounty work, built around one idea that matters: synchronize every request, then let the server blink first.
Security & Supply Chain
ethereum-lottery-app: The Lottery That Teaches Web3’s Hardest Lesson
A bare-metal Solidity project that looks simple, then reveals why on-chain randomness, access control, secret handling, and deployment are harder than they seem.
Security & Supply Chain
self-olympics: A Country Leaderboard That Knows Who You Are, Without Knowing You
Self-Olympics uses passport-backed zero-knowledge proofs, a Farcaster Frame, and a PostgreSQL nullifier ledger to make one-human, one-vote ranking feel practical.
Security & Supply Chain
Inside shuvonsec/nextjs-ssrf-poc: the Next.js image optimizer trap that turns redirects into data leaks
A tiny local lab shows how an allowlisted image URL, a trusted redirect, and BMP passthrough combine into a much nastier SSRF than a blocked request.
Security & Supply Chain
recon-engine: The Bash Script That Turns One Domain Into a Recon Dossier
Seven phases, graceful degradation, and a practical way to map attack surface without a heavyweight platform.
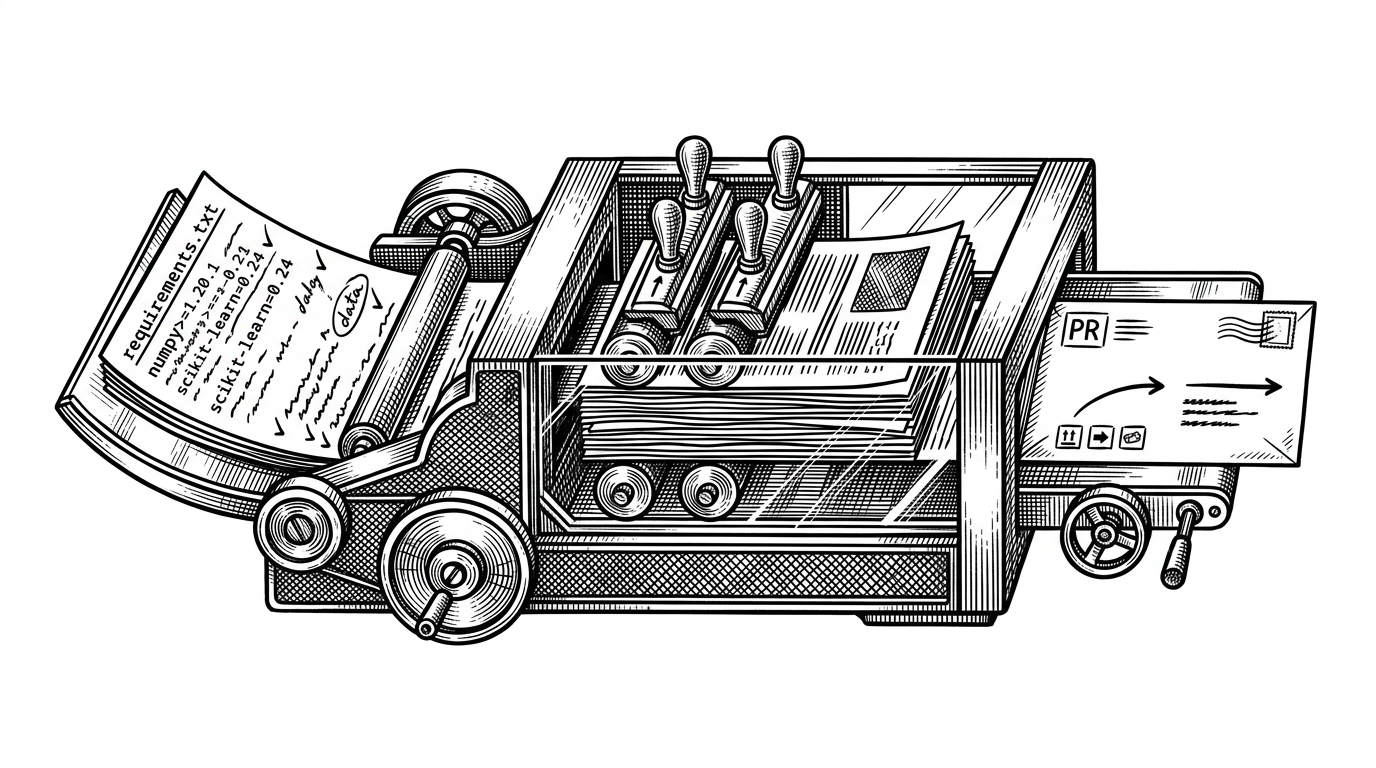
Security & Supply Chain
dependabot-demo: The Repo That Shows Dependabot’s Decision Tree
Two requirement styles, one update policy, and raw bot logs reveal how Dependabot decides what deserves a pull request.
Security & Supply Chain
Repo Explainer: `stealth-addresses` and the One-Byte Trick Behind Private Payments
A Solidity implementation of ERC-5564 and ERC-6538 that makes stealth addresses usable by shrinking wallet scanning to a tiny filter, then doing the heavy cryptography only when a match looks real.
Security & Supply Chain
zen-internals-node: The Firewall Hidden Inside V8
zen-internals-node turns eval() and new Function() into a policy check, so Node.js code can be stopped at the instant it tries to become executable.
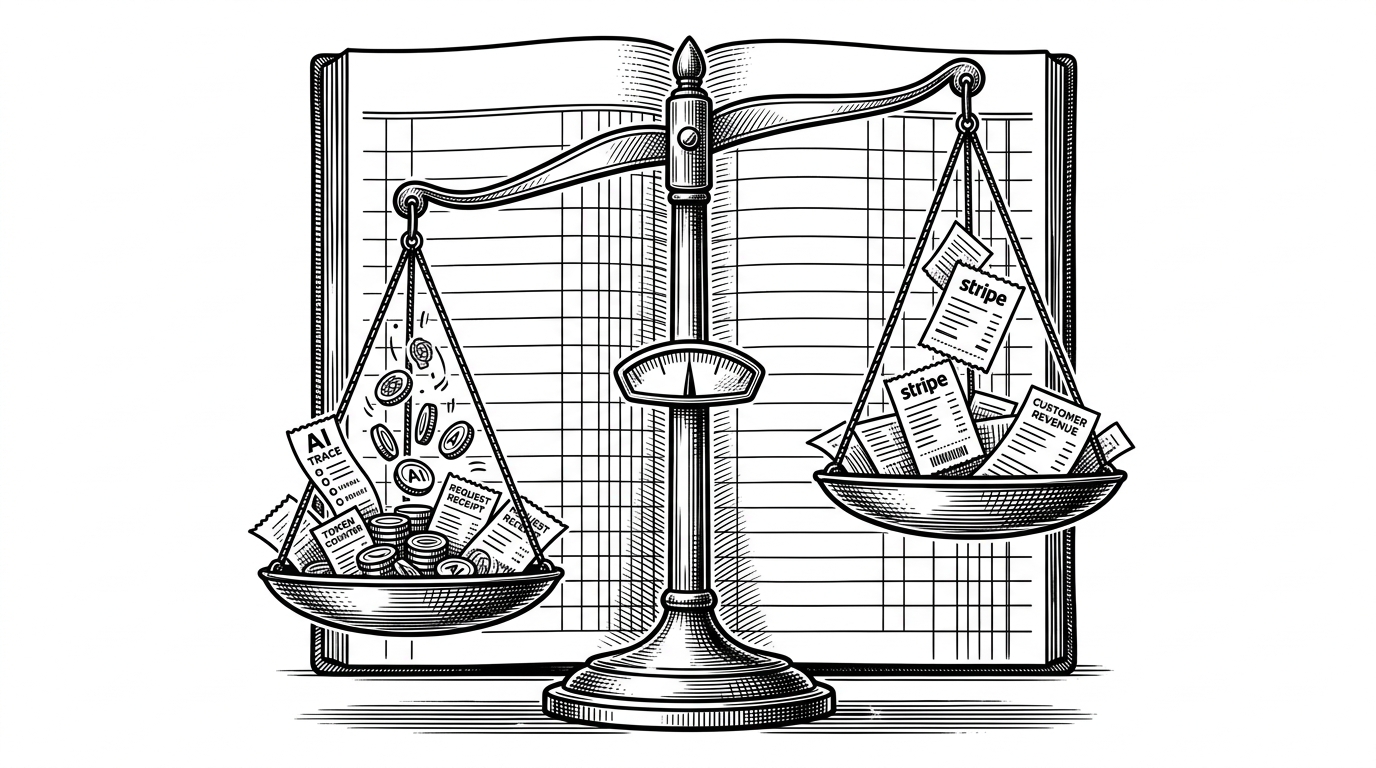
Security & Supply Chain
observe: the open-source observability stack that measures AI margin, not just tokens
It turns model calls, Stripe revenue, and cached responses into one question: which customers and features actually pay for themselves?
Security & Supply Chain
Zero Liability Architecture: Unpacking slimbiggins007/glnc-site
How a solo developer built a Plaid-integrated financial widget without storing a single byte of user data on their own servers.
Security & Supply Chain
The Zero-Dependency Hunter: Unpacking shuvonsec/graphql-mutation-idor
How a minimalist Python script abandons external libraries to automate the discovery of complex logic flaws in modern GraphQL APIs.
Security & Supply Chain
Limen and the End of Prompt-Based Security
Why deterministic middleware, not better system prompts, is the only way to safely give autonomous agents access to your production database.
Security & Supply Chain
github-account-scanner-detection-sample-20260321-195933: The Sacrificial Canary: Unpacking github-account-scanner-detection-sample
How a repository with zero lines of code acts as the controlled variable for testing automated GitHub security scanners.
Security & Supply Chain
a5c-ai/generate-token-action and the Art of the Paranoiac CI Pipeline
Why a specialized authentication tool abandoned the npm ecosystem to build a zero-dependency fortress in pure Node.js.
Security & Supply Chain
idjey/AntiAi: Overlaying Cryptographic Trust on the Deepfake Web
How a NestJS backend and a client-side browser extension bypass platform gatekeepers to mathematically prove video authenticity.
Security & Supply Chain
The Graph-Powered Attacker: Inside VishNet
How an open-source vishing simulator uses real-time voice cloning and Neo4j to autonomously map human vulnerabilities.
Security & Supply Chain
Separating the Eyes from the Hands: Inside NishithP2004/spectra
How a Kubernetes-native orchestration platform uses strict agent hierarchies and ephemeral sandboxes to safely unleash AI on offensive security tasks.
Security & Supply Chain
The Human-Readable Signature: Inside duplicati/jsonsignature
How a zero-dependency C# library uses stream concatenation and JSON comments to bypass the complexity of JWS.
Security & Supply Chain
bug-bounty-runner: Beyond the Grep: Inside Shuvonsec's Autonomous Security Agent
How claude-bug-bounty bridges the gap between raw network packets and human-level vulnerability reasoning.
Security & Supply Chain
The Ghost in the Tokenizer: ai-copilot-payload-builder
How invisible Unicode "Sneaky Bits" turn benign documents into high-privilege AI exploits.
Security & Supply Chain
The Browser is the Bypass: How google-dork-runner Solves the Cat-and-Mouse Game of Search Recon
By abandoning the automated scraper in favor of a generated "Query Factory," this zero-dependency tool turns Google's bot detection into a non-issue.
Security & Supply Chain
oauth-security-tester: The Zero-Dependency Ghost in the OAuth Machine
How oauth-security-tester audits complex authentication chains using nothing but the Python Standard Library.
Security & Supply Chain
shuvonsec/graphql-idor-scanner: The Differential Engine for GraphQL Identity Theft
Moving beyond status codes to detect cross-tenant data leakage through automated session comparison.
Security & Supply Chain
ax-agent: AX: Building the Fireproof Kitchen for Autonomous Agents
How a security-first architecture and signature-based prompting are turning untrusted LLMs into reliable, always-on digital employees.
Security & Supply Chain
ax-ai-agent-mvp: Project AX and the Architecture of the Fireproof Agent
How a Trust Zone proxy and a 34k-line audit-first codebase solved the security crisis that nearly killed the autonomous assistant.
Security & Supply Chain
codex-cli-hardening-cheatsheet: Building a Sandbox for the Future of Agency
Moving beyond "be careful" prompts to a zero-trust architecture for your terminal.
Security & Supply Chain
0xTrace and the Decoupled Privacy Layer
By offloading stealth metadata to the Vara Network, 0xTrace solves the "Announcement Problem" that has plagued Ethereum’s native privacy standards.
Security & Supply Chain
Partial Control: Inside the Salesforce Kill Switch Architecture
How hwong103/partial uses granular trigger deactivation to survive the complexity of enterprise-scale automation.
Security & Supply Chain
Authentication-System: Hardening the Handshake: Inside a Production-Ready Auth System
Beyond the basic JWT tutorial. How to implement token rotation, granular rate limiting, and database-side session defense in Node.js.
Security & Supply Chain
ToastNotify: The Windows Identity Thief in Your Taskbar
How a tiny C# utility exposes the massive trust gap in the Windows Action Center by “borrowing” the credibility of your most trusted apps.
Security & Supply Chain
The Auditor is the Code: Inside Self-Scribing-Auditor
Moving past generic security checklists to autonomous, repo-native vulnerability research.
Security & Supply Chain
Credentia: The Zero-Knowledge Handshake for Digital Credentials
How a hybrid of Sepolia events and IPFS CIDs creates a verifiable, time-bound audit trail for sensitive documents without the gas-heavy overhead of on-chain storage.