Security & Supply Chain
Open-source security, dependency auditing, supply-chain safety, and agent guardrails
227 explainers
Security & Supply Chain
customized_agentic_system_mvp: The Agent Harness That Puts Governance Before Intelligence
A multi-LLM agent stack where every tool call passes through RBAC, rate limits, injection scanning, and human approval before execution.
Security & Supply Chain
`absoluteappsec/nextgen`: The AppSec Lab That Teaches AI to Read Code, Think Like a Pentester, and Police Itself
A hands-on framework for turning LLMs into private security agents, with RAG, hybrid context, few-shot reasoning, and prompt-injection guardrails built into the curriculum.
Security & Supply Chain
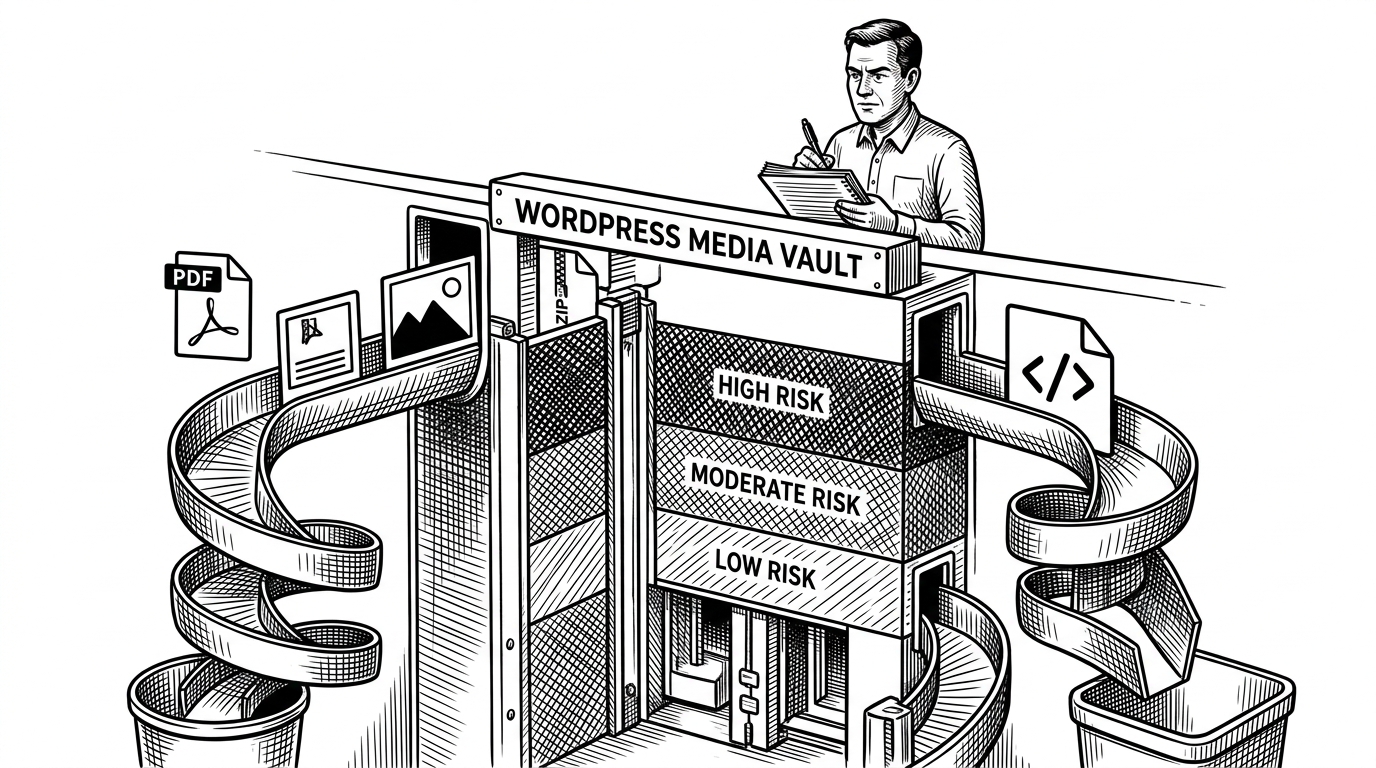
pro-mime-types: Pro Mime Types: The WordPress Plugin That Turns File Uploads Into Policy
A deep dive into how sybrew/pro-mime-types rebuilds WordPress’s MIME rules, scores file risk, and keeps multisite upload policy sane across changing environments.
Security & Supply Chain
CloudMechanic: The AWS Scanner That Acts Like an OBD-II Port for Your Cloud
A read-only Go CLI with a TUI twin, a uniform scanner interface, and a concurrent execution model that makes cloud hygiene feel local, fast, and safe.
Security & Supply Chain
antipattern-czar: The Linter That Refuses to Hide Your Errors
A Bun-powered TypeScript tool that turns swallowed exceptions, weak logging, and brittle string matching into reliability policy.
Security & Supply Chain
chain-strike: Chain Strike: The Claude Code Skill That Treats Vulnerabilities Like Building Blocks
Instead of stopping at a single bug, this repo tries to link findings into a stronger attack chain, turning exploit composition into a repeatable workflow.
Security & Supply Chain
Inside `safechain-internals`: The Release Channel That Keeps Aikido Device Protection Alive
A tiny repository for binaries, MDM profiles, and anti-tamper rules reveals how enterprise security software gets installed, trusted, and kept running across Windows, macOS, and Linux.
Security & Supply Chain
curiefense-1: Curiefense: The WAF That Thinks in Flows, Not Just Packets
A cloud-native security layer for Envoy that blends Rust, Lua, GitOps, and sequence-aware inspection into one proxy-side defense system.
Security & Supply Chain
Cloud-Sentinel Is a CSPM in Pieces. That’s Why It Works.
A Node gateway, Redis, a Python worker, and a risk-score layer turn cloud auditing into a distributed system you can test, scale, and reason about.
Security & Supply Chain
`acquisitions`: The Node.js API Boilerplate That Treats Security Like an Execution Layer
A layered Express 5 stack with Arcjet, Drizzle, Zod, and Docker defaults that turns user role, bot detection, and rate limiting into part of the request flow.
Security & Supply Chain
Wazuh-SIEM-Lab: The Repo That Turns a SIEM Into a Detection Engine
A two-node lab that starts with default alerts and ends with tuned rules, real-time file integrity monitoring, and the log-forensics mistakes every security engineer eventually has to make.
Security & Supply Chain
Threat-Intel-Nom-Nom: The open-source TIP that only pings you when the threat is actually new
A self-hosted threat-intel stack that watches websites, RSS, APIs, and .onion sources, extracts IOCs, and uses content-plus-context hashing to cut alert fatigue before it starts.
Security & Supply Chain
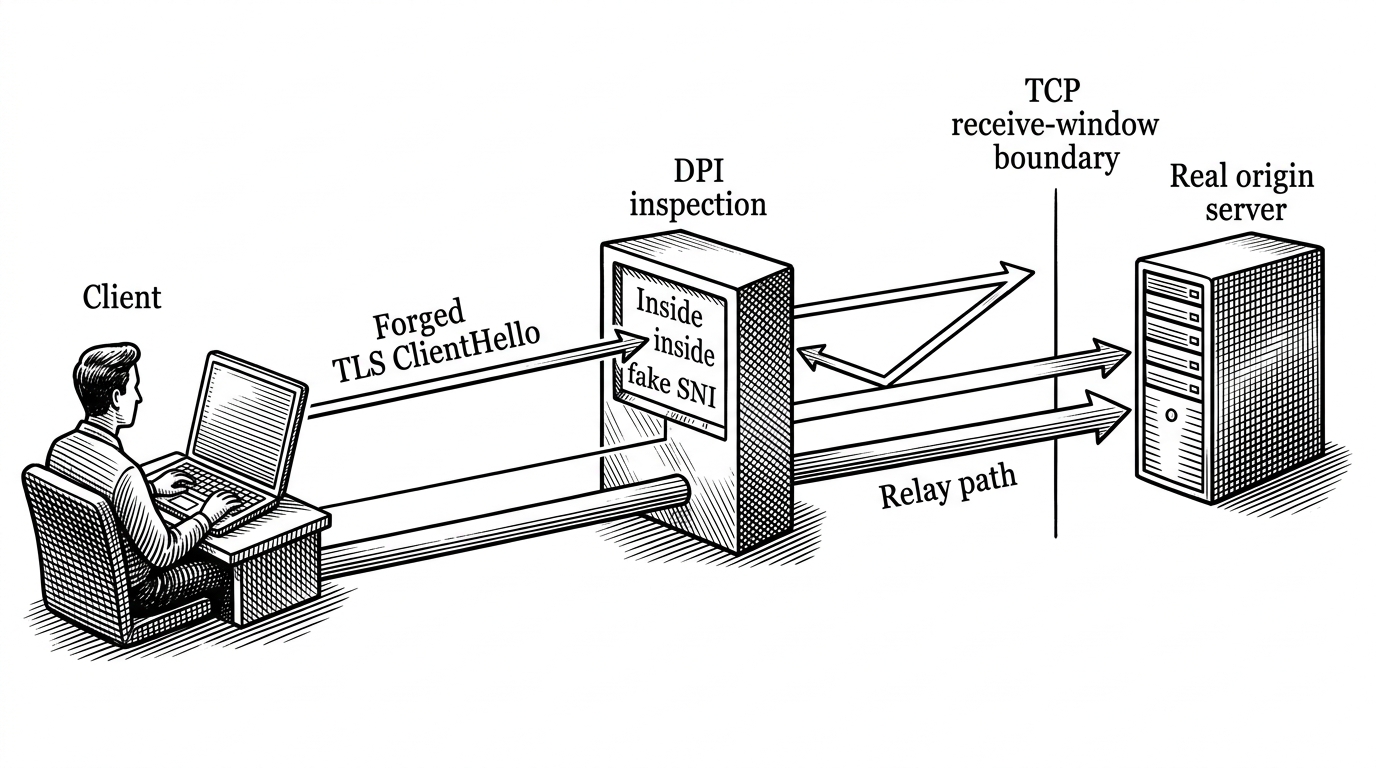
sni-spoofing-rust: How a Rust Tool Gaslights DPI With One Packet That Never Reaches the Server
A deep dive into the out-of-window SNI injection trick, the raw-socket plumbing behind it, and why the project is more about TCP state than TLS itself.
Security & Supply Chain
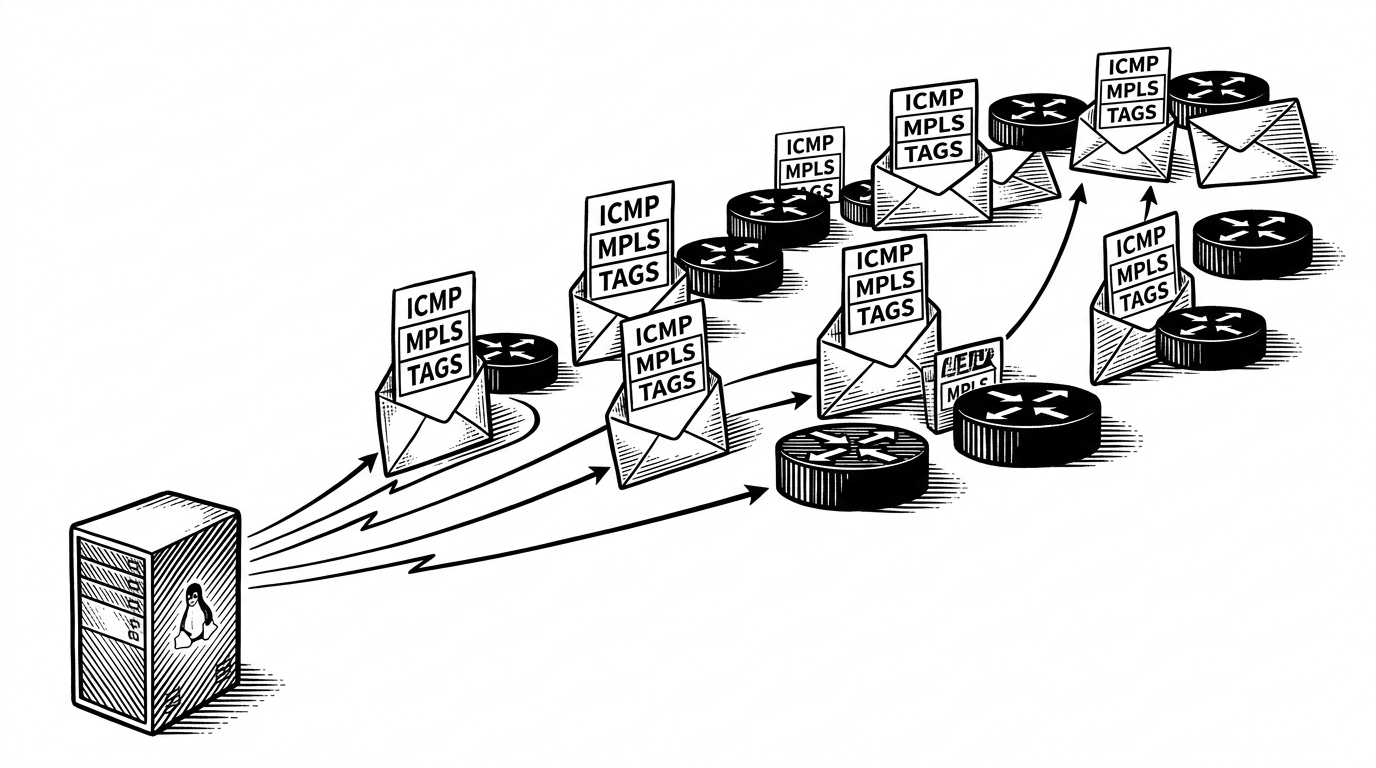
apernet-traced: How One C Program Can Lie Convincingly to traceroute
A compact Linux packet engine that forges ICMP Time Exceeded replies, injects MPLS labels, and makes a single host look like a whole provider backbone.
Security & Supply Chain
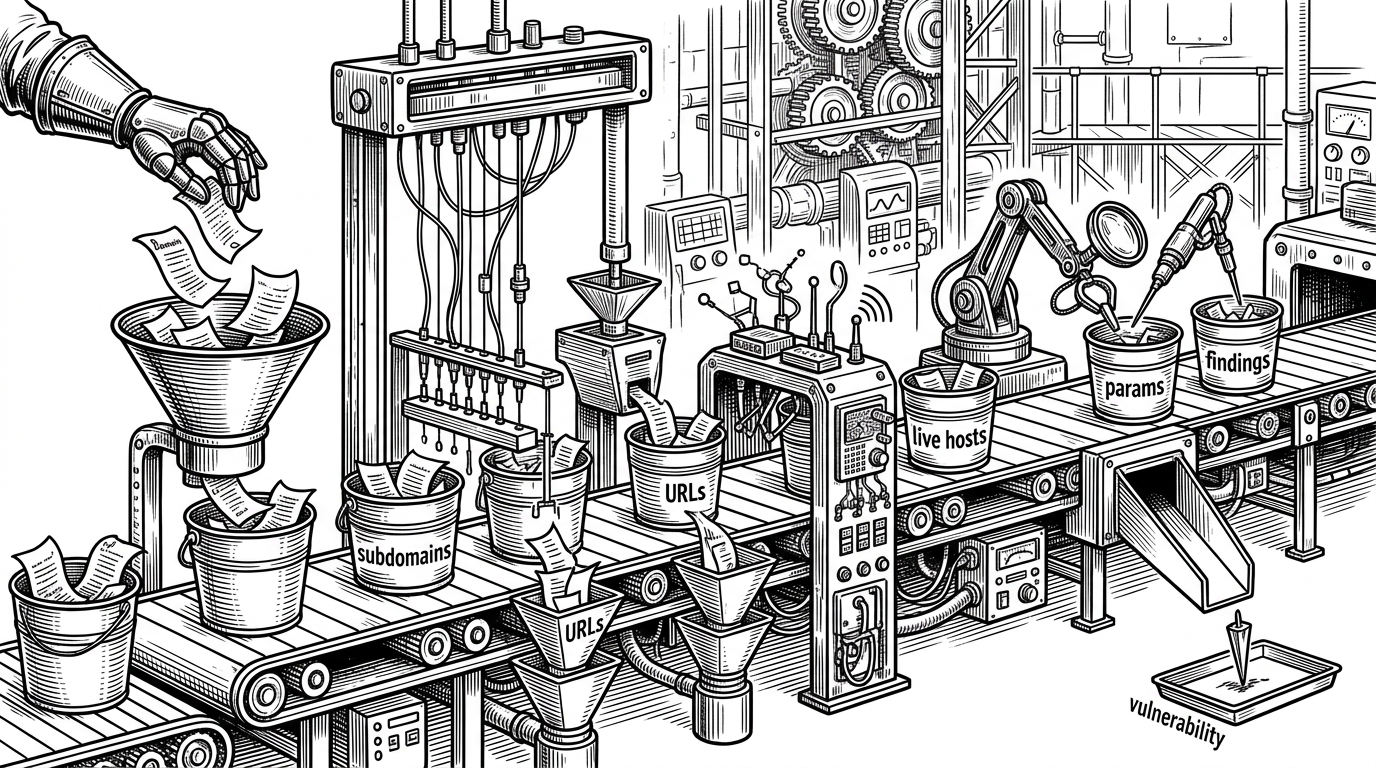
`full-hunt-pipeline`: The Bash Glue That Turns Recon Into a One-Command Workflow
A compact shell orchestrator that chains subdomain discovery, content hunting, and vulnerability scanning into a file-driven bug bounty pipeline, with quick mode and authenticated testing built in.
Security & Supply Chain
JohannesLks/CVE-2026-23398: The ICMP Packet Linux Forgot to Ignore
A tiny Scapy proof of concept, a forged inner header, and a kernel validation path that turns a routine network error into a crash.
Security & Supply Chain
AikidoSec/gcp-onboarding-terraform-module: how to onboard a cloud scanner without a shared secret
This Terraform module encodes least privilege, API enablement, and keyless trust into one repeatable GCP handoff.
Security & Supply Chain
safe-chain-jfrog-plugin: Turning Artifactory Into a Dependency Bouncer
A deep dive into the JFrog extension that checks remote packages against live malware intel and blocks suspicious downloads before they land.
Security & Supply Chain
The Air-Gapped CI Pipeline: Inside twentyhq/ci-privileged
How the open-source CRM Twenty isolated its GitHub Actions to solve the "pwn-request" problem, creating a zero-trust DMZ for automated code review.
Security & Supply Chain
The Zero-Trust Terminal: Inside postrv/sanctum-oss
How a Rust-based security daemon protects developers from poisoned AI dependencies, credential exfiltration, and runaway API billing.
Security & Supply Chain
docs: Iron.sh and the Architecture of the Untrusted Root
How a network-level 'Secret Proxy' and egress-secured sandboxes are solving the AI agent security dilemma.

Security & Supply Chain
The Zero-Dependency Sentry: How openrouter-webhook-logger Masters AI Observability
A masterclass in "unzip-and-run" architecture, securing the chaotic world of LLM webhooks with nothing but raw PHP and a MySQL socket.
Security & Supply Chain
VulnSwarm: The Security Scanner That Thinks in Graphs
It turns source code into a Neo4j-backed attack map, then uses reachability, centrality, and agentic review to find the code paths that matter most.
Security & Supply Chain
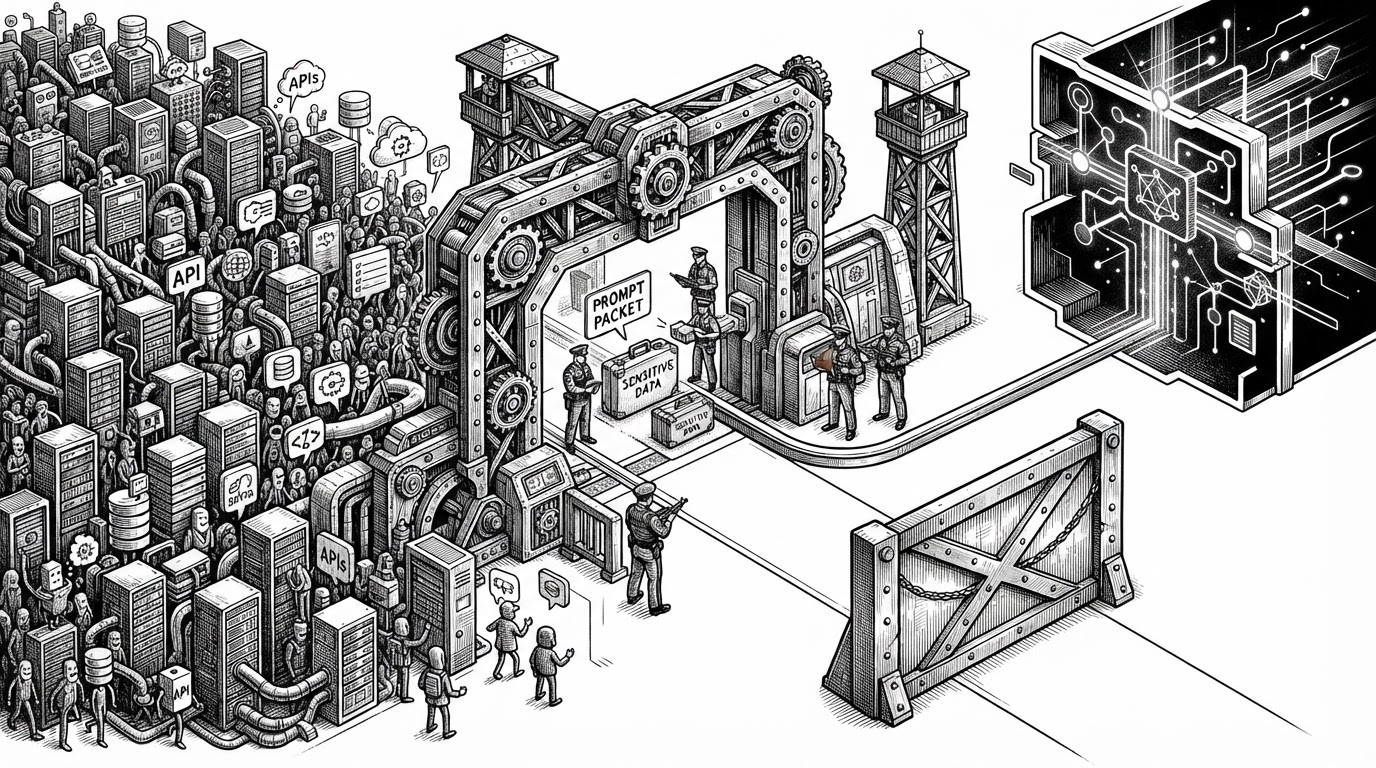
secure-genai-gateway: Secure GenAI Gateway: The Firewall for Prompts, Outputs, and AI Spend
A centralized Python gateway that scrubs sensitive input, blocks risky responses, encrypts audit trails, and gives enterprises one place to govern every LLM request.
Security & Supply Chain
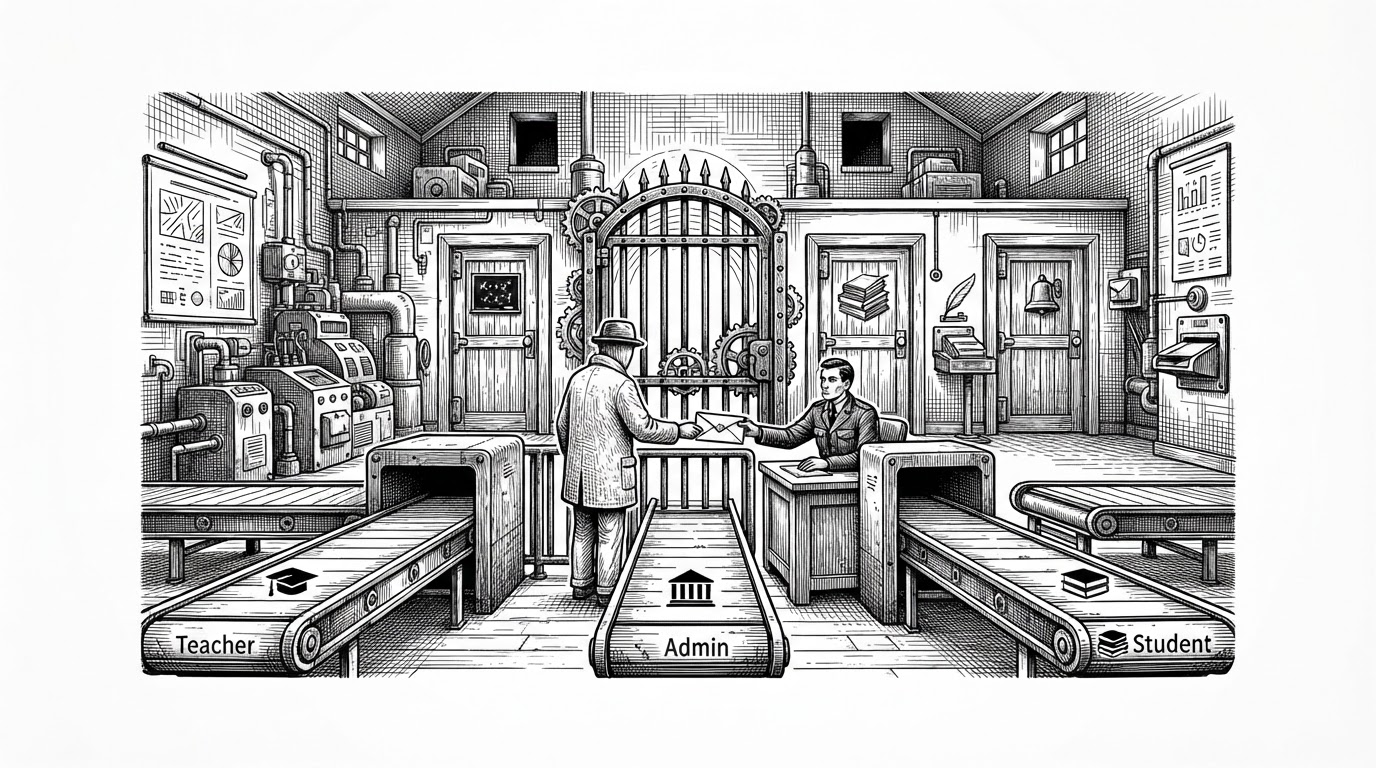
student-management-system-django-drf: A Django API Where Roles Shape the Whole App
A close look at a student management backend that uses permissions, scoped querysets, serializer validation, and signals to turn RBAC into a system design pattern.
Security & Supply Chain
BankCoreSolution: The Bank App Built to Teach You How to Break It, Then Prove It Works
A cleanly separated .NET banking system that turns MSTest, NUnit, xUnit, and formal test documentation into one connected training ground.
Security & Supply Chain
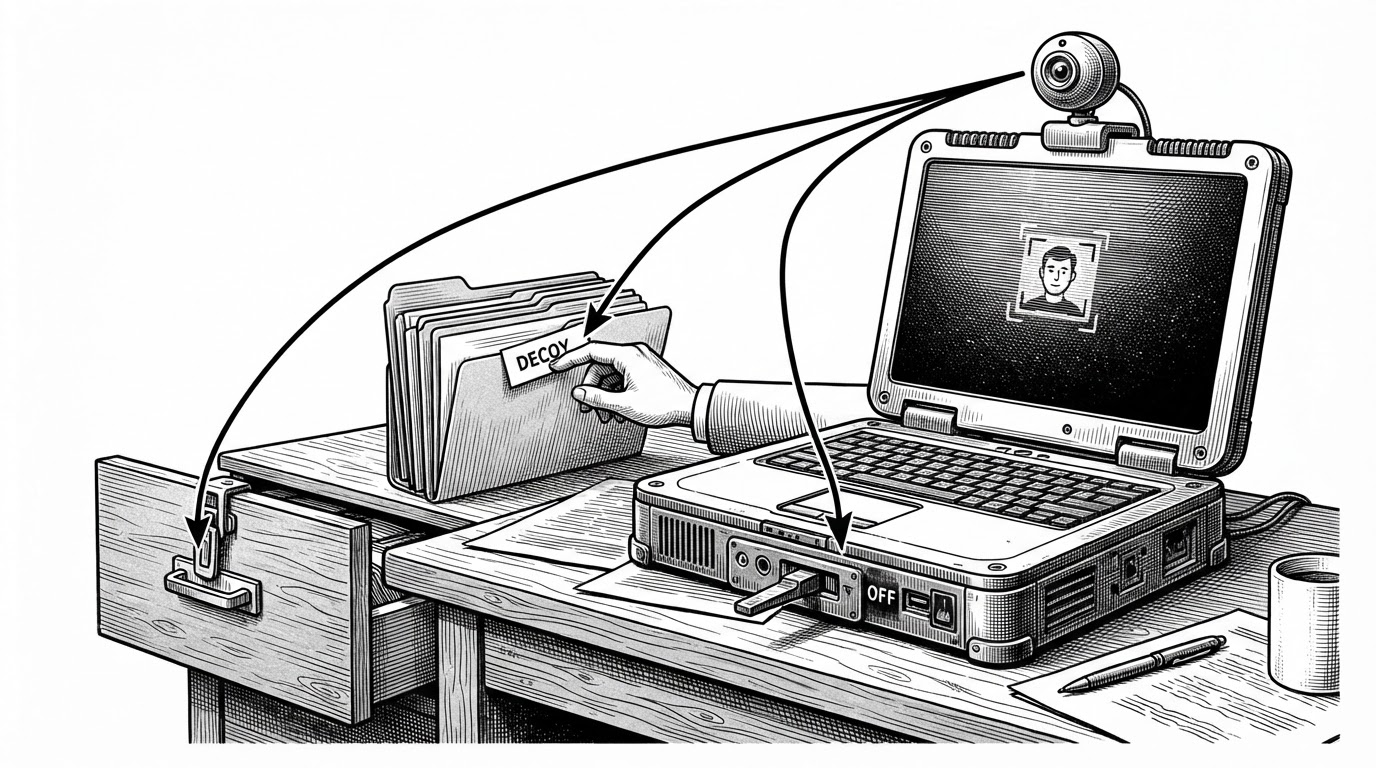
AegisSecure: When a Webcam Becomes a Lock, a Vault, and a Decoy
How a Python security script turns face recognition into active defense, encrypting files, swapping in fake data, and giving the owner a remote kill switch.
Security & Supply Chain
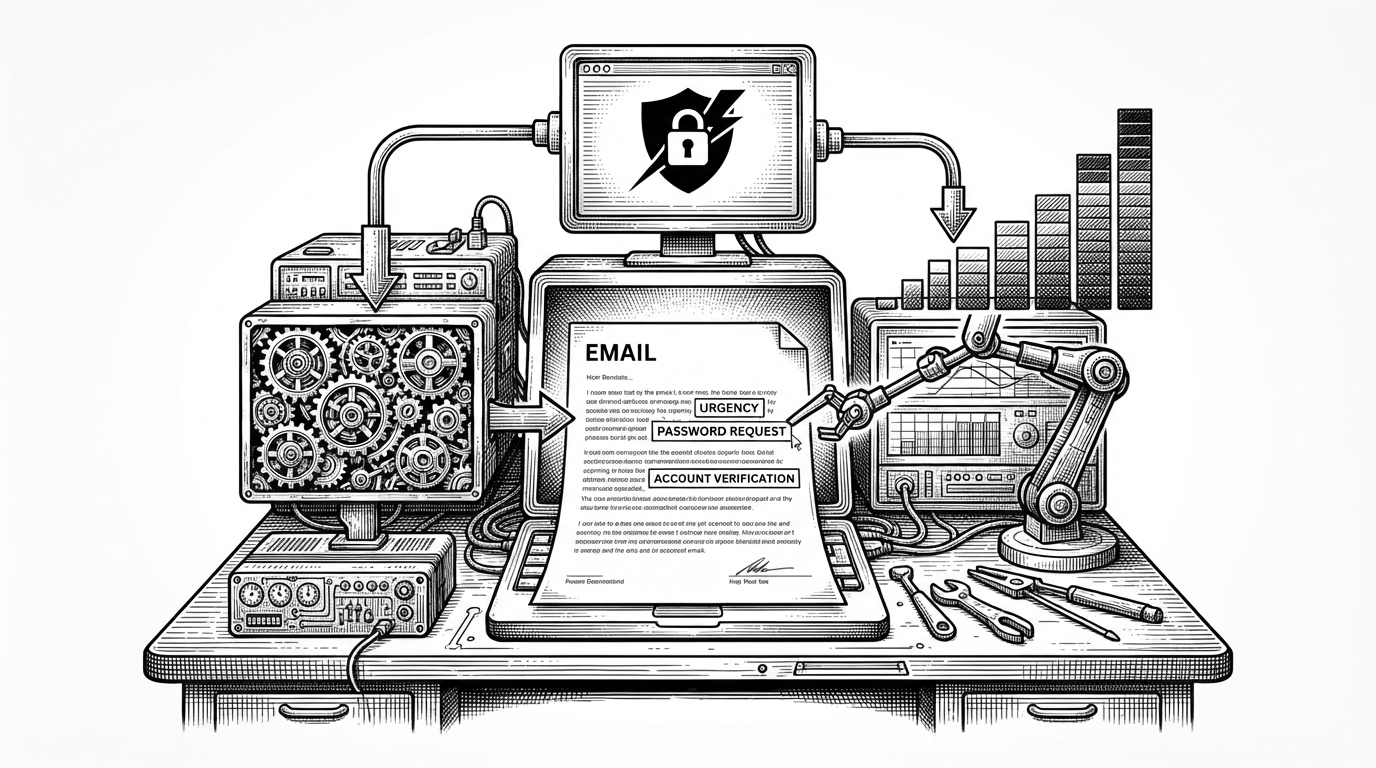
email-phishing-detector: The Phishing Filter That Trusts Both a Model and a Red Flag Checklist
A full-stack email scanner that pairs TF-IDF logistic regression with frontend heuristics, then wraps the whole thing in a cyber-terminal interface that explains risk instead of just naming it.
Security & Supply Chain
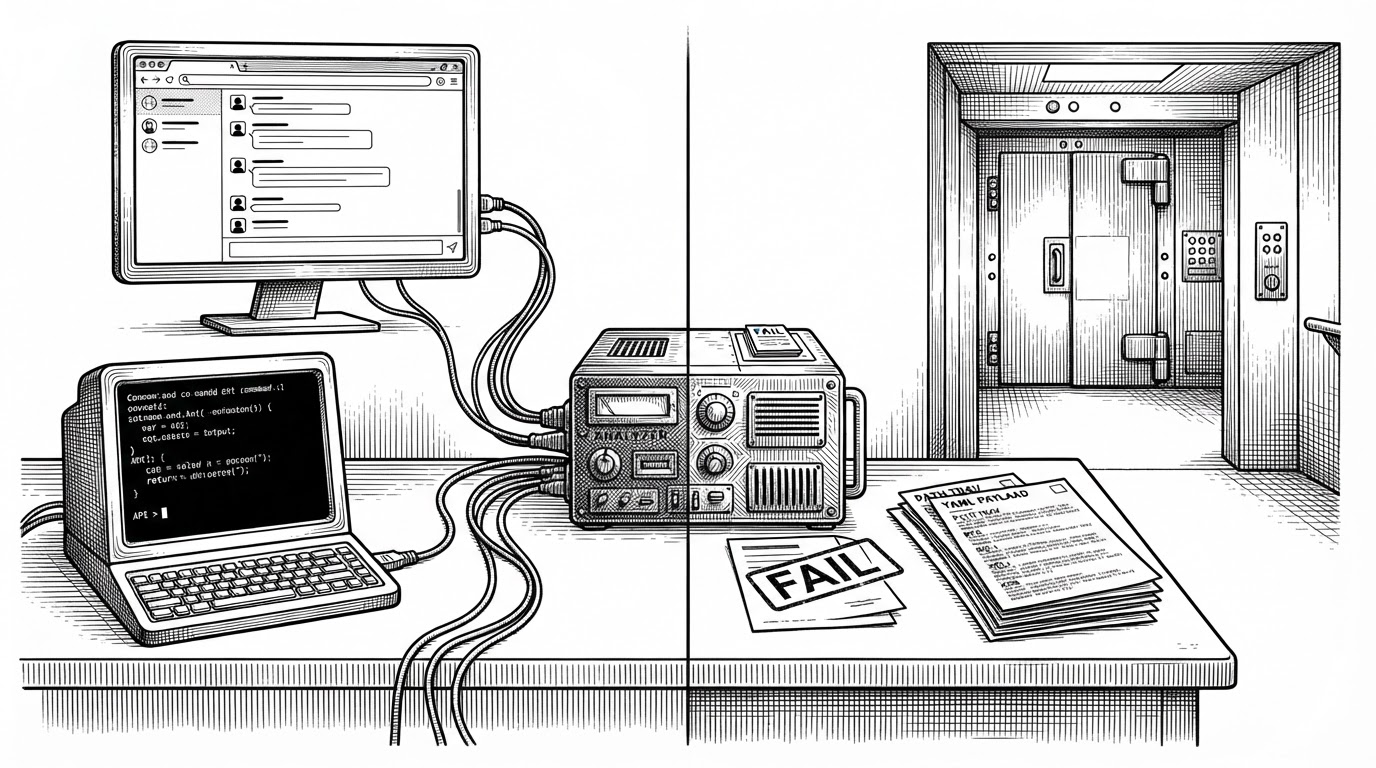
AI-LLM-Application-Security-Scanner: LLMShield: The Security Scanner That Turns Prompt Attacks Into Testable Failures
A modular Python framework for probing LLM apps through APIs and browser UIs, then judging responses with a fail-first rule that treats any leak as a broken guardrail.
Security & Supply Chain
packet-analyzer-dpi: How a C++ DPI Engine Turns One Flow Into One Thread
A deep dive into manual packet parsing, TLS SNI extraction, and a fast-path architecture that keeps stateful inspection local, parallel, and surprisingly readable.
Security & Supply Chain
SecureLab---Login-Security-Testbed: SecureLab: The Login Lab Where Defenses Flip Live and the Attacks Keep Talking
A cyber range for authentication security that makes lockouts, CAPTCHA bypasses, and leaked-password checks visible in real time.
Security & Supply Chain
Prahar: The Open-Source AI Sentry Built to Catch Lies, Faces, and Gunfire
A modular defense intelligence framework that fuses RSS news, deepfake detection, acoustic reconnaissance, and a structured military knowledge base into one triage pipeline.
Security & Supply Chain
MedVault: The EHR That Lets Patients Hand Out Time-Limited Access
A Spring Boot and React health-record system built around patient ownership, audit trails, and role-based access instead of a static provider database.
Security & Supply Chain
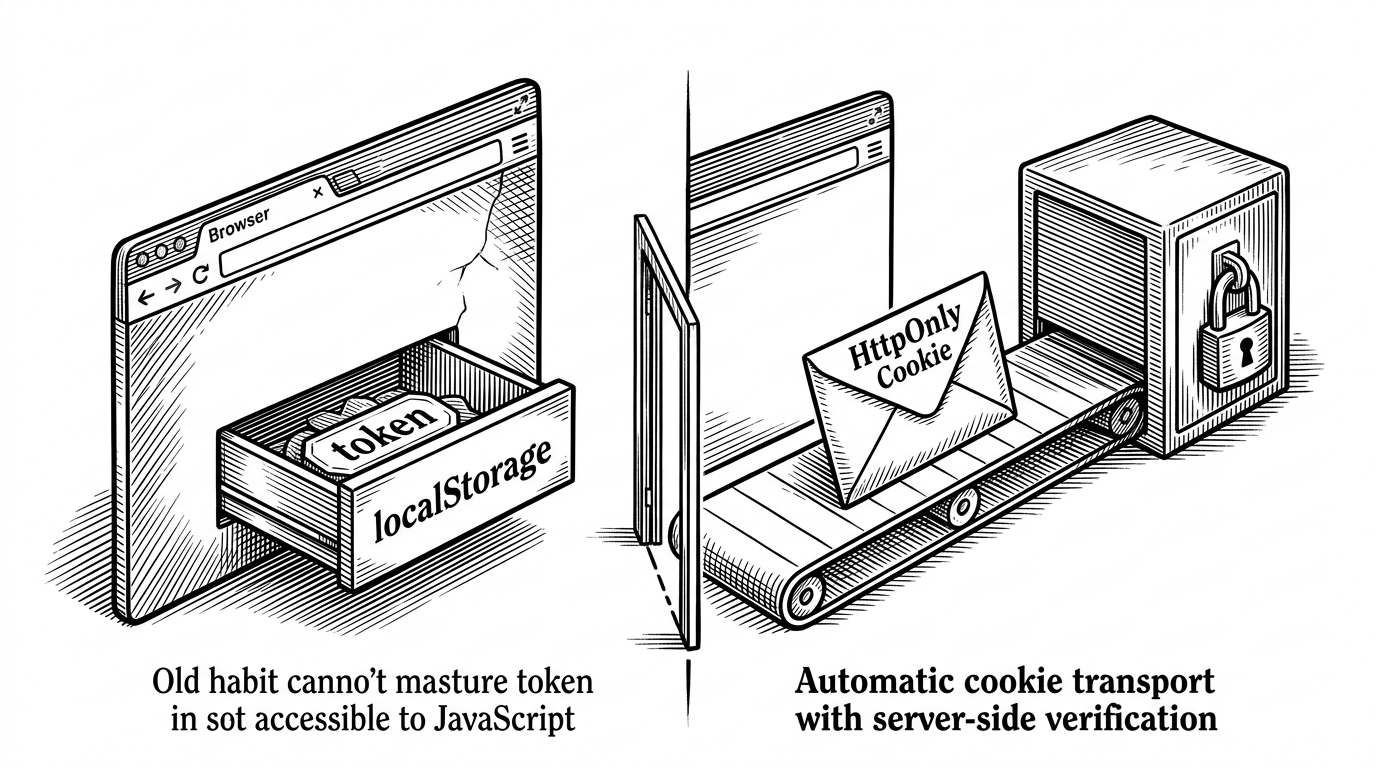
mukesh417/mern-authentication-system: The MERN Auth Template That Treats Security Like a Product Feature
A clean full-stack reference for cookie-based sessions, email OTP verification, and password resets that behave like a real application, not a classroom exercise.
Security & Supply Chain
Abhisekhkotnala/voting_backend: The Express Middleware That Turns Smart Contracts into REST
A compact Node.js bridge that hides ABI complexity, signs owner transactions on the server, and exposes an Ethereum voting contract as a conventional API.
Security & Supply Chain
Expense-tracker: LedgerFlow: The Expense Tracker That Solves the Boring Parts First
A look at the security plumbing, cross-origin glue, and defensive data model behind a full-stack finance app that behaves more like production software than a hobby project.
Security & Supply Chain
EphemeralGuard: Securing the Infrastructure That Disappears First
A real-time security lab for cloud workloads that vanish before traditional tools can finish an audit. It tags short-lived resources early, correlates noisy alerts into incidents, and measures its own precision against synthetic ground truth.
Security & Supply Chain
ProjectsFolder Turns a Complaint Portal Into a Security-First Bureaucracy Machine
Under the hood of a student admin system that treats refresh tokens, role gates, and audit logs like enterprise infrastructure, while keeping the frontend brutally simple.
Security & Supply Chain
Secure-Audio-Steganography: When the Secret Is in the Pauses
A Python steganography pipeline that asks you to speak the cover text, counts the silence, and hides encrypted bits where the waveform gives you room.
Security & Supply Chain
Vaultly: The Fintech Monorepo That Treats Every Transfer Like a Failure Case
A deep dive into the locking, idempotency, MPIN checks, and webhook simulation that make this wallet stack read like a production-finance blueprint.
Security & Supply Chain
Computer_Network: SECURECHAT: A Chat App That Makes Encryption Part of the Conversation
A room-based, browser-native E2EE chat built with Next.js and Socket.io, where the UI teaches you how a message becomes unreadable before it ever leaves your browser.
Security & Supply Chain
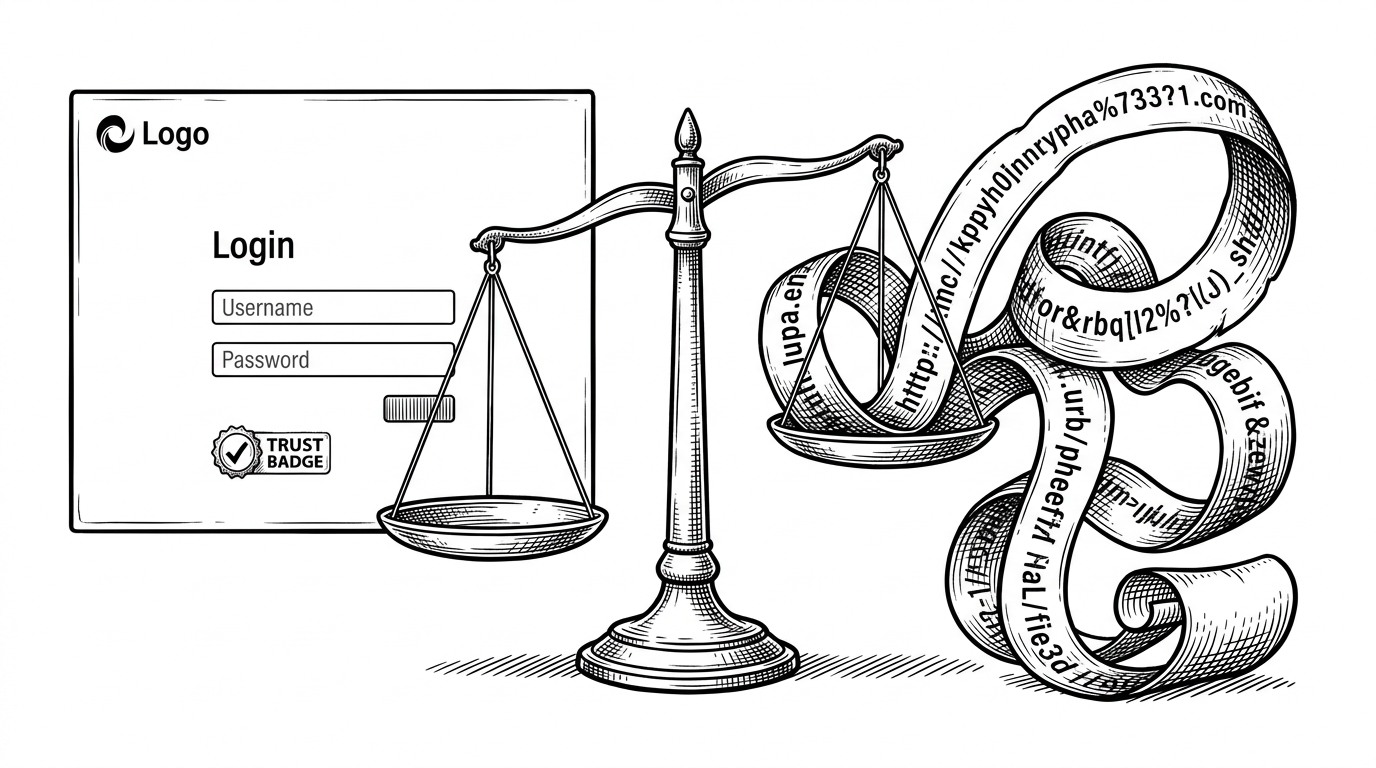
multimodal-phishing-detection-system: Multimodal Phishing Detection System: When a Fake Site Has to Lie Twice
A phishing detector that reads the URL, looks at the page, and deliberately trusts the messier clue more when the two disagree.
Security & Supply Chain
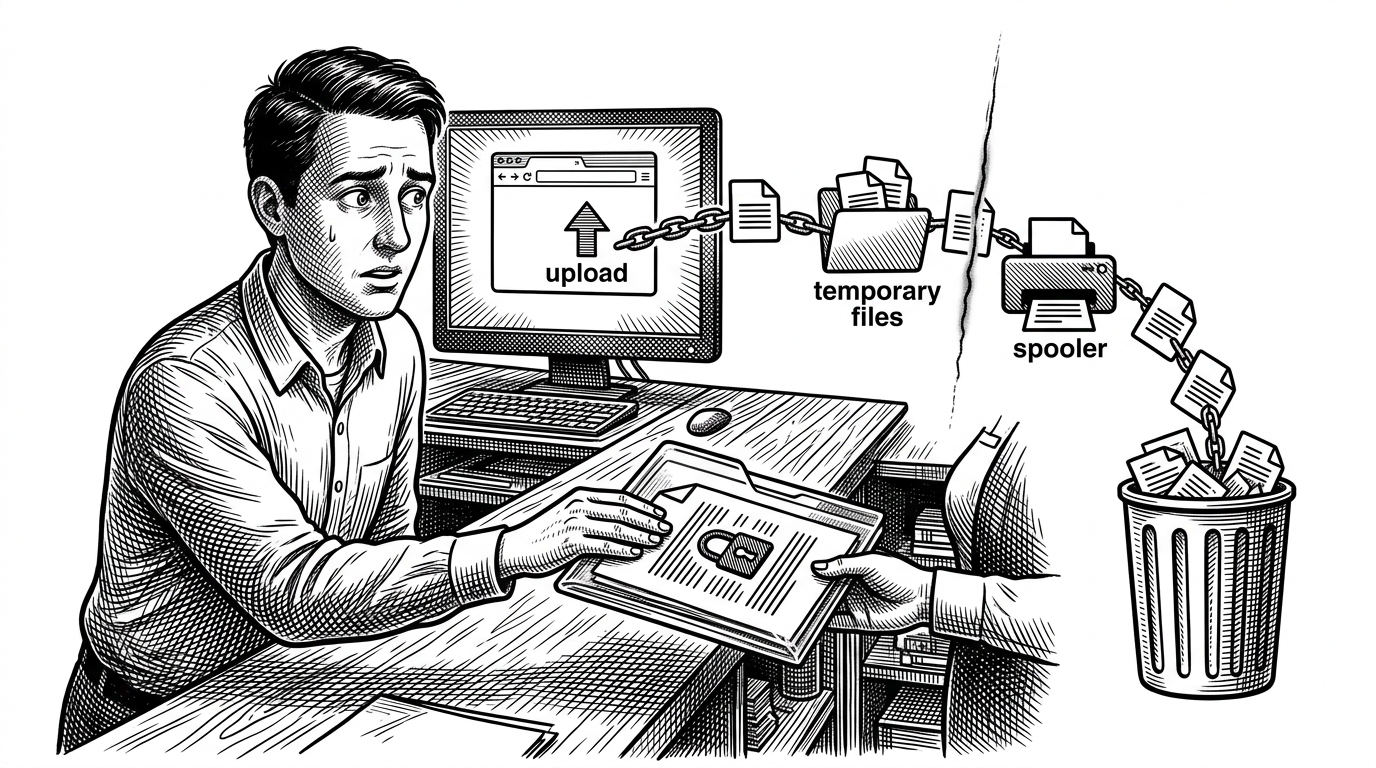
404error: SafePrint: The Print-Shop Pipeline Built to Leave No Digital Trace
A privacy-first upload-to-spool system that treats the browser, the shop PC, and the file system as temporary, unsafe surfaces.
Security & Supply Chain
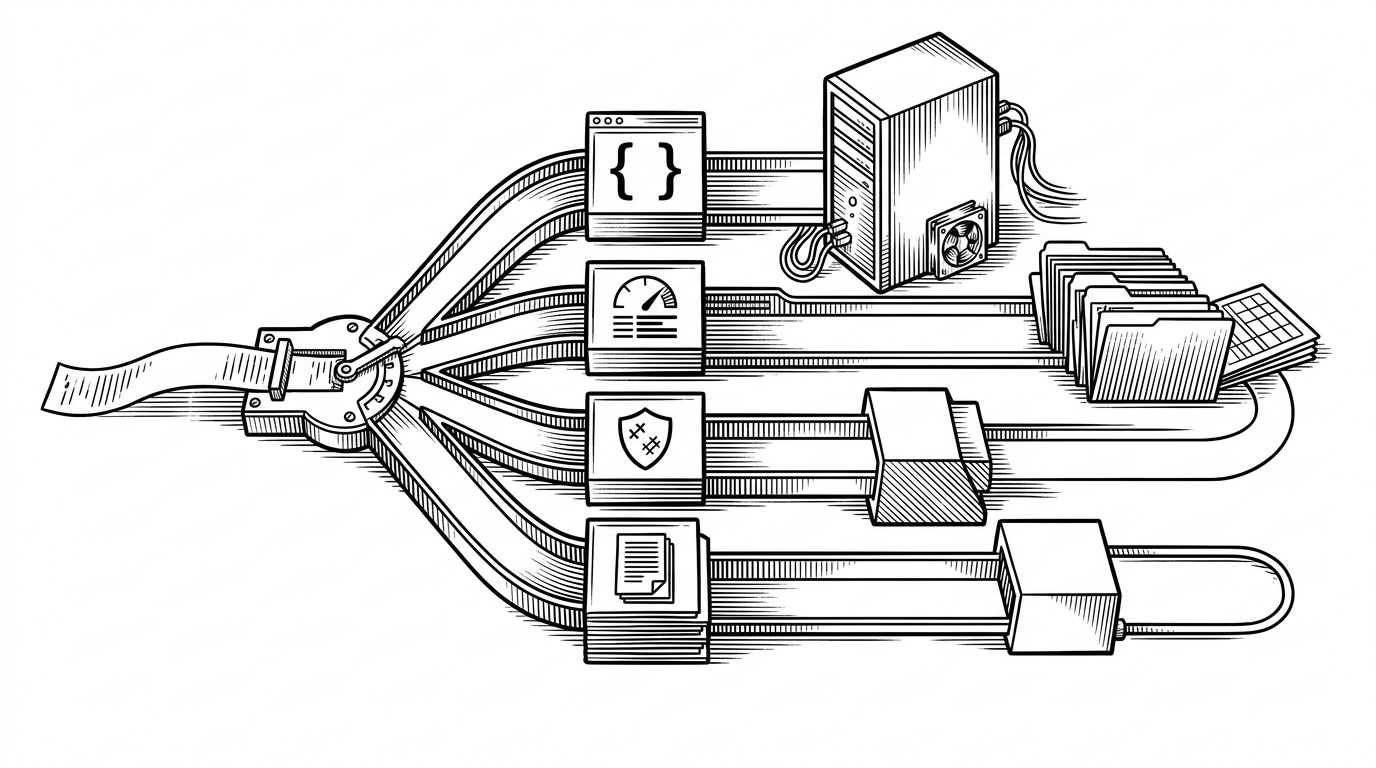
GHOSTNET: The Local Security LLM That Routes, Grounds, and Audits Itself
A deep dive into a privacy-first pentesting assistant that uses deterministic intent routing, live CVE aggregation, and model auditing to turn a chatbot into a security workflow.
Security & Supply Chain
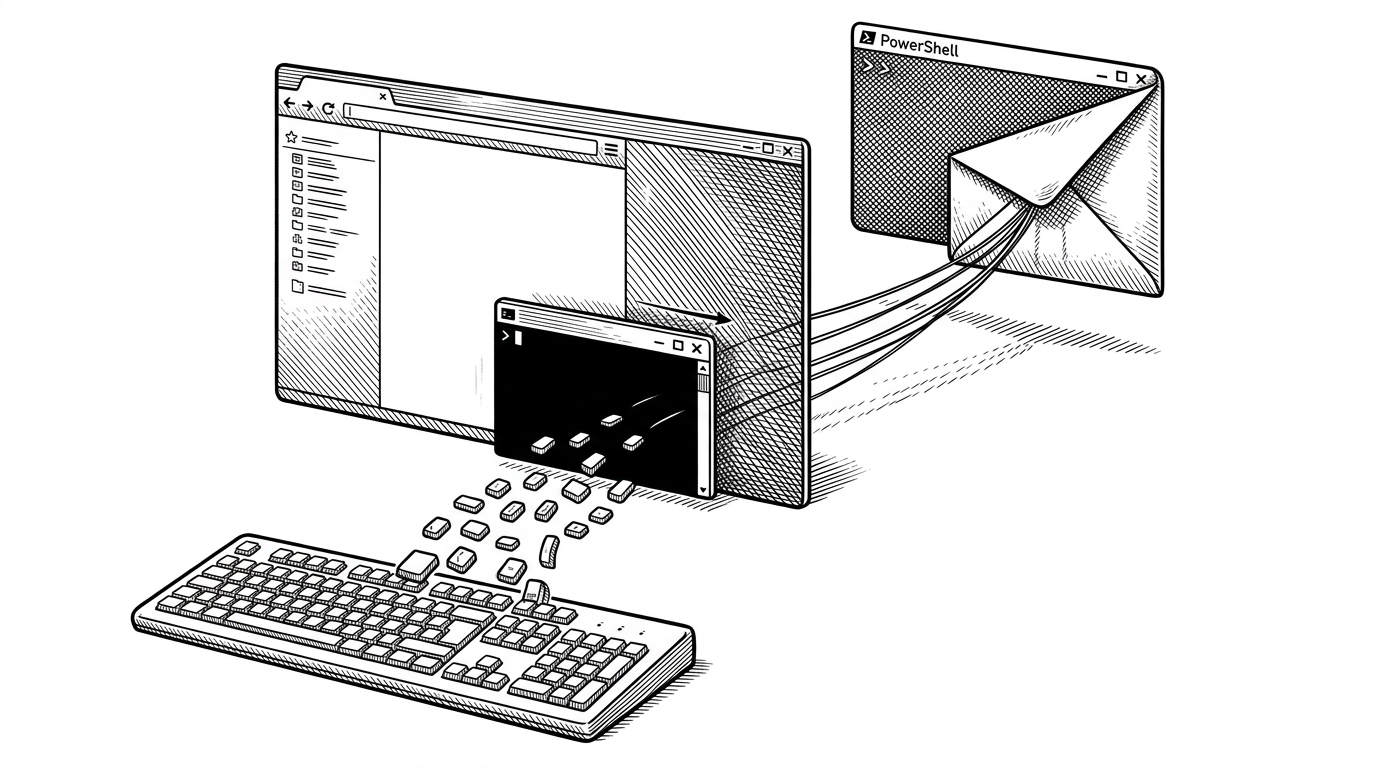
Advanced-Keylogger-using-C-: How a C++11 Windows Hook Becomes a Stealthy Exfiltration Pipeline
A compact Win32 proof of concept that captures keystrokes, hides its console, and moves logs through PowerShell, Base64 layering, and a companion decryptor.
Security & Supply Chain
grok-pentest: When a Pen Test Becomes a Reasoning Loop
An AI-driven security framework that reads responses, chooses the next test, and turns reconnaissance into a conversational workflow.
Security & Supply Chain
dataminerbr/base64: The Smallest Possible Trust Trap
A one-file GitHub repo hides a Base64-encoded URL, but the real story is how a harmless-looking challenge can steer curiosity toward an external delivery gate.
Security & Supply Chain
rustenium-identity: Inside Rustenium Identity's browser mask
A Rust overlay that keeps headers, JavaScript, time zone, and proxy behavior in one believable profile instead of treating spoofing as a single switch.