Security & Supply Chain
Open-source security, dependency auditing, supply-chain safety, and agent guardrails
227 explainers
Security & Supply Chain
The Non-Invasive Skeleton Key: Inside rxerium/FreePBX-Vulns-December-25
How a handful of YAML templates outpaced global botnets to secure critical telecom infrastructure without firing a single exploit.
Security & Supply Chain
openai/gpt-oss-safeguard: The Moderation Model That Reads the Rulebook First
A new safety system treats policy as input, not an afterthought. That makes moderation more transparent, more adaptable, and much harder to mistake for a fixed classifier.
Security & Supply Chain
opengrep-rules: The security rule that treats prompt injection like RCE
AikidoSec’s opengrep-rules repository shows how static analysis is moving from code bugs to AI workflow abuse, one YAML file at a time.
Security & Supply Chain
PS4-BO3-Customs: How a PS4 Mod Turns Black Ops III Into Its Own PC Clone
A custom map converter, runtime hook layer, and Lua spoofing stack work together to load Steam Workshop-era content on jailbroken consoles by borrowing the game’s hidden PC pathways.
Security & Supply Chain
The Unix Immune System: Unpacking apernet/apermon
How a minimalist C daemon bypasses the bloated observability stack to turn raw sFlow data into instant DDoS mitigation.
Security & Supply Chain
market-ai-resolution: The AI Oracle That Knows When Not to Decide
A TypeScript proof of concept for prediction-market settlement that pulls live evidence, follows market rules, and falls back to UNKNOWN when confidence is too low.
Security & Supply Chain
modelcontextprotocol/access: The GitOps Approach to Open Source Identity
How the fastest-growing AI protocol uses Pulumi and TypeScript to turn cross-platform community management into a single pull request.
Security & Supply Chain
The Invisible Identity Transplant: Unpacking descope-migration
How a Python utility reconstructs legacy password hashes and auto-discovers schemas to move user bases without forcing a single password reset.
Security & Supply Chain
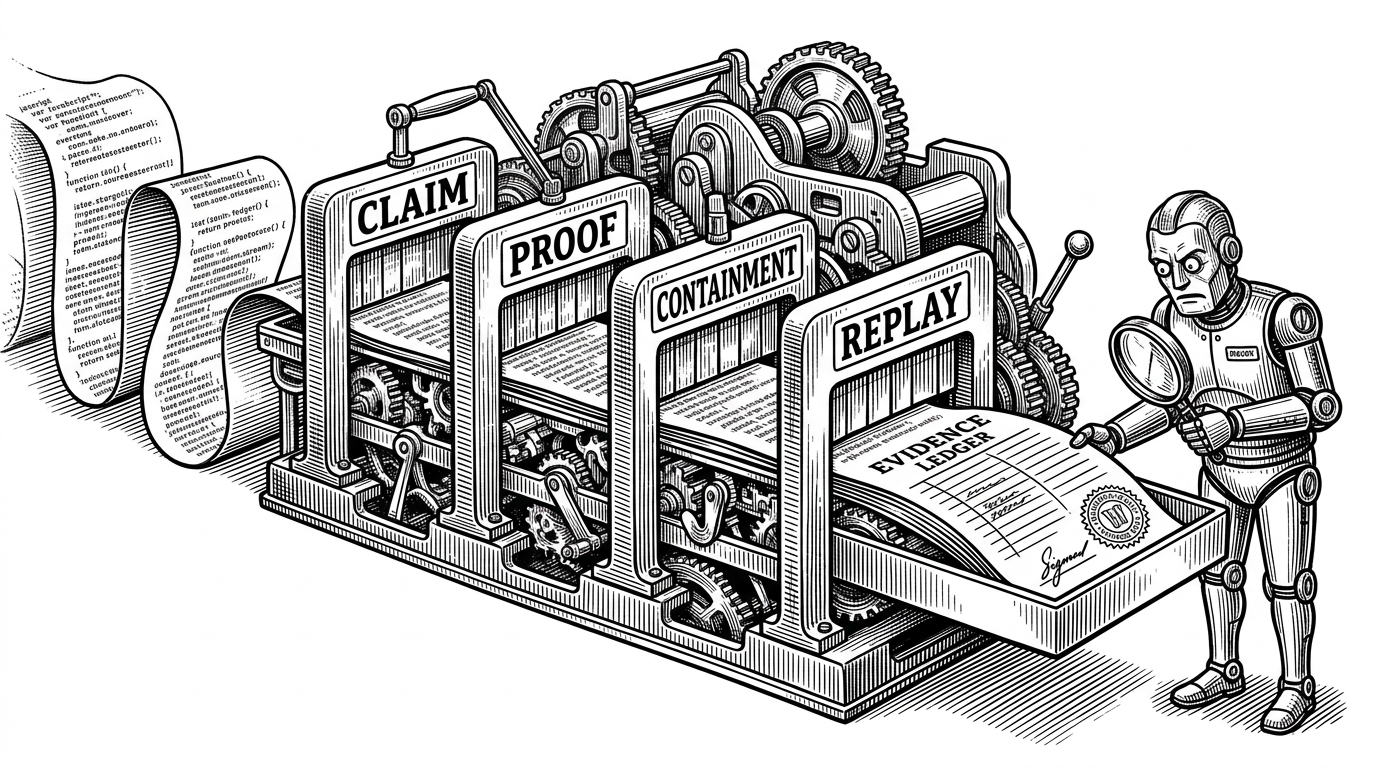
franken_engine: FrankenEngine: The JavaScript Runtime That Tries to Prove Its Own Claims
A Rust runtime for hostile extension workloads, where containment, replay, and evidence are built into the engine instead of bolted on after the breach.
Security & Supply Chain
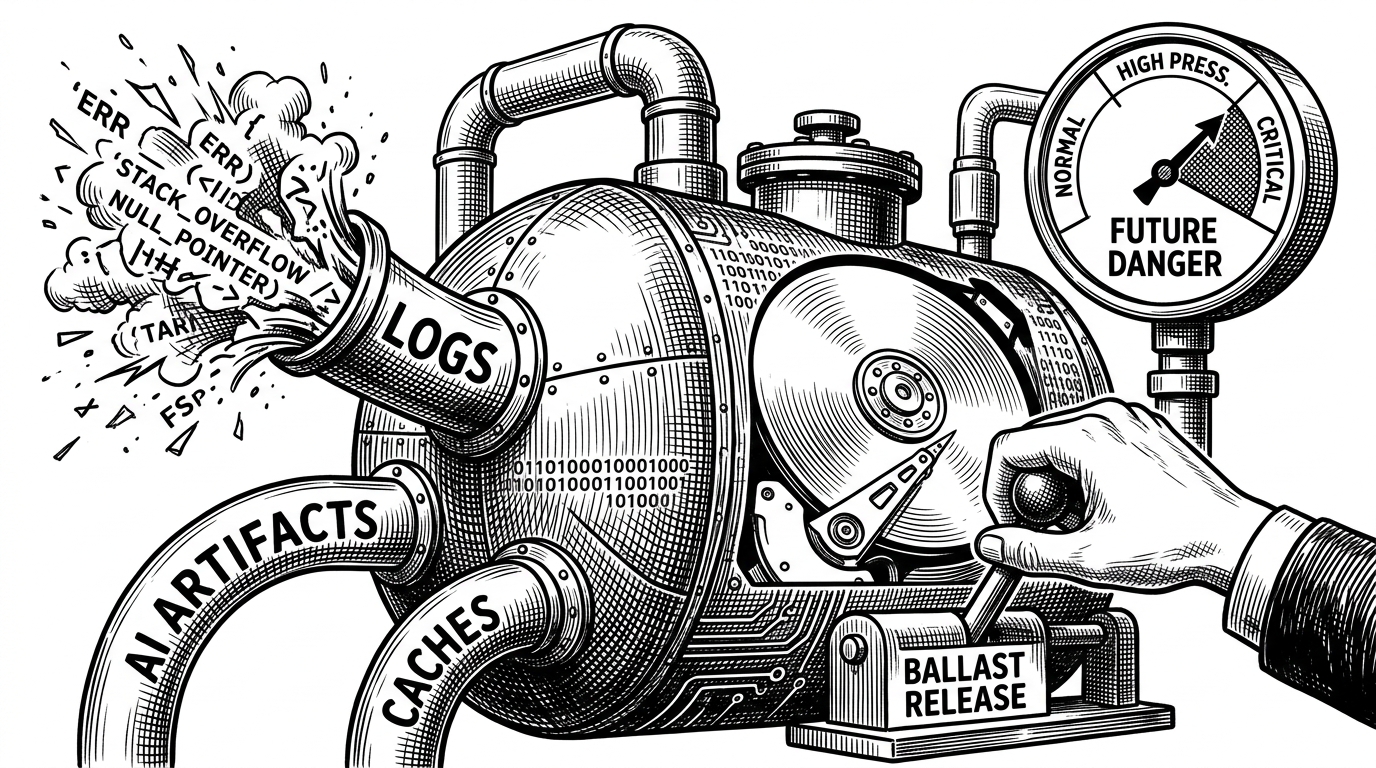
storage_ballast_helper: Predictive Self-Healing for the AI Agent Era
How a Rust-based daemon uses industrial control theory and sacrificial files to prevent disk exhaustion during high-velocity coding loops.
Security & Supply Chain
The Black Box Recorder for an AI Meltdown: Inside openclaw-security-news
How a Python-driven repository became the machine-readable crisis dashboard for the most controversial agent framework in open-source history.
Security & Supply Chain
The Sandbox for the Agentic Era: Inside ironsh/irons
How a Go-based CLI and a specialized egress proxy are replacing local environment variables with boundary-level secret injection to secure autonomous coding agents.
Security & Supply Chain
`descope/authzcache`: The Sidecar That Makes Fine-Grained Authorization Feel Local
A deep dive into the caching layer that keeps Descope’s auth graph fast, indexed, and usable even when the remote service is not.
Security & Supply Chain
Nightstream: The Post-Quantum zkVM Built Like a Proof, Not a Guess
A lattice-based folding machine in Lean and Rust that turns recursive proving, memory consistency, and future-proof security into one research prototype.
Security & Supply Chain
Anomalous-Outputs: Inside the Pseudo-Jailbreaks That Don’t Quite Break Claude
A forensic archive of prompt loops, split personas, and safety refusals that look like exploits until you read the fine print.
Security & Supply Chain
OpenAI teen-safety-policy-pack: The moderation layer written like code
How Markdown policies, label ladders, and test datasets turn teen safety into a versioned enforcement spec.
Security & Supply Chain
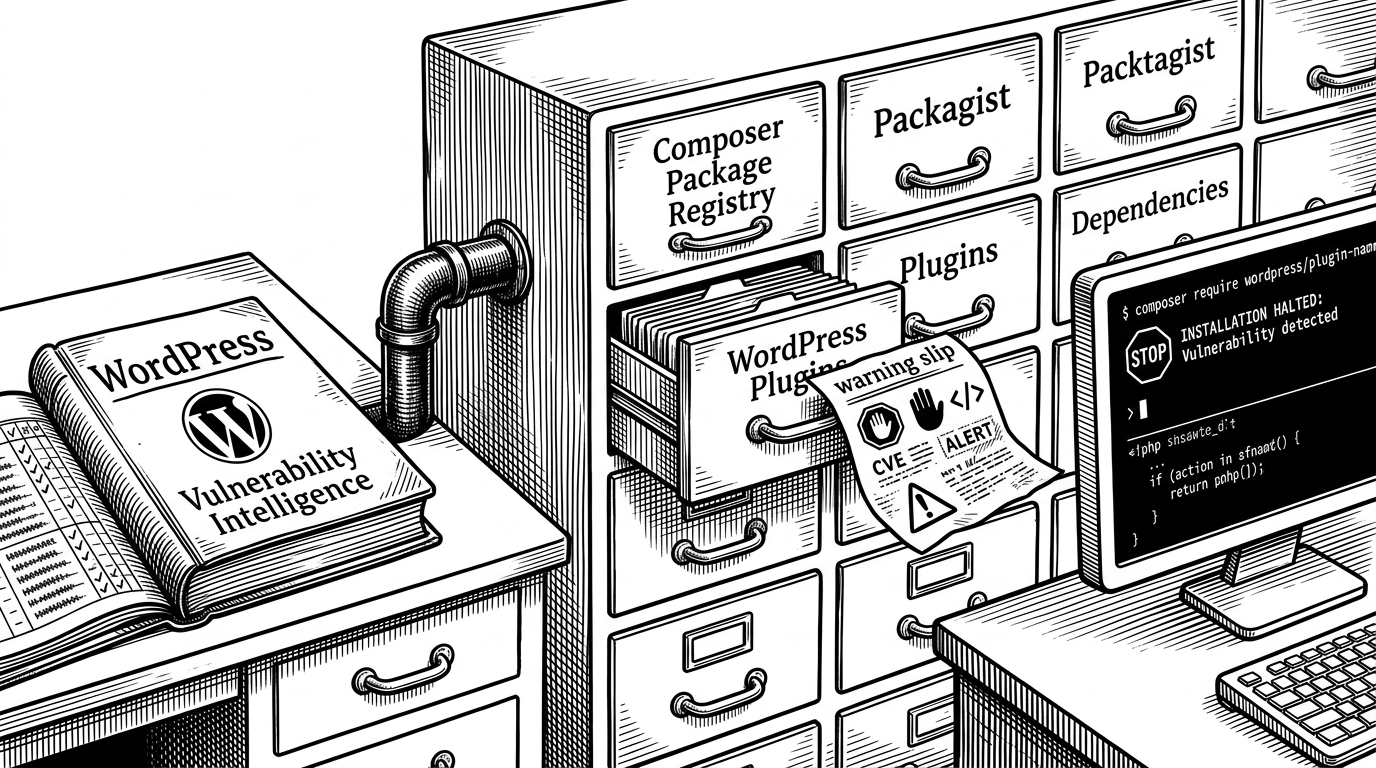
wpsecadv: The Go Service That Teaches Composer About WordPress Security
A tiny repository provider with a big job: translate Wordfence advisories into Composer-native security checks, so WordPress plugins and themes can be blocked before they ever ship.
Security & Supply Chain
ADCS-Attack: The Cheat Sheet That Turns PKI Misconfigurations Into a Map
A lightweight GitHub index for the ESC1 to ESC10 attack surface, and a sharp example of how offensive security knowledge gets standardized, searched, and reused.
Security & Supply Chain
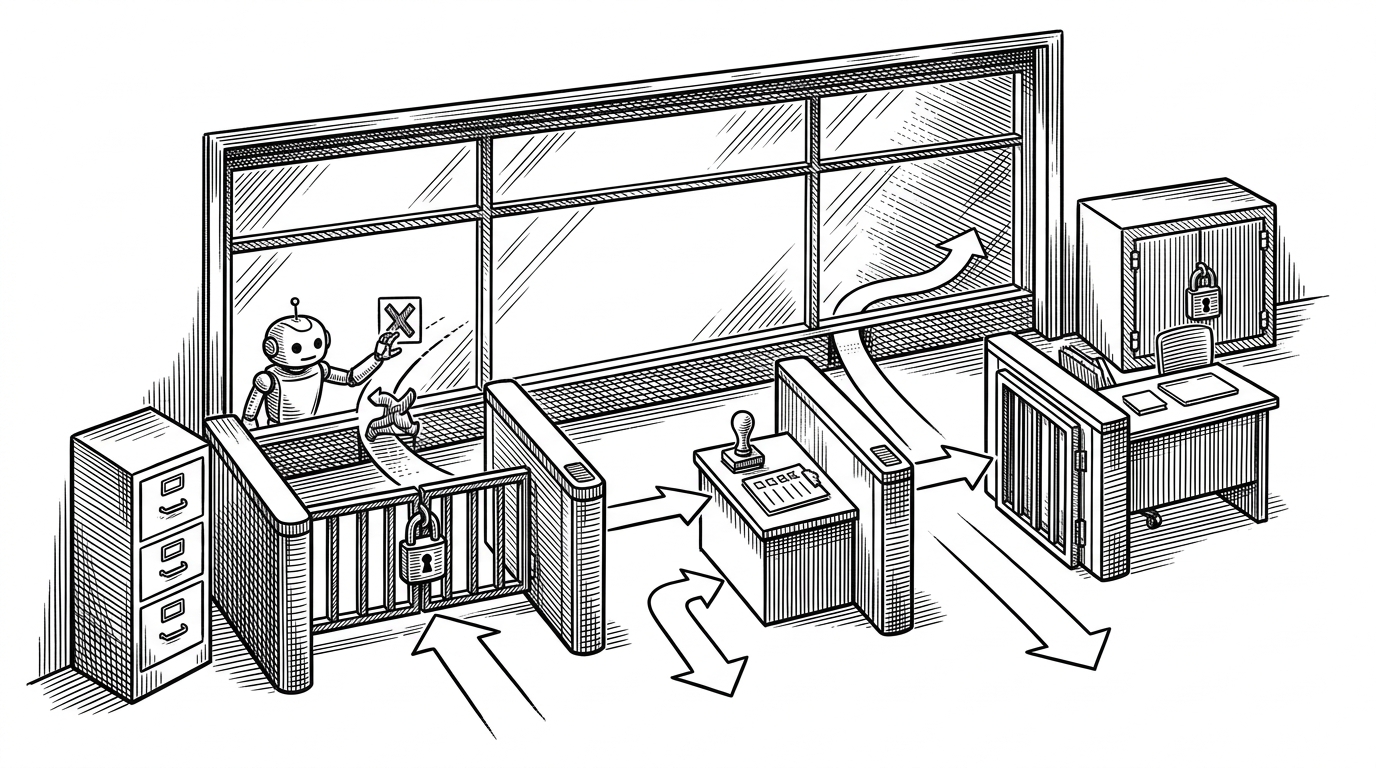
Inside `okdt/claude-code-hardening-cheatsheet`: The Policy Layer That Puts Claude Code on a Leash
A practical hardening template for Claude Code that turns agentic coding from “hope it behaves” into explicit least-privilege controls, sandboxing, and human checkpoints.
Security & Supply Chain
starlingbank/api-samples: The sample repo that turns bank APIs into a cryptographic contract
How Starling teaches developers to sign requests, verify webhooks, and move between public banking APIs and payment services without guessing at the rules.
Security & Supply Chain
Tank: Building a Hardened Registry for the Agentic Era
After the ClawHavoc supply chain attacks, a new breed of package manager is enforcing "Permission Budgets" on the AI skills that run our code.
Security & Supply Chain
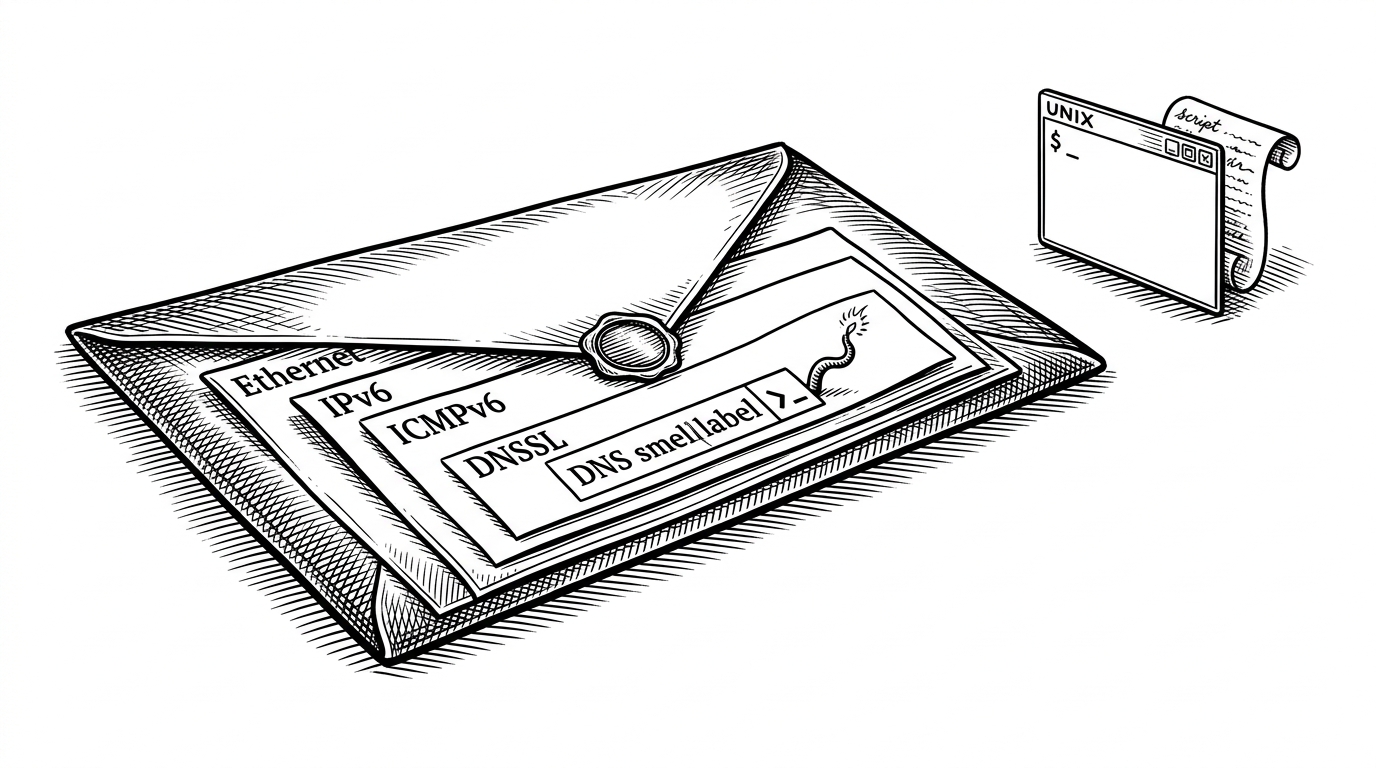
JohannesLks/CVE-2025-14558: How an IPv6 Router Advertisement Became a Shell Command
A FreeBSD rtsold proof of concept shows how a valid-looking DNS search list can cross from C parsing into shell execution, turning local network presence into code execution.
Security & Supply Chain
The Aegis website is what trust looks like in HTML
Beem Development turns a public landing page into part of the security story, using React, Vike, and a tightly controlled SSR pipeline to keep the site fast, explicit, and easy to verify.
Security & Supply Chain
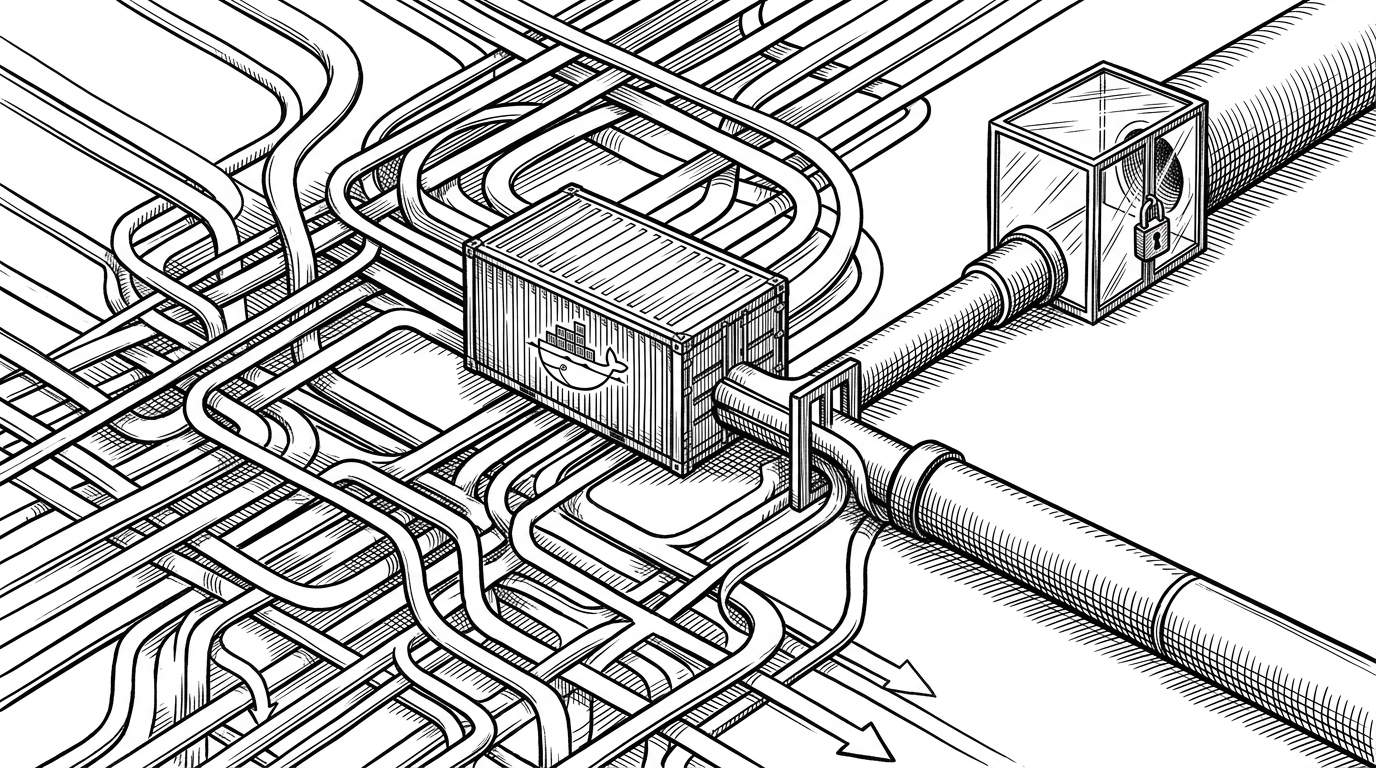
`proxy-everything`: The Docker Sidecar That Decides What Your Container Gets to Say
A deep dive into a Go-based transparent proxy that hijacks all container egress, peeks into TLS just enough to choose a path, and can even intercept DNS without touching application code.
Security & Supply Chain
anogs-analysis: The anti-cheat that waits to punish you
A reverse-engineered iOS framework that breaks startup into 51 steps, hides its strings in layers, scans loaded libraries, and lets the server deliver the real verdict.
Security & Supply Chain
haineypot: The Honeypot That Lies Like a Tired Linux Box
Google Research's high-interaction trap does more than fake a login prompt. It adds human-looking delay, captures every keystroke, and turns an intrusion into replayable evidence.
Security & Supply Chain
UnDefend: How a User-Mode File Lock Can Trip Up Windows Defender
A tiny C++ proof of concept targets the update gap, not the scanner, showing how timing, NTAPI calls, and shared file handles can undermine a security engine from standard-user context.
Security & Supply Chain
em-dash: Hard-Coding HIPAA into the Agentic Workflow
Moving beyond "vibes-based" compliance with Rego policies, evidence hashing, and the Claude Code ecosystem.
Security & Supply Chain
openai-agents-fastapi-starter: The safest way to let an AI agent touch a shell
A tiny FastAPI starter shows how to pair OpenAI Agents SDK with Vercel Sandbox microVMs, stream every tool call to the browser, and keep code execution ephemeral, inspectable, and serverless.
Security & Supply Chain
The AI Firewall: Inside experimental-ext-interceptors
How a proposed middleware extension is turning the Model Context Protocol from a raw communication channel into a secure, auditable standard.
Security & Supply Chain
The Zero-Knowledge Proxy: Inside duplicati/oauth-handler
How an open-source backup engine solved the impossible problem of desktop OAuth without absorbing massive security liability.
Security & Supply Chain
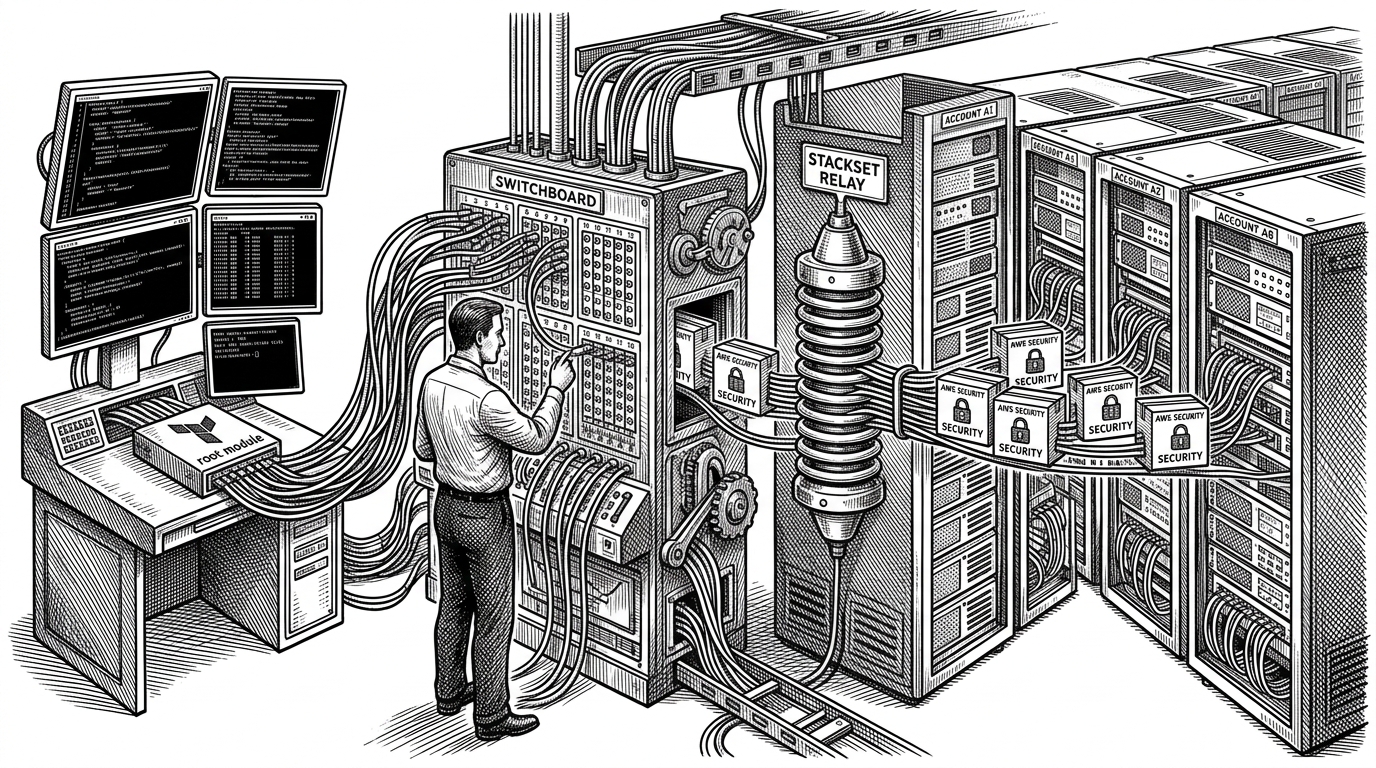
AikidoSec/aws-native-terraform-module: Terraform That Deploys Like an AWS Control Plane
It uses Terraform where orchestration belongs, StackSets where AWS can fan out cleanly, and `moved` blocks to refactor live security roles without a destructive rewrite.
Security & Supply Chain
Auditing the Autonomous Spender: Inside tomerhakak/agentprobe
How a local-first testing framework uses record-and-replay to tame infinite tool loops, catch prompt injections, and bring software engineering rigor to LLM agents.
Security & Supply Chain
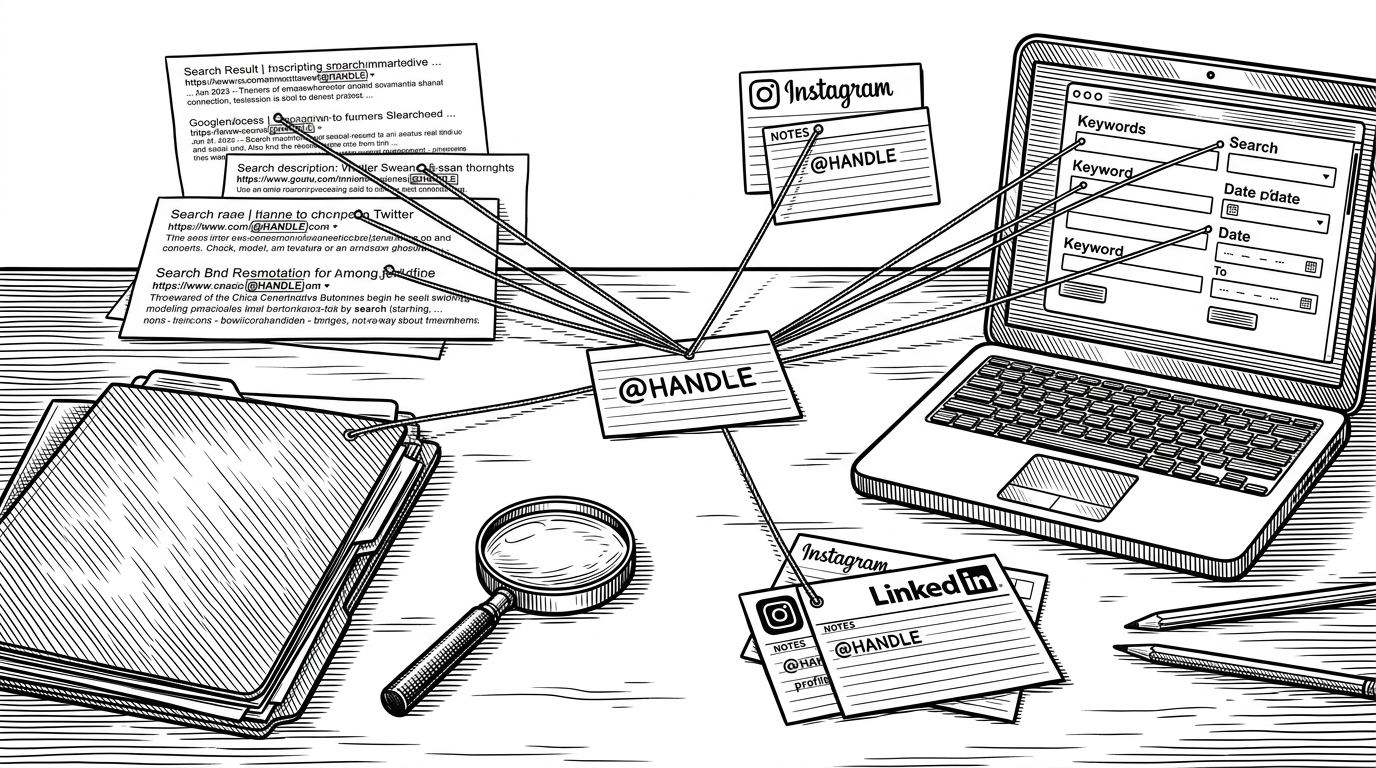
Twitter_Sleuth: The OSINT Tool That Hunts Twitter Through Google
A small Python framework turns dorking, cross-platform pivots, and structured reporting into a reconnaissance workflow for the age of locked-down social APIs.
Security & Supply Chain
Furina: The Rust DLL That Rebuilds a Game World From Packets
An internal Pixel Worlds cheat that hooks the game, decodes nested BSON messages, and turns compressed network data into a live minimap and player tracker.
Security & Supply Chain
Routing as a Weapon: Inside apernet-public-utils
How the team behind the Hysteria proxy uses minimalist Bash scripts to manipulate IPv6 tables, bypass geo-blocks, and squeeze maximum throughput out of cheap VPS instances.
Security & Supply Chain
circuitbreakerlabs/cli: The Automated Interrogation Room for LLMs
How a Rust-based man-in-the-middle proxy uses WebSockets and Rhai scripting to run adaptive, multi-turn adversarial attacks in CI/CD.
Security & Supply Chain
SilentHarvest_BOF: The registry dumper that makes BOF code feel normal
A niche Cobalt Strike module that sidesteps LSASS, leans on SeBackupPrivilege, and hides its own complexity behind a post-build symbol patching workflow.
Security & Supply Chain
`gascity-otel`: The Flight Recorder for AI Agents
A prewired OpenTelemetry stack for Gas City and Claude Code that turns prompts, tool calls, token burn, and agent lifecycles into something you can finally inspect.
Security & Supply Chain
aikido-kiro-power: Aikido's Kiro Power turns security into a write-time gate
This tiny repo does not scan code itself. It teaches Kiro to stop, check, fix, and rescan before unsafe code can move forward.
Security & Supply Chain
Quarantining the AI Supply Chain: Inside chain-ml/agent-reputation
How a Python pipeline uses isolated Docker sidecars and cryptographic hashing to build a unified trust layer for autonomous agents.
Security & Supply Chain
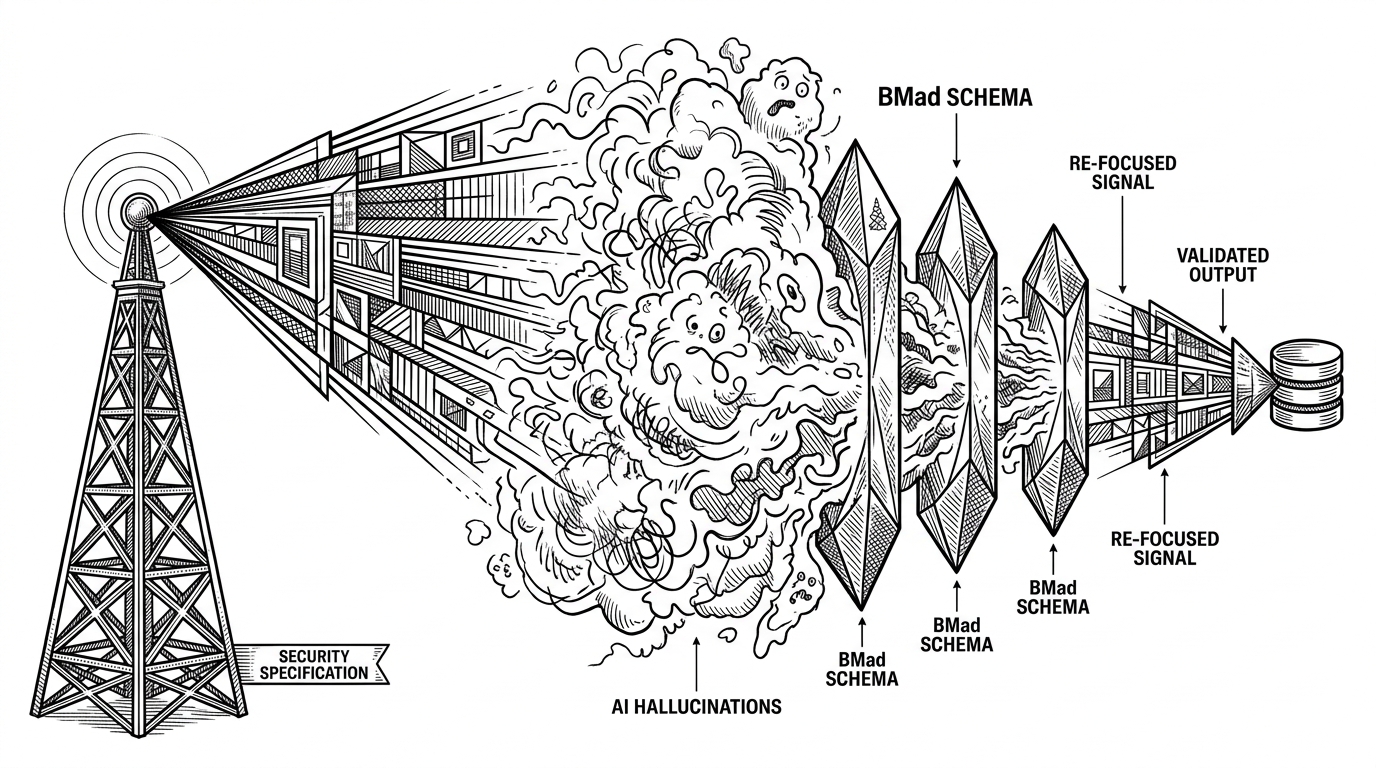
Compiling the Security Mind: How bmad-cyber-sec Hardens the AI Persona
Moving beyond "vibes" to a schema-first architecture that turns LLMs into validated, role-specific security engineers.
Security & Supply Chain
Kalim_Backdoor: How a DLL Turns a Windows Shortcut Into Persistence
Inside a MuddyWater-linked backdoor that hides behind COM, phones home through a fake updater routine, and keeps its shell and exfiltration threads running in parallel.
Security & Supply Chain
SharpAESCrypt: The .NET 8 Library That Encrypts Files Without Breaking the Past
A modern AESCrypt implementation for C# that balances strict security, legacy compatibility, and streaming performance.
Security & Supply Chain
The 50-Line Cryptographic Sieve: Inside nodebb-plugin-pwned-passwords
How a minimalist forum plugin uses k-Anonymity and a controversial fail-open architecture to verify passwords without ever transmitting them.
Security & Supply Chain
actions: Breaking the Build on Jailbreaks
How a suite of GitHub Actions brings traditional CI/CD discipline to non-deterministic LLM safety.
Security & Supply Chain
The Clinical Red-Teaming Engine: Inside circuitbreakerlabs-python
How a machine-generated Python SDK delivers high-stakes mental health safety evaluations for conversational AI.
Security & Supply Chain
vuln-scanner: The Glue Code of the Bug Bounty
How vuln-scanner transforms raw reconnaissance into a prioritized hit list for elite security researchers.