Security & Supply Chain
Open-source security, dependency auditing, supply-chain safety, and agent guardrails
227 explainers
Security & Supply Chain
npq: The Zero-Trust Bouncer for the npm Ecosystem
Why running npm install is the most dangerous thing you do all day, and how to intercept the threat before it hits your disk.
Security & Supply Chain
lenucksi/aur-malware-check: The emergency scanner that turned an AUR panic into a forensic playbook
A Bash-and-Python toolkit that does more than list suspicious packages. It checks install timing, persistence artifacts, and eBPF traces, then folds scattered community findings into one trusted workflow.
Security & Supply Chain
X4G: The Python Tunnel That Tries to Outthink the Network
A deep dive into a tunneling gateway that pairs VLESS relaying with adaptive flow control, quota-aware pacing, and a dashboard built to deploy anywhere.
Security & Supply Chain
ios-location-spoofer: The Repo That Fakes iPhone Location by Lying to Apple
A JavaScript MITM tool that rewrites the `/clls/wloc` response, patches protobuf fields, and makes iOS believe its Wi-Fi and cell world is somewhere else.
Security & Supply Chain
When the Harness Is the Hack: Codex-5.5-codex-instruct-5.5
A tiny Python tool shows how a normal CLI customization hook can become a persistent model-control path.
Security & Supply Chain
The End of the Script Kiddie: Unpacking shuvonsec/claude-bug-bounty
How a Python harness, strict logic gates, and persistent memory turned Claude Code into an autonomous security researcher.
Security & Supply Chain
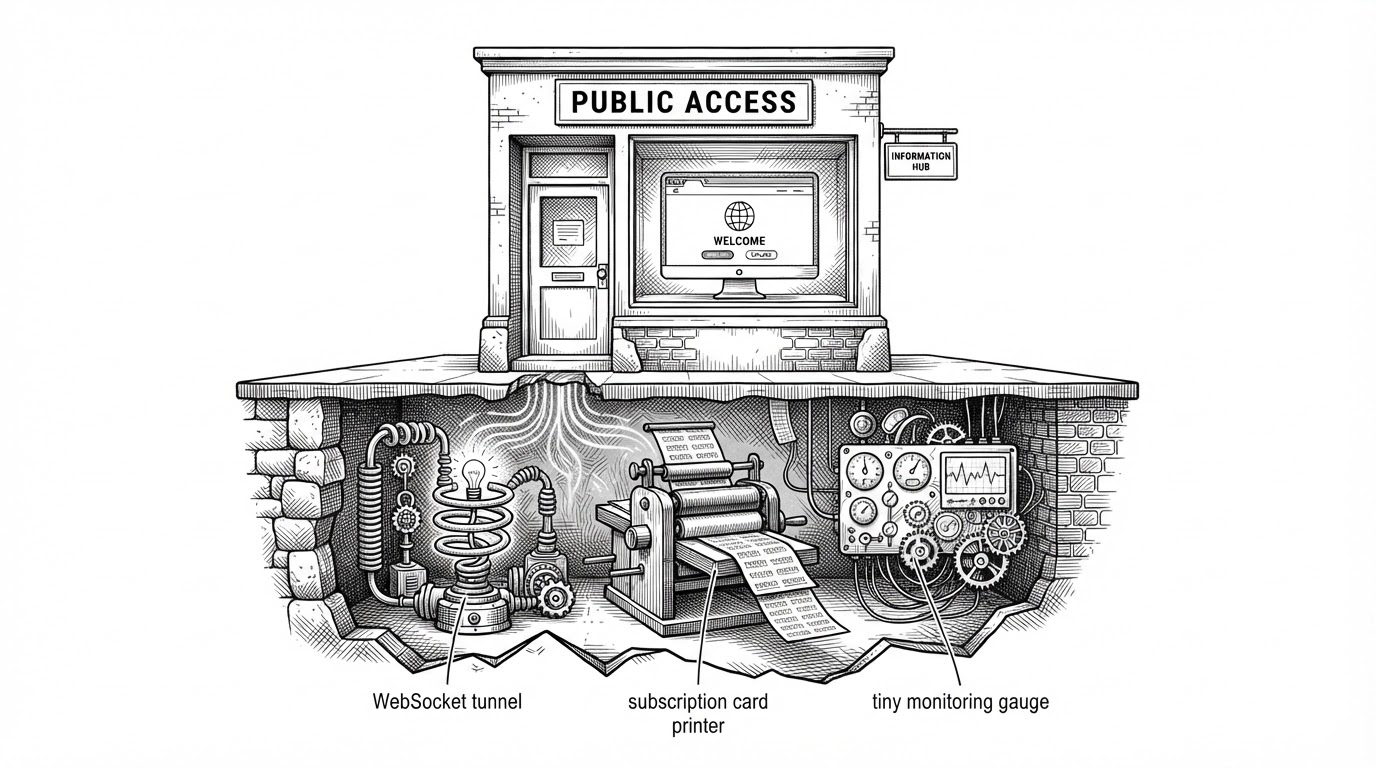
deploy-vercel: The Vercel Template That Hides a Proxy in Plain Sight
A single-file Node.js app turns a serverless host into a disguised gateway, a subscription generator, and a remote-monitorable tunnel, all wrapped in the language of a harmless website.
Security & Supply Chain
metamask-desktop: MetaMask Desktop: The Browser Extension That Built Itself a Fortress
A deep dive into how MetaMask keeps Web3 compatibility, provider injection, and security hardening intact while moving the wallet out of the browser and into a dedicated desktop host.
Security & Supply Chain
Deepsec: When a Security Scanner Learns to Think in Stages
A Vercel Labs harness that uses fast pattern matching, agentic investigation, and revalidation to turn vulnerability hunting into a disciplined pipeline.
Security & Supply Chain
Dify-Sandbox: How a Go Jail Lets LLMs Run Code Without Owning the Server
LangGenius’s sandbox trades per-task container startup for a tightly staged lock sequence: seccomp, chroot, privilege dropping, UID tricks, and a strict bootstrap order for Python and Node.js.
Security & Supply Chain
Nebula: The Pentester’s IDE That Decides When AI Should Read, Summarize, or Act
An open-source security workspace that blends a real terminal, local-first models, retrieval, memory, and agentic shell access into one workflow for offensive security.
Security & Supply Chain
The Digital Ventriloquist: How any-auto-register Industrializes AI Identity
A deep dive into the modular framework bypassing the world's most sophisticated bot detection through TLS impersonation and hardened automation.
Security & Supply Chain
conversation-steganography: Conversation Steganography: Hiding Secrets Inside Ordinary AI Chat
A Go-based proof of concept that uses arithmetic coding, local language models, and conversation state to make encrypted messages look like harmless text.
Security & Supply Chain
P4RS3LT0NGV3 Is a Disguise Engine for Text
A deep dive into the static browser toolkit that mutates language, hides payloads in Unicode, and reverse-engineers its own tricks.
Security & Supply Chain
secpipe: The Zero-Trust Agent: Inside pipelock
How a single Go binary acts as a local firewall to stop autonomous coding agents from exfiltrating your secrets.
Security & Supply Chain
Privado: Mapping the Secret Life of Your Data
How a graph-based static analysis engine turns "Privacy by Design" from a legal slogan into a verifiable build step.
Security & Supply Chain
splorp/wordpress-comment-blocklist: The Human Compiler Behind WordPress Spam Defense
A plain-text blocklist turns WordPress’s simplest filter into a privacy-preserving spam trap, using fragments, anchors, and years of manual pattern hunting.
Security & Supply Chain
pashov/skills: The Multi-Agent Mind Split for Smart Contract Security
How a collection of Markdown files forces LLMs to adopt eight distinct attacker personas and an adversarial judge to find deep Solidity vulnerabilities.
Security & Supply Chain
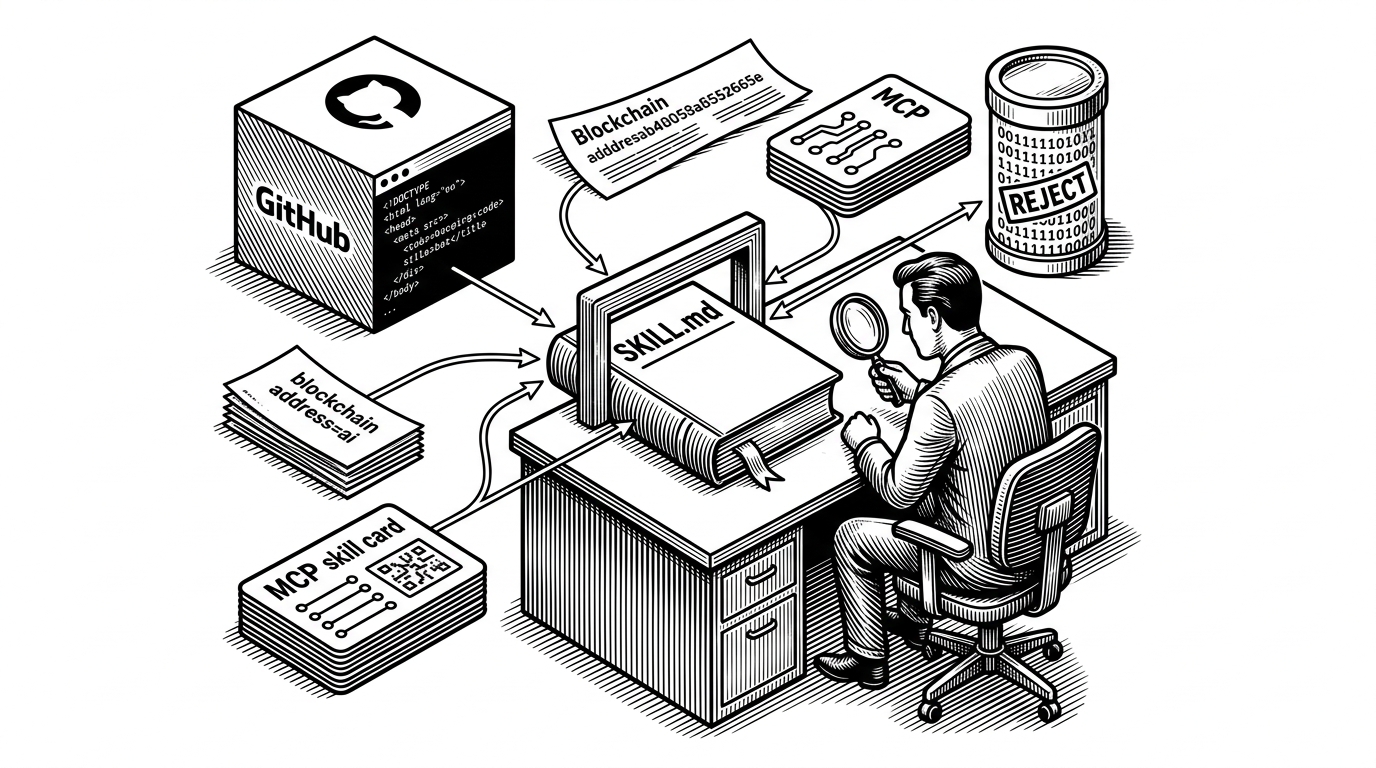
slowmist-agent-security: SlowMist Agent Security: The Markdown Firewall That Teaches AI Agents to Distrust Everything
A security skill built for autonomous agents, with trust tiers, red flags, and review templates that turn fuzzy judgment into a repeatable defense system.
Security & Supply Chain
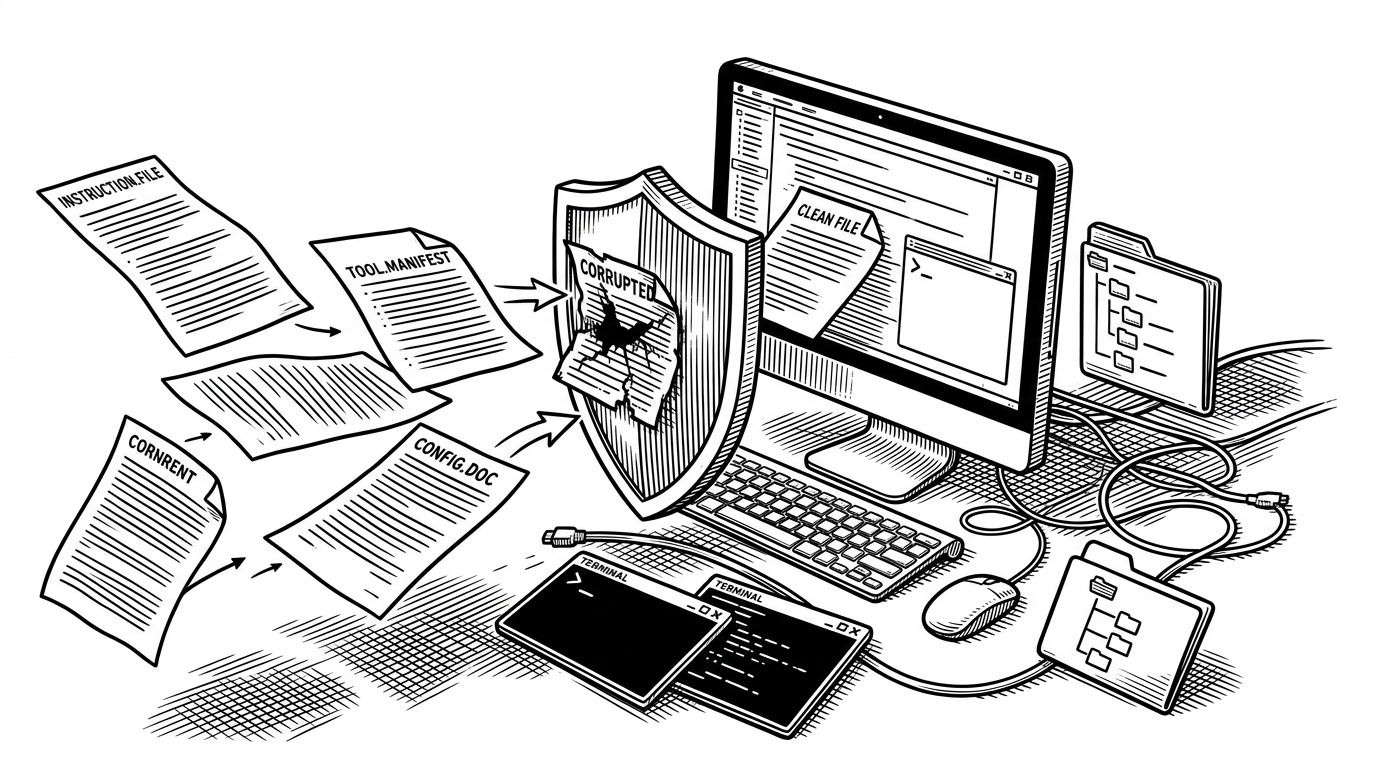
AgentSeal: The Antivirus Layer for AI Agents
A local-first security toolkit that scans skill files, audits MCP configs, and watches your agent directories for prompt injection, poisoning, and supply-chain tricks.
Security & Supply Chain
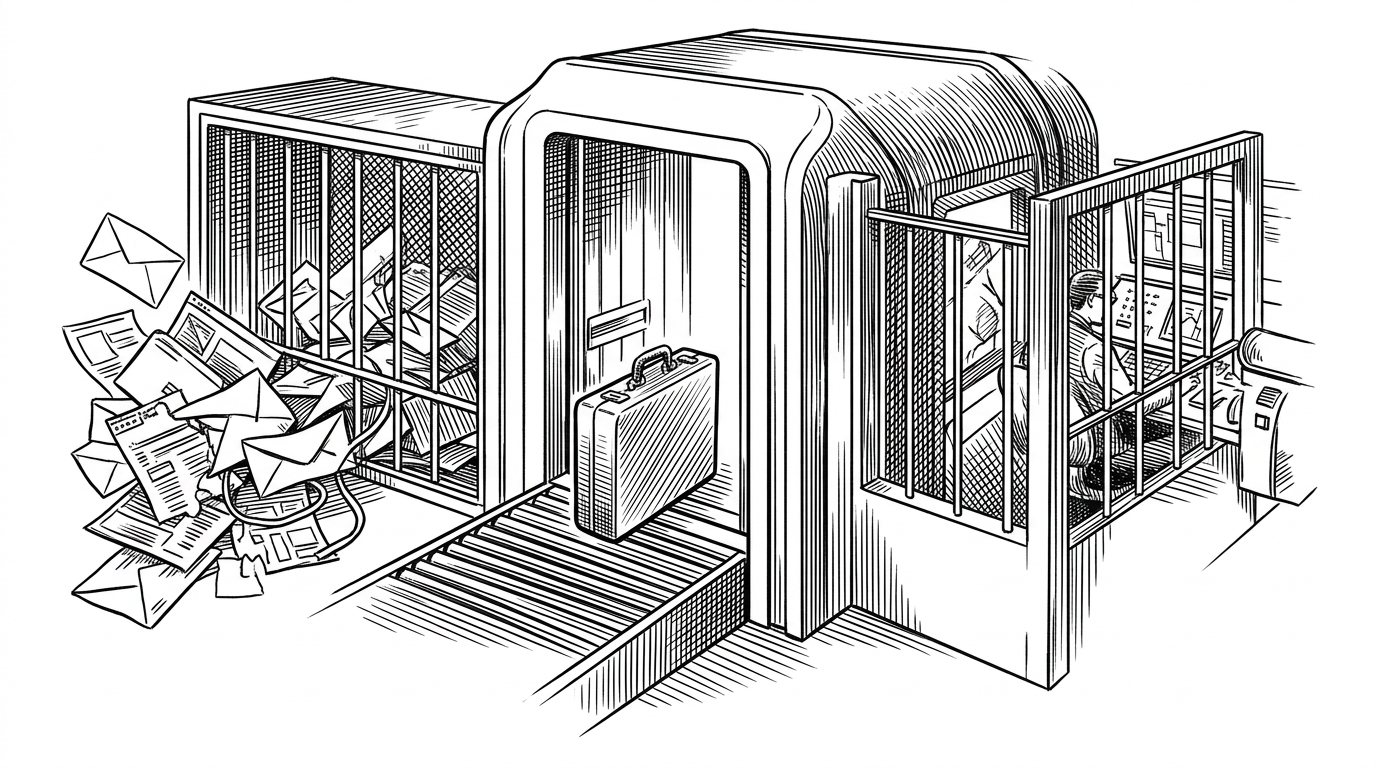
camel-prompt-injection: CaMeL draws a hard line between data and commands
Google Research's prompt injection defense uses a quarantined LLM, capability tags, and a custom interpreter to keep untrusted inputs from steering privileged actions.
Security & Supply Chain
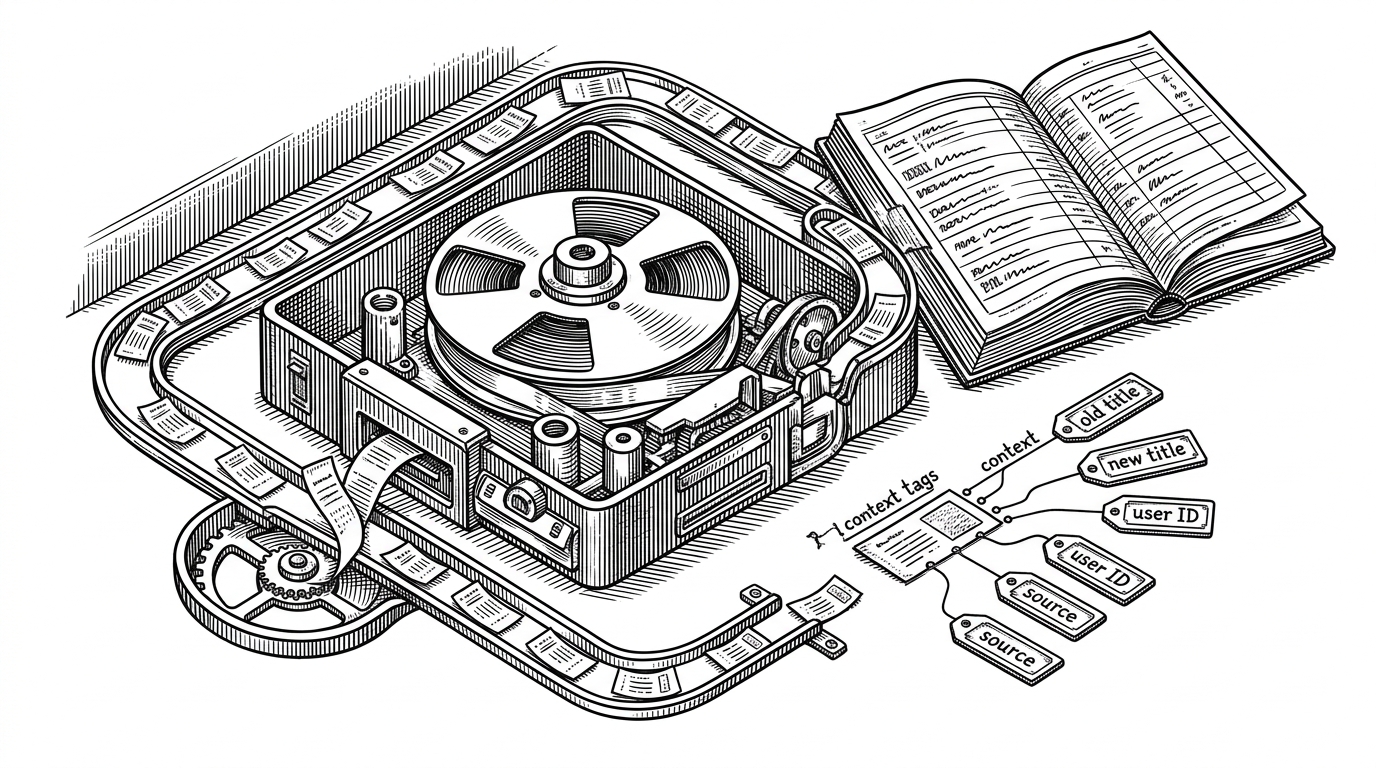
WordPress-Simple-History: The Plugin That Turns WordPress Into a Black Box Recorder
A deceptively simple audit trail that pairs a flexible event model with a two-table context system, modern PHP architecture, and developer-friendly logging hooks.
Security & Supply Chain
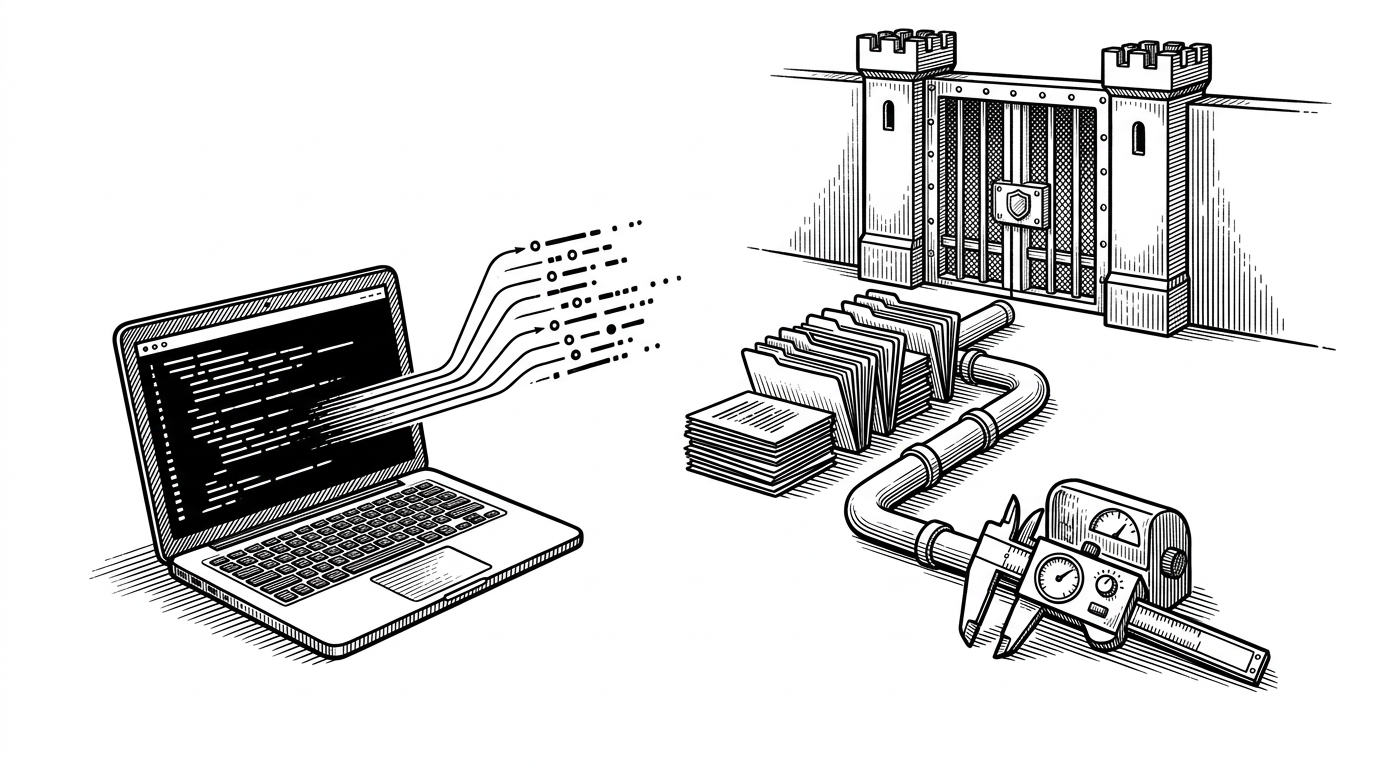
foxguard: The Rust Security Scanner That Wants to Feel Like a Linter
A local-first tool with AST parsing, cross-file taint tracking, secret detection, and PQC compliance, built to give developers security feedback before they leave the editor.
Security & Supply Chain
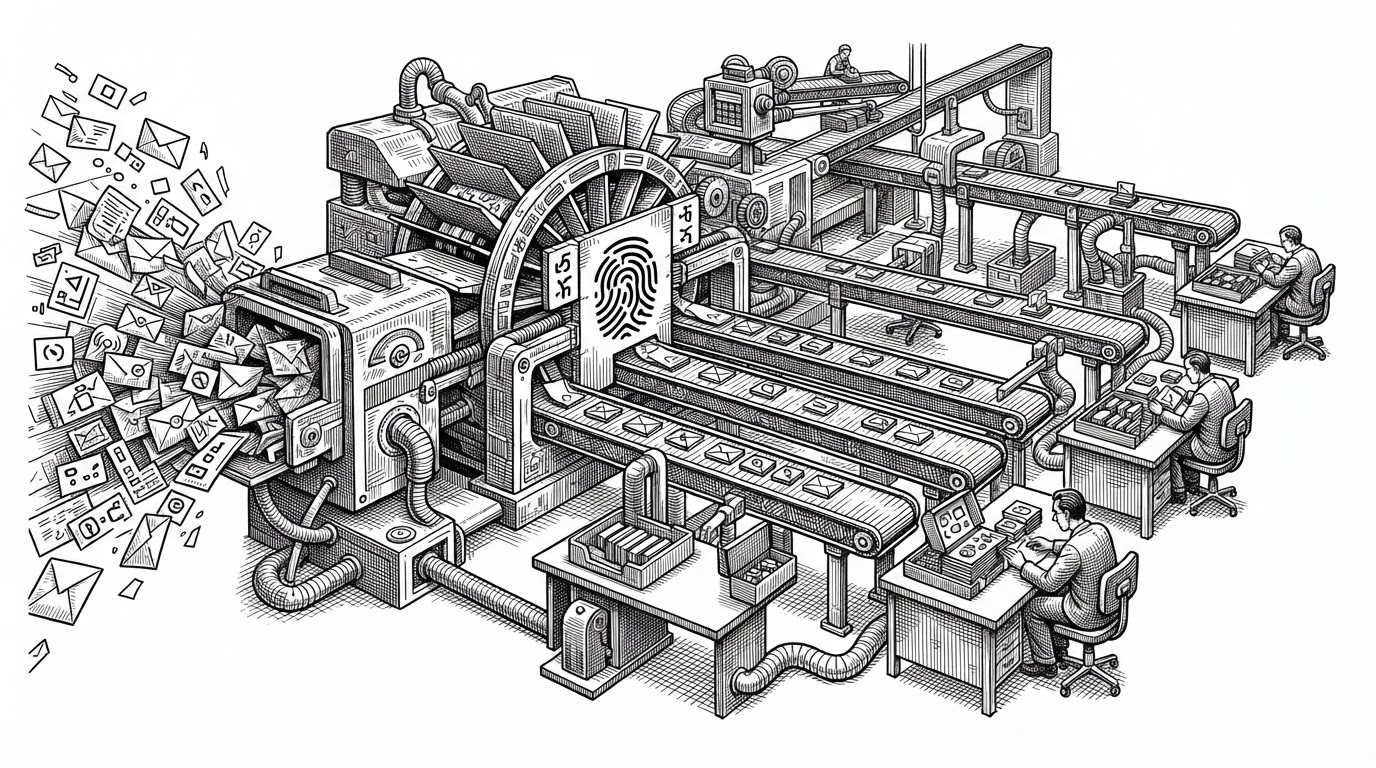
Packet_analyzer: The C++ DPI Engine That Turns Five-Tuple Hashing Into a Fast Path
A deep look at how this repository parses raw packets, tracks state per flow, extracts TLS SNI from encrypted traffic, and keeps every connection pinned to one worker thread.
Security & Supply Chain
Ophion: The Hypervisor That Lies to the Clock
How a stealth Type-2 hypervisor uses micro-architectural time compensation and private memory boundaries to subsume Windows and evade modern anti-cheats.
Security & Supply Chain
elder-plinius.github.io: The Poetry Site That Hides a Clipboard Payload
A tiny static page turns innocent clicks into hidden behavior. The real story is not the verse, it is the gap between what the page shows and what the code does.
Security & Supply Chain
cool-sdk: CooL SDK Turns AI Execution Into Cryptographic Evidence
A TypeScript SDK for confidential computing, transparency logs, and hybrid post-quantum signatures. It is built to prove what ran, where it ran, and whether the record was tampered with.
Security & Supply Chain
OpenShell-Community: The Operating System for Untrusted Agents
NVIDIA’s community repo packages sandboxes, skills, and bootstrap tooling around a sharper idea of AI safety: constrain the runtime, not the prompt.
Security & Supply Chain
The Invisible Scaffolding of the Java Ecosystem: Unpacking apache/maven-dependency-plugin
How hundreds of hermetic integration tests, bytecode scanning, and a strict Java 8 mandate keep the enterprise build pipeline from collapsing.
Security & Supply Chain
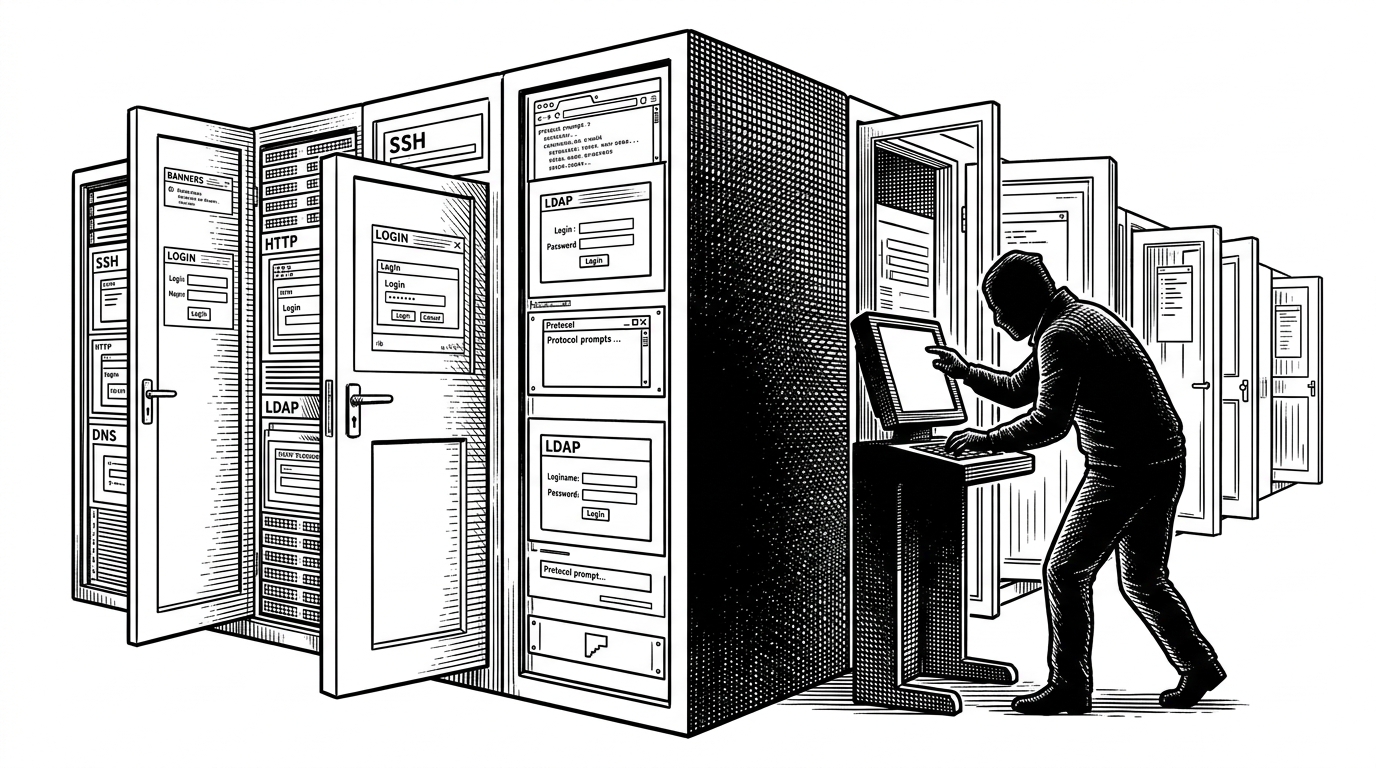
trapster-community: Trapster Community: The Honeypot That Keeps Talking
An open-source deception framework that uses AI, cloned web skins, and async protocol emulation to turn dead-end probes into long, believable attacker conversations.
Security & Supply Chain
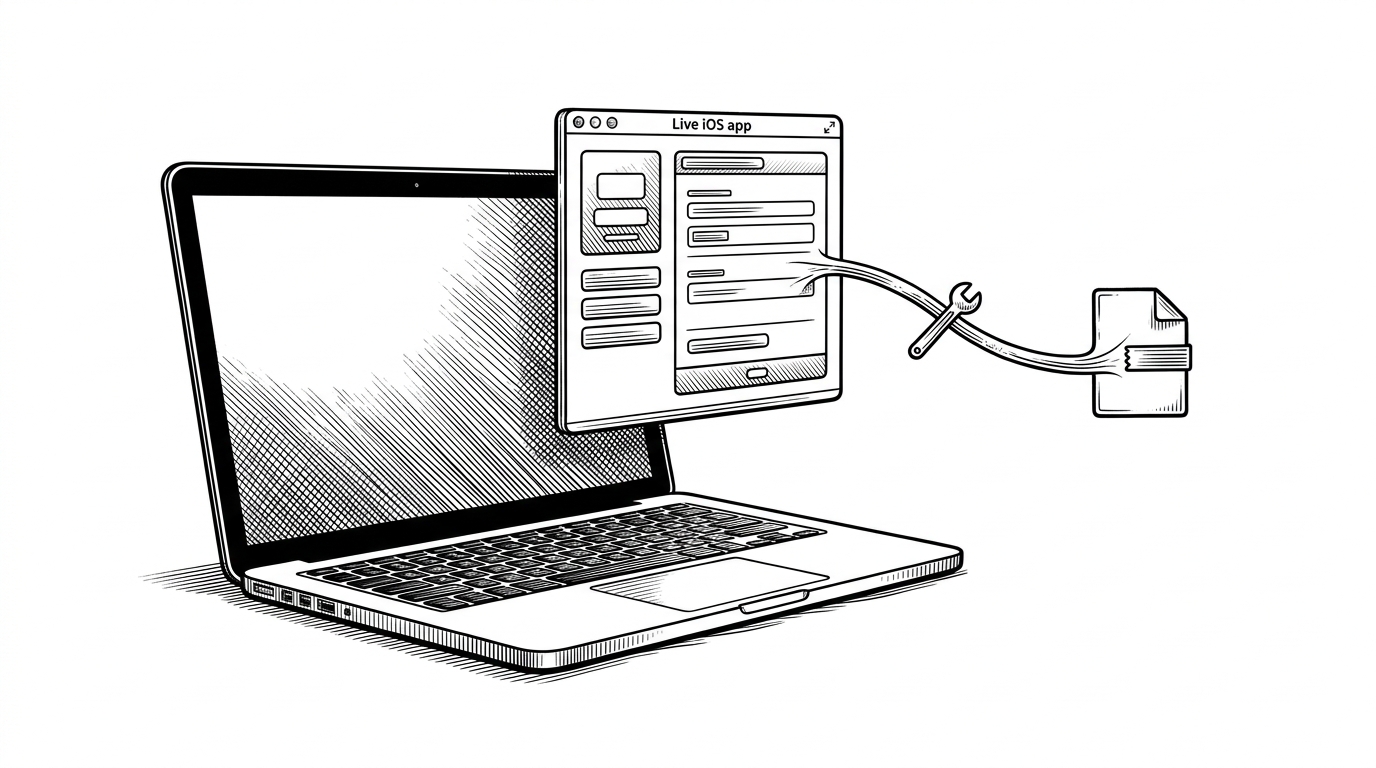
decrypted Turns Apple’s Own Debugging Tools Into a FairPlay Decryption Pipeline
A Swift UI, a Python engine, and a vulnerable `gcore` entitlement combine to dump decrypted iOS app memory, patch the Mach-O, and make the runtime state permanent.
Security & Supply Chain
LeakHub: The Truth Machine for Leaked AI Prompts
An open-source system that clusters noisy prompt scraps, verifies them by consensus, and turns a rumor mill into a real-time ledger.
Security & Supply Chain
claude-constitution: Anthropic turned Claude’s values into a file you can read
A versioned constitution for an AI model is not a product release note. It is governance as code, with trade-offs written out in plain language.
Security & Supply Chain
opentelemetry-ruby-contrib: OpenTelemetry Ruby Contrib: The Monorepo That Makes Ruby Auto-Instrumentation Feel Native
A tour of the generator, the dormant-loading pattern, and the SQL safety layer that lets dozens of gems behave like one observability system.
Security & Supply Chain
The Ghost in the Subnet: Unpacking iptables-mod-randmap
How an experimental kernel module bypasses connection tracking to turn a single server into a shapeshifting network prefix.
Security & Supply Chain
iron-sensor: An eBPF Security Camera for the Agentic Age
As AI coding agents gain ambient authority over our file systems, this lightweight monitor uses kernel-level hooks to track every autonomous intent.
Security & Supply Chain
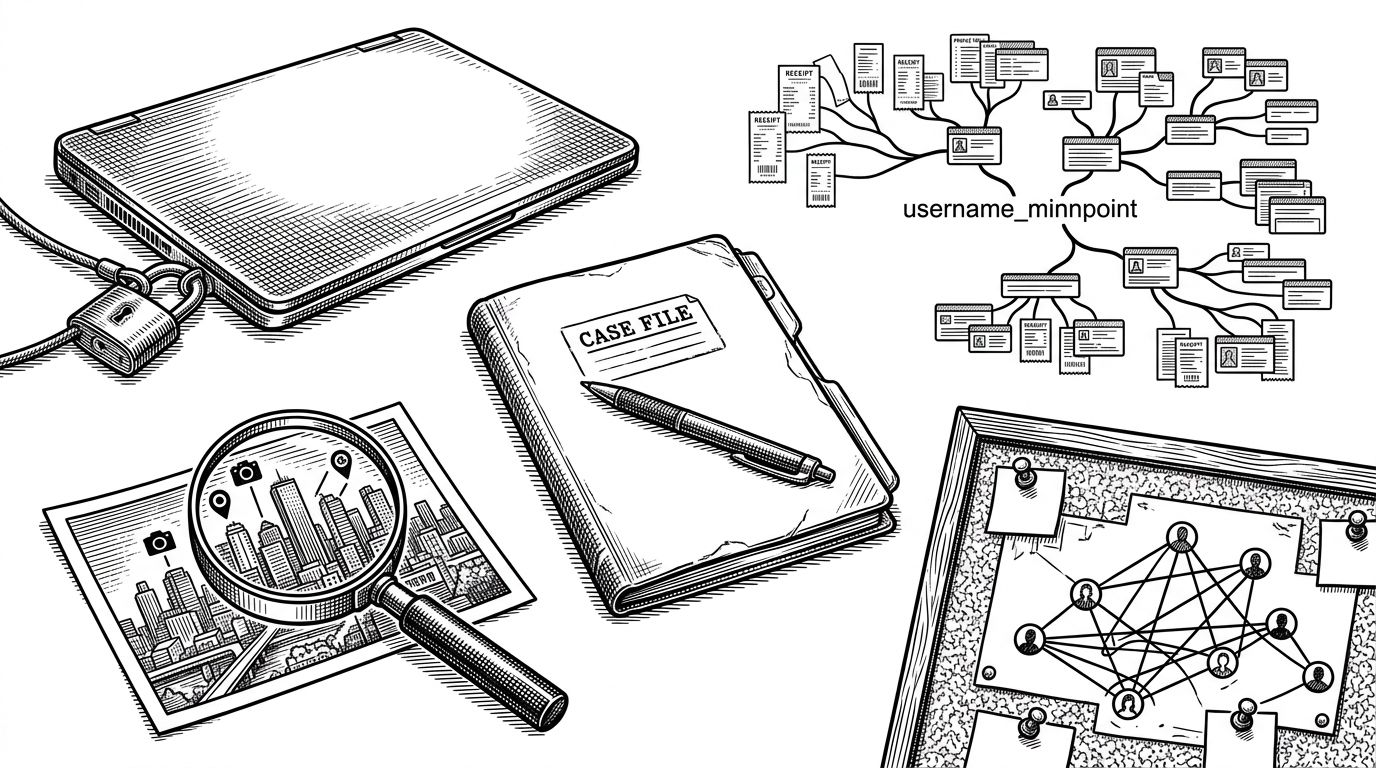
D4rk_Intel-OSINT-Investigative-Toolkit: The OSINT Repo That Thinks Like a Case File
A phase-by-phase workflow for secure setup, identity pivots, image forensics, and link analysis. This project is less a toolchain than a methodology for turning scattered clues into an investigation.
Security & Supply Chain
public-skills-builder: Mining the Collective Memory of Bug Hunters
How a specialized ETL pipeline transforms disclosed vulnerabilities into a high-signal Shadow-Brain for AI security agents.
Security & Supply Chain
Catching a Rogue Client Red-Handed: Inside nekogram-proof-of-logging
How a lightweight Xposed module and a Python script exposed a silent data exfiltration ring hiding inside a popular open-source Telegram fork.
Security & Supply Chain
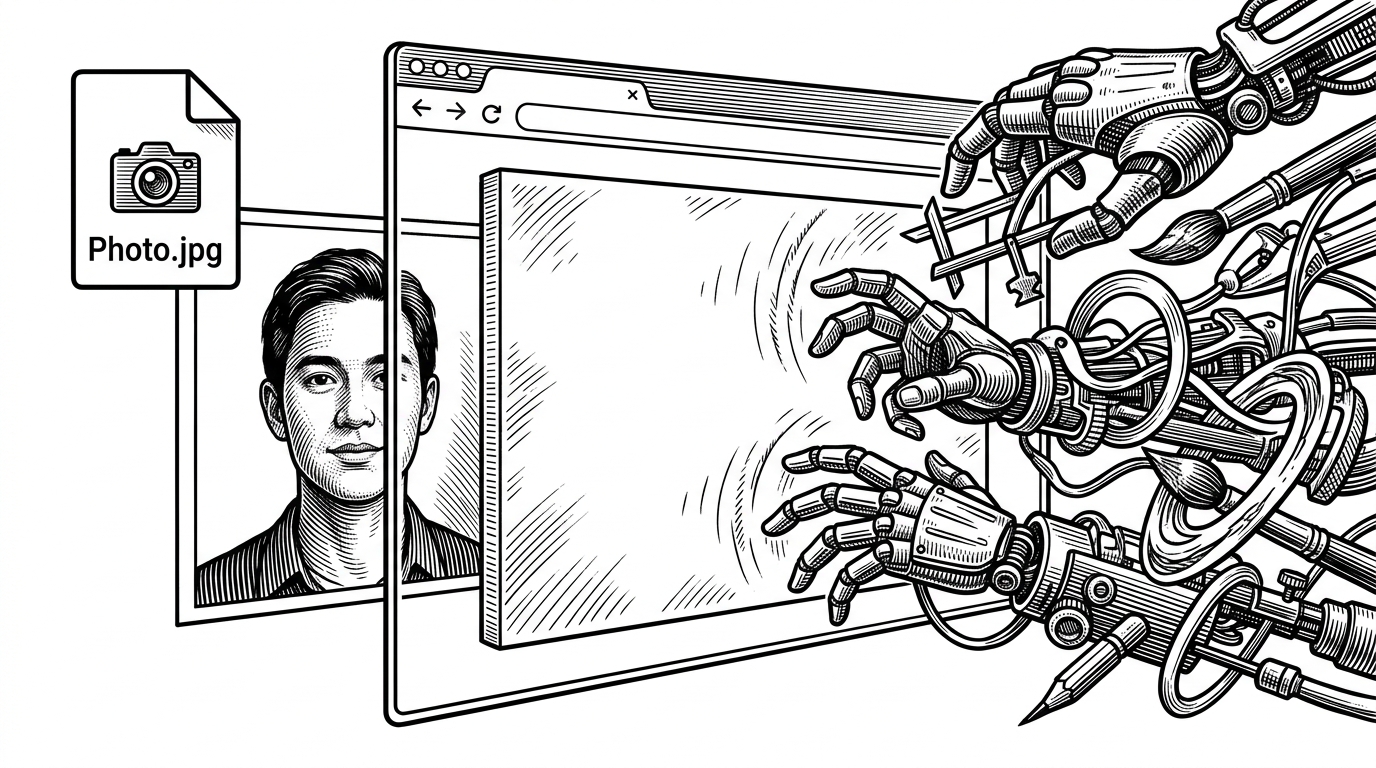
ImageDefender: The One-File Browser That Tries to Poison AI Image Edits
A client-side, Canvas-powered defense that keeps images local and turns plain HTML into a privacy tool.

Security & Supply Chain
Outpacket: The Rosetta Stone for the Post-Impacket Red Team Stack
A cheatsheet that does more than compare tools. It rewires how operators think about authentication, remote execution, Kerberos, SMB, and AD workflows across modern async tooling.
Security & Supply Chain
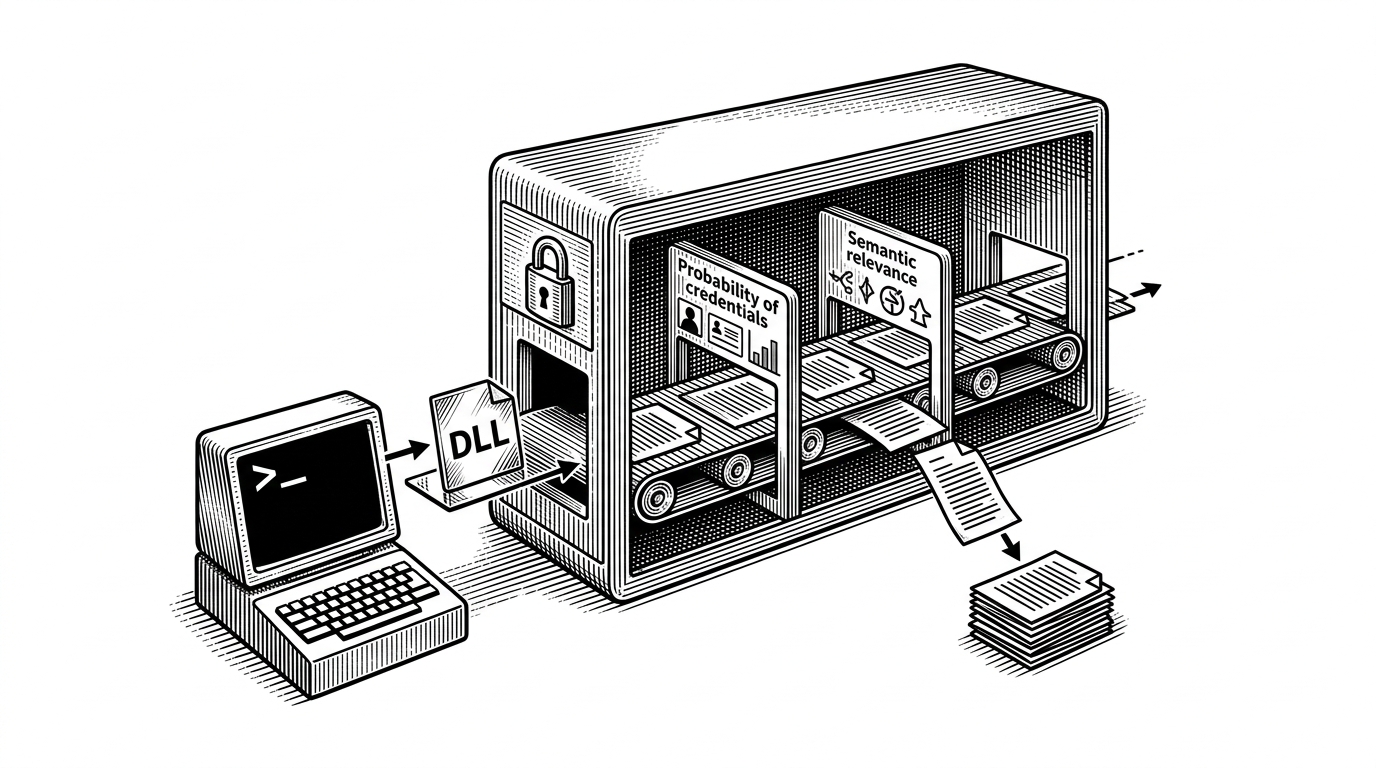
ai-postex: Post-Exploitation That Reads for Meaning, Not Just Strings
A Cobalt Strike extension that runs compressed ML models on the target, turning file triage into native Windows inference instead of grep-based guesswork.
Security & Supply Chain
Vinifera: The Watchtower That Scans GitHub Like a Security Team Would
A Ruby on Rails recon engine that tracks developer activity, catches stray public repos, and runs Gitleaks inside Docker to keep scans isolated, throttled, and production-safe.
Security & Supply Chain
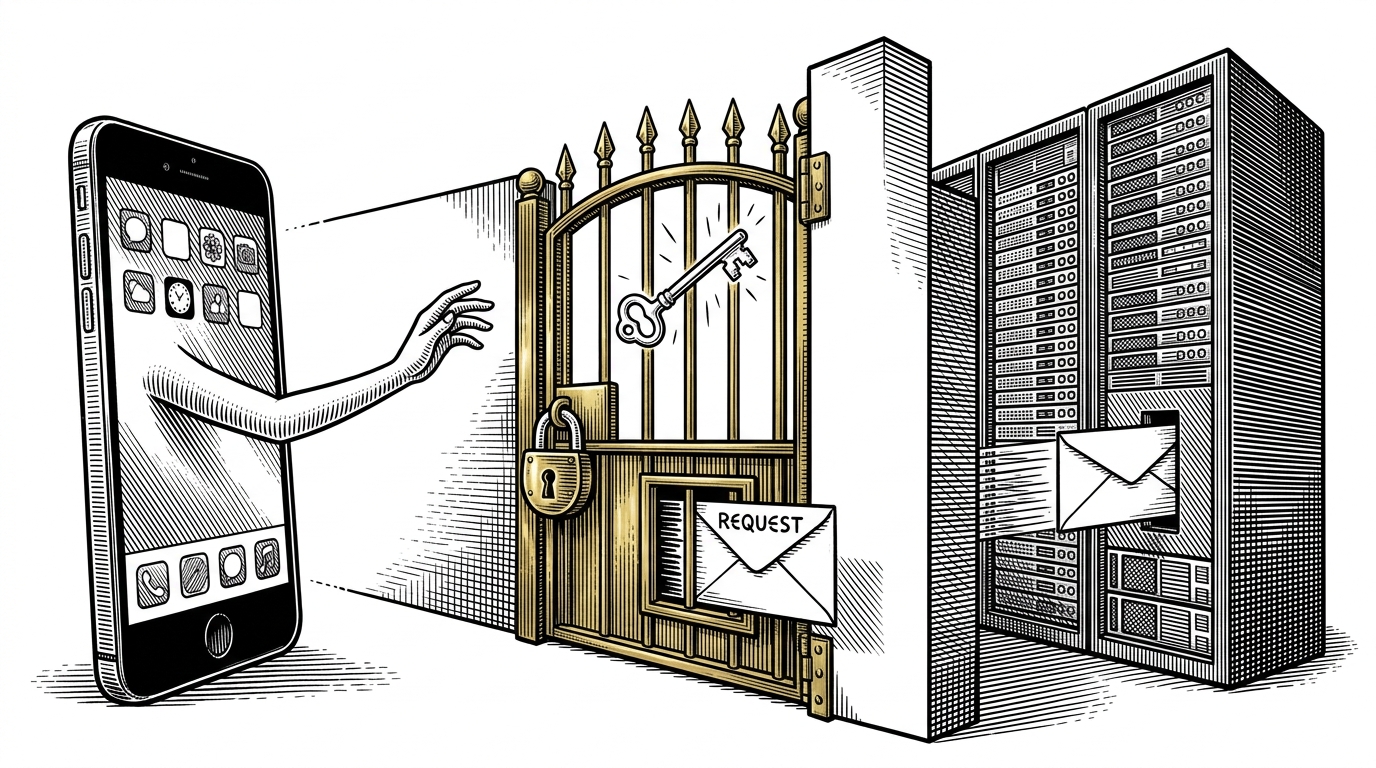
OpenAI-Proxy-PHP: The tiny PHP gatekeeper that keeps OpenAI keys off the client
A single-file middleware layer signs requests, freezes the model and prompt server-side, and turns image uploads into temporary URLs. It is less a proxy than a programmable security fence for AI apps.
Security & Supply Chain
The Art of the Passive Check: Inside rxerium-templates
How a boutique collection of Nuclei scripts uses metadata forensics and Base64 decoding to hunt zero-day vulnerabilities without firing a single exploit.
Security & Supply Chain
The Invisible Handshake: Inside modelcontextprotocol/ext-auth
How a specification-as-code repository is building the enterprise security mesh for the agentic era by solving the AI login problem.
Security & Supply Chain
NATURALIS-FUTURA: The Bestiary That Makes AI Risk Navigable
A cartographic encyclopedia that turns abstract threat modeling into something you can explore, remember, and compare.
Security & Supply Chain
openai-mcpkit: OpenAI's MCP kit starts where most demos end: authentication
A blueprint for bringing proprietary data into ChatGPT without flattening the enterprise security model.