Security & Supply Chain
Open-source security, dependency auditing, supply-chain safety, and agent guardrails
227 explainers
Security & Supply Chain
Ghidra: The Binary Translator That Makes Every CPU Look Alike
How the NSA built a reverse-engineering platform around a universal intermediate language, a hybrid Java/C++ stack, and a collaboration model most tools still do not match.
Security & Supply Chain
Hunting Ghosts at 400 Requests Per Second: Inside sherlock-project/sherlock
How a data-driven Python CLI bypassed SaaS bottlenecks to become the open-source standard for digital reconnaissance.
Security & Supply Chain
x64dbg: The Open-Source Surgeon of the Windows Core
How a community-built debugger ended the dark age of reverse engineering and turned binary deconstruction into a high-speed modular art form.
Security & Supply Chain
The Ghost in the Machine is a Markdown File: Unpacking CL4R1T4S
How an open-source library of extracted system prompts reveals the hard-coded rules, hidden tools, and fragile guardrails governing commercial AI models.
Security & Supply Chain
Devise: The Rails Authentication Stack That Made Login Feel Native
A deep look at how Devise wraps Warden, injects modules into models, and bakes hard-earned security defaults into the Rails way of doing things.
Security & Supply Chain
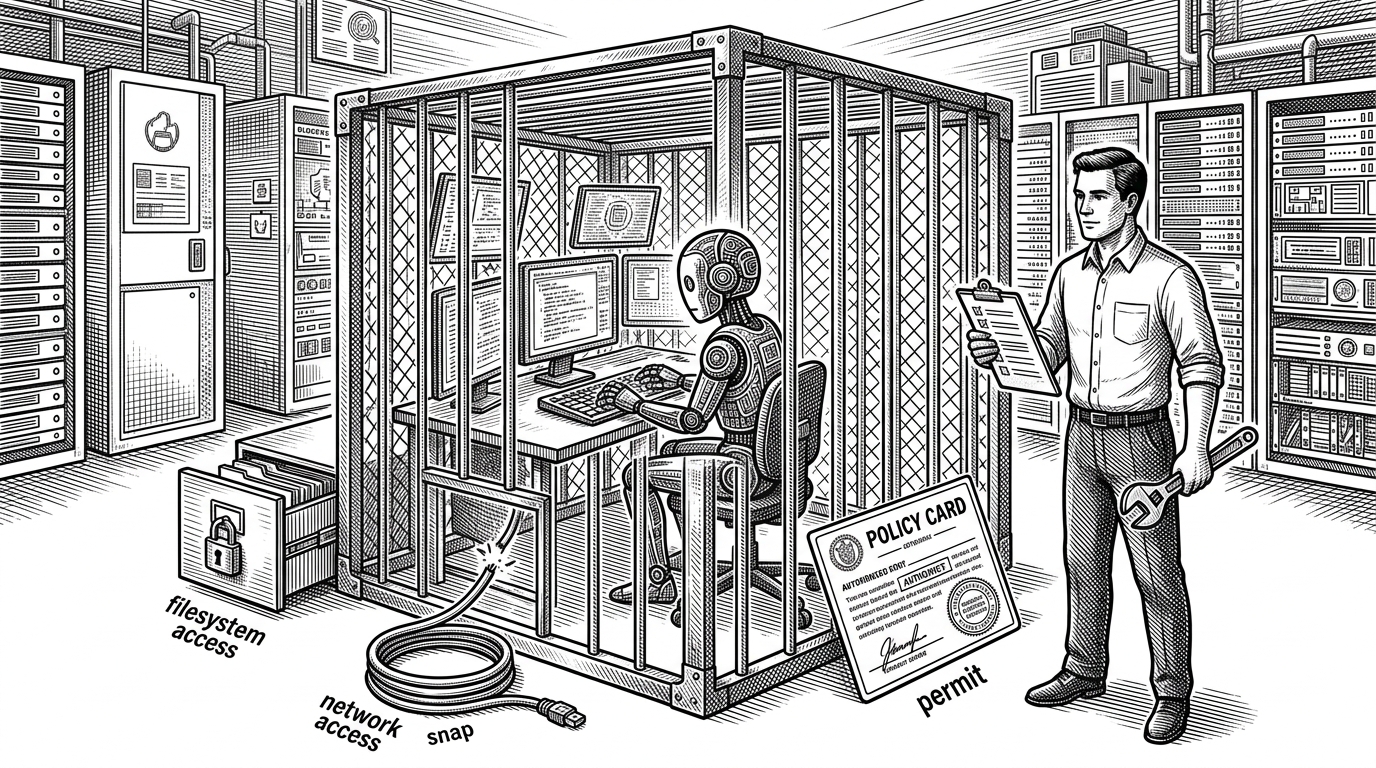
NVIDIA NemoClaw: The Sandbox That Treats Agents Like Untrusted Code
A deep dive into the stack that wraps OpenClaw in OpenShell, layers declarative policy on top, and turns autonomous assistants into operator-contained workloads.
Security & Supply Chain
Hysteria: The "Brutal" Protocol That Refuses to Slow Down
While the rest of the web politely yields to network congestion, Hysteria 2 uses a customized QUIC transport to punch through censorship and throttled networks.
Security & Supply Chain
L1B3RT4S: Weaponizing the English Language
How a pseudonymous researcher built a massive, open-source arsenal of linguistic exploits and glitch tokens to bypass AI safety guardrails.
Security & Supply Chain
SkillSpector: NVIDIA’s Scanner for AI Skills That Lie About What They Do
A hybrid security pipeline for agent-era supply chains, where static rules catch the obvious and LLM analysis catches the mismatch between promise and behavior.
Security & Supply Chain
The Math of Broken Servers: Unpacking Netflix/chaosmonkey
How an interface-driven Go binary uses statistical probability, Spinnaker, and standard Linux cron to enforce architectural resilience at global scale.
Security & Supply Chain
Zphisher and the Architecture of Disposable Deception
How a 34KB Bash script and zero-dependency PHP templates commoditized high-fidelity credential harvesting.
Security & Supply Chain
PentestGPT: The AI Pentest Tool That Refuses to Trust Itself
A deep dive into the compiler-like checks, receipt verification, and supervisor-executor split that turn an LLM from a chatterbox into an auditable offensive security system.
Security & Supply Chain
NVIDIA/OpenShell: The Runtime That Refuses to Trust the Agent
OpenShell keeps credentials, policy, and audit logging outside the sandbox, so autonomous code can act without owning the keys.
Security & Supply Chain
Bytebase: The Control Plane That Turns Database Changes Into Governed Releases
How Issue, Sheet, Release, CEL policies, and MCP turn database work into a reviewable system for humans and agents.
Security & Supply Chain
Ory Kratos: The Auth Server That Refuses to Be Your Login Page
A deep dive into the headless identity engine behind custom UX, schema-driven identities, and flow-based authentication.
Security & Supply Chain
Aegis: The Cryptographic Blindfold for Autonomous Agents
How local-first proxying solves the "Confused Deputy" problem by isolating raw credentials from the LLMs that use them.
Security & Supply Chain
wloc: How a Proxy Turns Apple’s Location Service Into a Ghost API
A clever iOS spoofing tool hides in MITM seams, rewrites Apple’s WLOC responses, and uses a web map plus Shortcuts to make system-level location control feel local.
Security & Supply Chain
CAI: The Zero-Refusal Actuator for Autonomous Offensive Security
How Alias Robotics turned the preachy LLM into a high-precision terminal controller for the next generation of red-teaming.
Security & Supply Chain
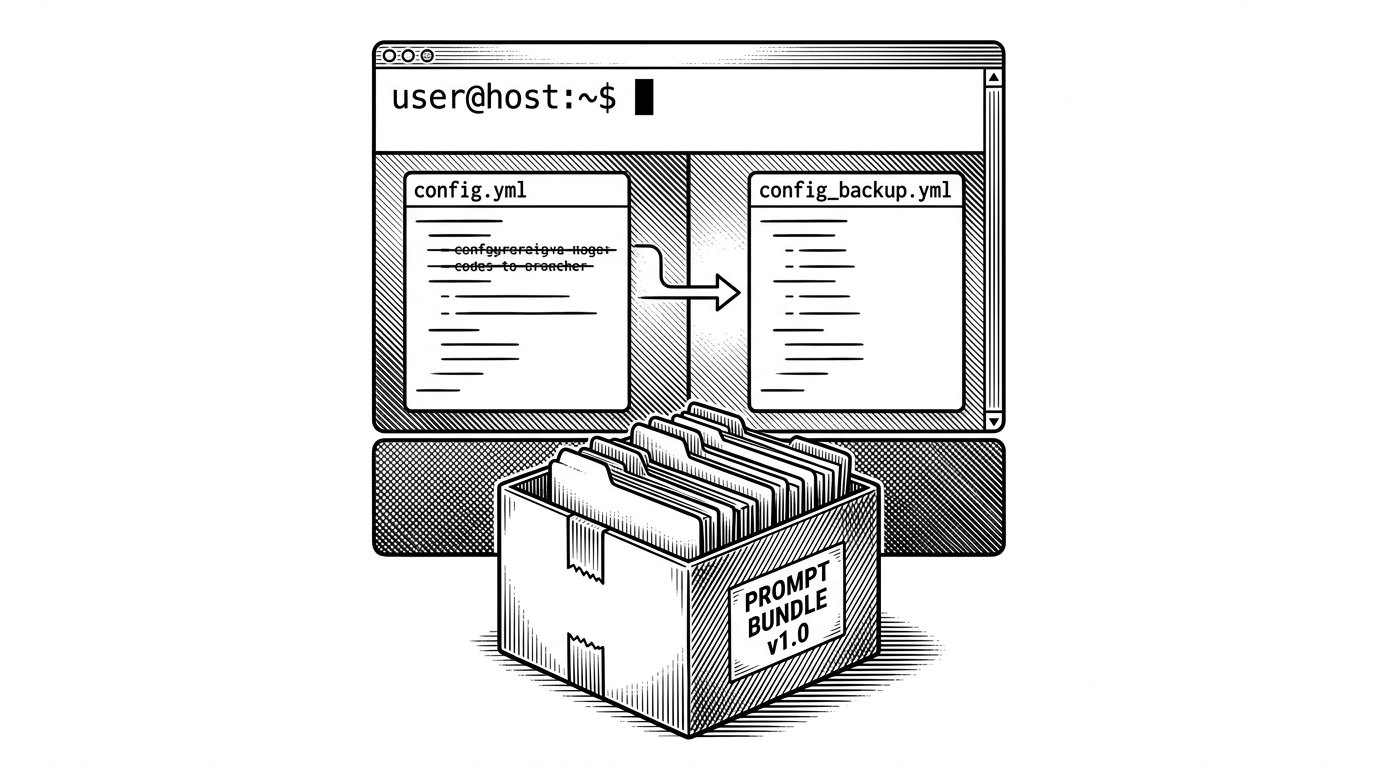
MDX-Tom/gpt-5.6-instruct: The Jailbreak Repo That Ships Like Real Software
A CLI-installed prompt system, backup-aware config switching, and regression-tested prompt variants reveal how adversarial AI work is turning into a disciplined engineering practice.
Security & Supply Chain
Lego: The Invisible Architecture of the Automated Web
How a modular Go library solved the 200-way handshake and became the silent engine behind cloud-native HTTPS.
Security & Supply Chain
Ignitetechnologies/Mindmap: Mapping the Chaos of the Cyber Frontier
How a visual-first repository became the definitive spatial index for the modern security researcher.
Security & Supply Chain
tpotce: T-Pot: The Honeypot OS That Turns Attack Traffic Into a Live Intelligence Pipeline
A deep dive into Telekom Security’s containerized deception platform, where read-only honeypots, distributed sensors, and ELK dashboards turn intrusion attempts into a high-signal map of hostile behavior.
Security & Supply Chain
OBLITERATUS: The Toolkit That Treats Refusal Like a Vector Problem
How a mechanistic-interpretability project tries to identify, project out, and verify LLM refusal behavior without retraining.
Security & Supply Chain
The Invisible Wall: How sandbox-runtime Hardens the AI Terminal
Anthropic's experimental runtime uses OS-native "Black Arts" to let autonomous agents run wild without breaking the host.
Security & Supply Chain
Exploitarium: The Repo That Turns Exploit Research Into an Assembly Line
A curated archive of PoCs, harnesses, and validation artifacts that makes exploit development look less like wizardry and more like a repeatable workflow.
Security & Supply Chain
dirtyfrag: Dirty Frag: How a Linux Fast Path Turned Read-Only Files into a Root Shell
A deterministic privilege-escalation framework that chains two kernel subsystems, writes through page cache pages, and shows how “dirty” bugs keep evolving.
Security & Supply Chain
Inside trailofbits/skills: how security expertise becomes a versioned system for Claude Code
Trail of Bits has packaged audit methodology, rejection patterns, and validation scripts into a marketplace of skills that teaches an agent how to think before it hunts for bugs.
Security & Supply Chain
mhr-cfw: The Proxy That Hides Behind Google, Then Escapes Through Cloudflare
A deep dive into a two-hop domain-fronting relay that turns Google Apps Script and Cloudflare Workers into a censorship workaround, with HTTP/2 multiplexing, SNI rotation, and latency tricks that make the disguise usable.
Security & Supply Chain
0xor0ne/awesome-list: The Exploit Research Syllabus Hidden Inside an Awesome List
A year-by-year map of kernel hacks, memory corruption, and modern bypasses, curated for people who need to understand the technique, not just run the tool.

Security & Supply Chain
zizmor: The Rust Compiler for GitHub Actions Security
A deep look at the tool that parses workflows, shells, and expressions like code, then turns CI security into a fast, offline, compiler-like analysis pass.
Security & Supply Chain
YellowKey: The Tiny WinRE Trick That Breaks BitLocker’s Biggest Promise
A USB folder, a recovery reboot, and one key held at the right moment seem to turn Windows’ rescue path into a full drive-unlock path.
Security & Supply Chain
awesome-api-security: The Taxonomy of API Warfare
How a curated Markdown file became the definitive utility belt for modern offensive and defensive API security.
Security & Supply Chain
anything-analyzer: Anything Analyzer: The Proxy That Watches, Decrypts, and Explains the Whole Stack
A reverse-engineering toolkit that merges Chromium capture, a custom MITM proxy, JS hooks, and MCP into one workflow for understanding private APIs and encrypted client logic.
Security & Supply Chain
Coraza WAF: The Go Engine Rewriting ModSecurity for Cloud-Native Traffic
A deep dive into how Coraza preserves SecLang compatibility, trims runtime overhead, and pushes WAF logic into Go apps, proxies, and WASM sidecars.
Security & Supply Chain
AdaptixC2: The C2 That Lets Scripts Reshape the Console
A deep dive into the Qt client, JavaScript bridge, and workflow design that turn a command-and-control tool into a programmable desktop workspace.
Security & Supply Chain
copy-fail-CVE-2026-31431: Copy Fail: The Tiny Python PoC That Exposed a Deep Kernel Blind Spot
Inside `theori-io/copy-fail-CVE-2026-31431`, a minimalist exploit that turns Linux zero-copy machinery into a privilege-escalation lesson.
Security & Supply Chain
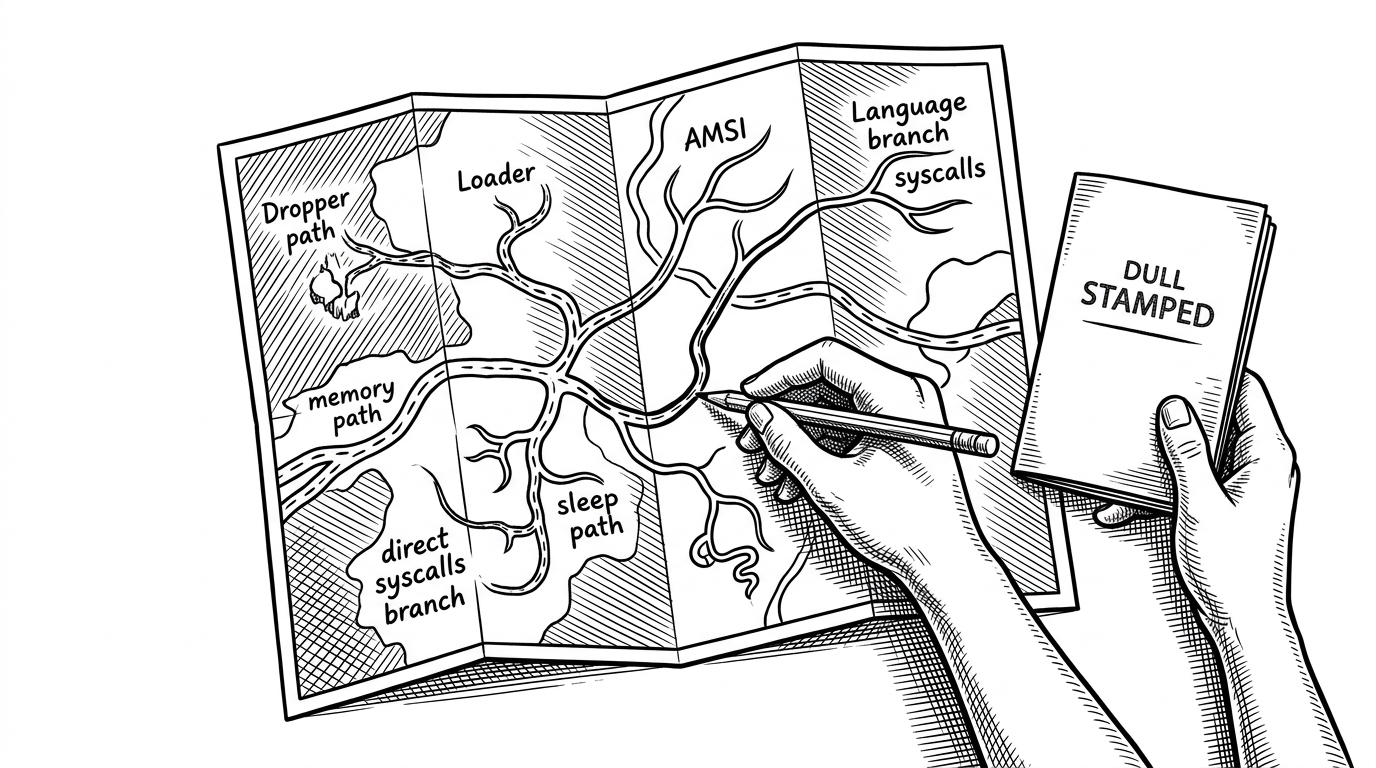
BypassAV: The Mind Map That Teaches How AV Evasion Fits Together
A curated offensive-security knowledge base that replaces “just run the tool” with a structured path through loaders, sleep obfuscation, indirect execution, and the manual techniques EDRs struggle to fingerprint.
Security & Supply Chain
MEV-Arbitrage-Bot: The Self-Custody Bot That Outsources the Hard Part
A Solidity vault, an off-chain trigger loop, and a deceptively simple promise: make arbitrage feel copy-paste friendly without turning the user into passive infrastructure.
Security & Supply Chain
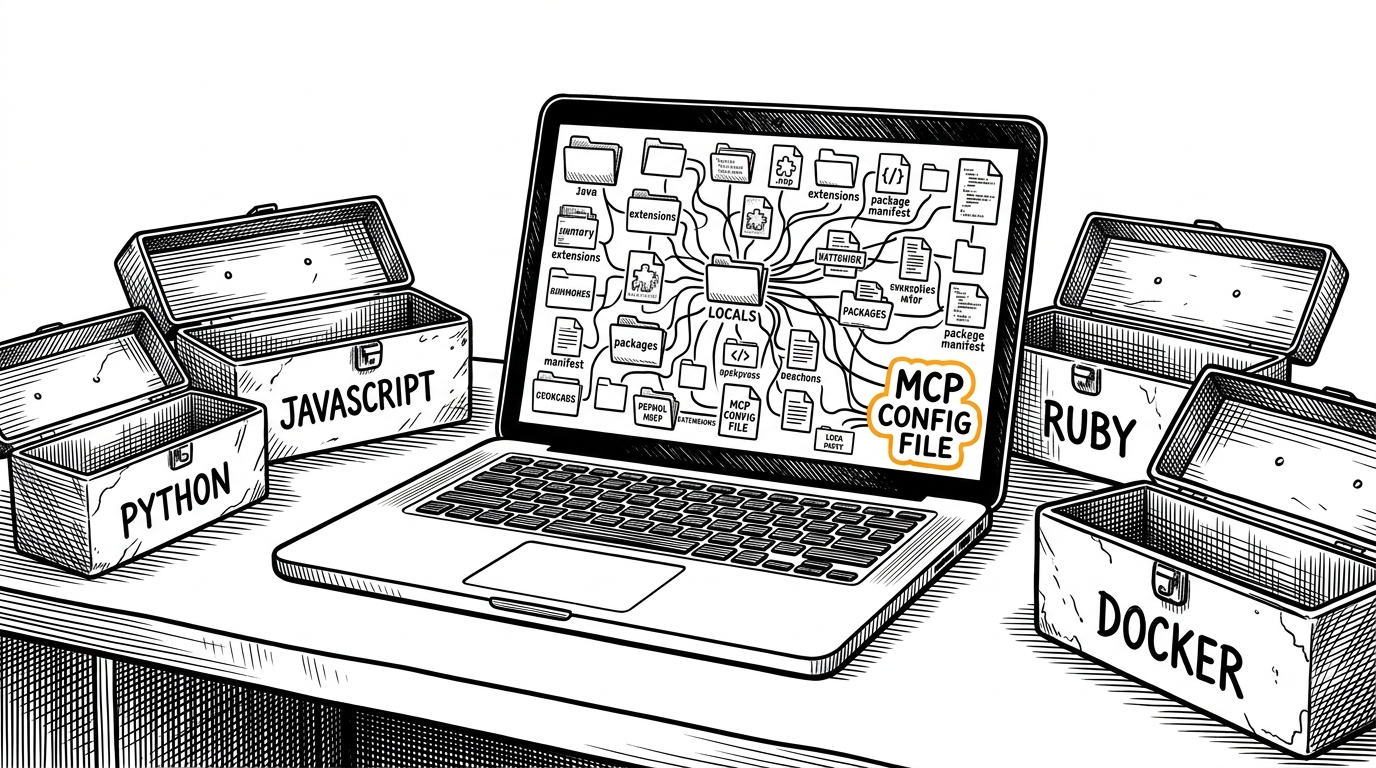
Bumblebee: The Scanner Built for the Developer Laptop Security Problem
A read-only Go tool that inventories on-disk packages, extensions, and MCP configs, then maps them to known supply-chain exposure without touching the machine it scans.
Security & Supply Chain
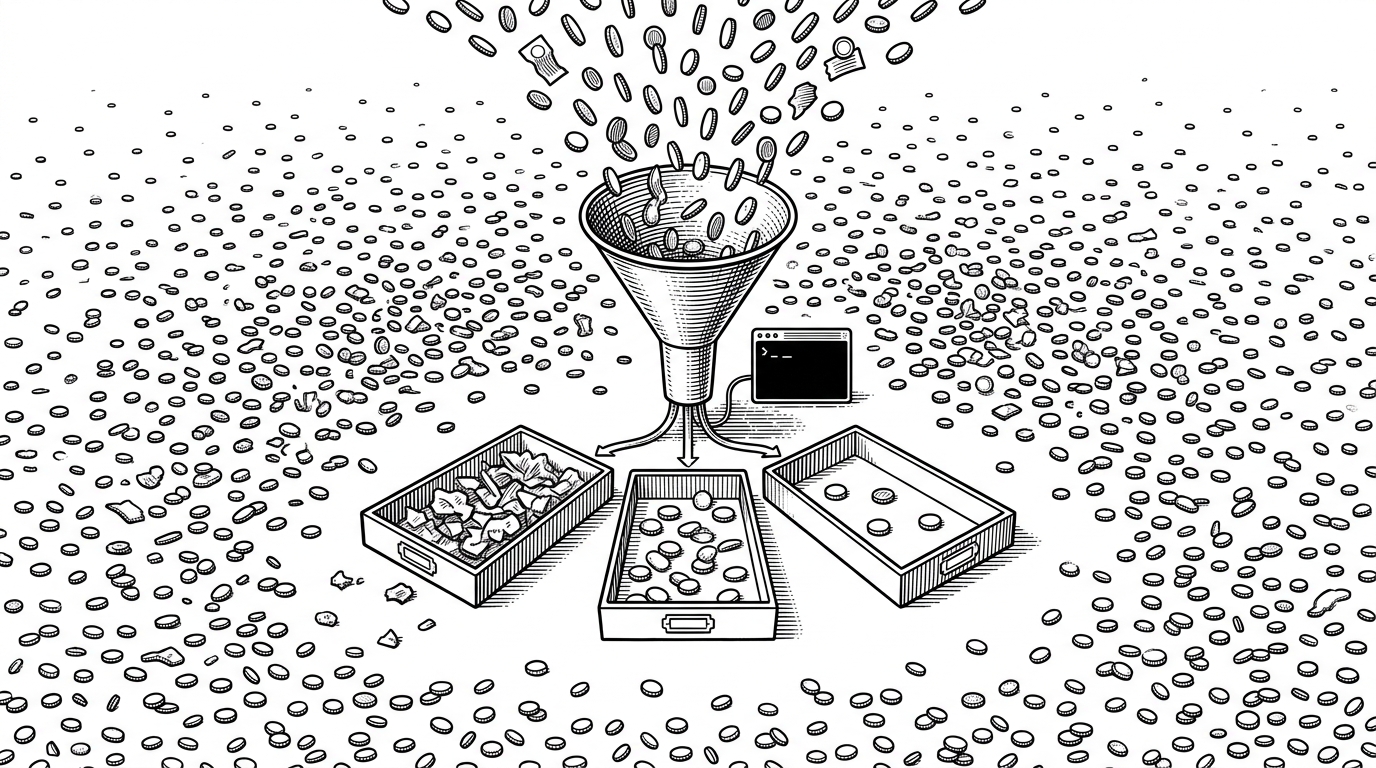
SenPaiScanner: The Go Tool That Turns Cloudflare IPs Into a Ranked Trust Funnel
A TUI-first scanner that filters noisy edge nodes with staged probes, jitter-aware scoring, neighbor expansion, and full Xray validation.
Security & Supply Chain
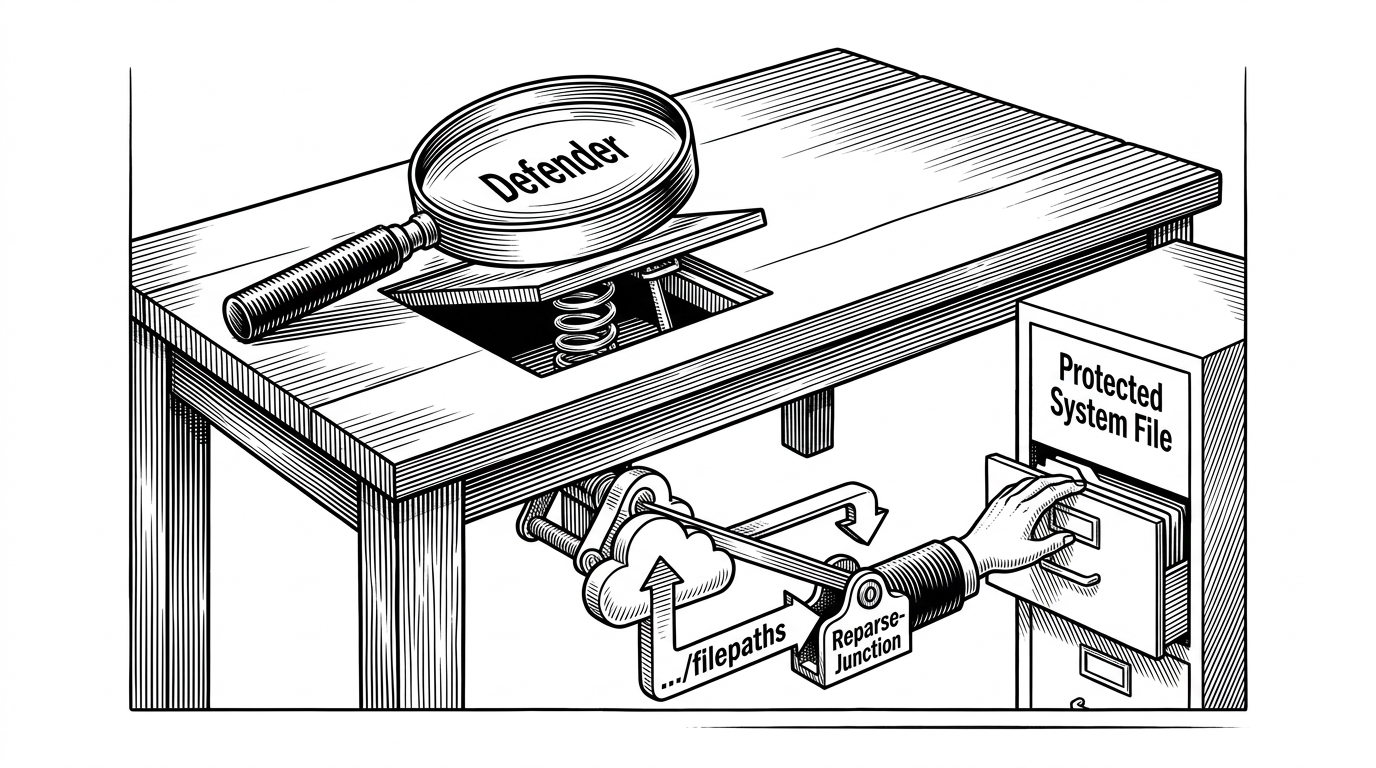
RedSun: How Windows Defender Becomes the Write Primitive
A Windows privilege-escalation PoC that chains Cloud Files, reparse points, and native NT file operations into one deeply ironic attack path.
Security & Supply Chain
Aether: The Rust Tunnel That Keeps Proving It Still Works
A censorship-circumvention client that turns route discovery, protocol camouflage, and end-to-end validation into one automated system.
Security & Supply Chain
BlueHammer: How Windows Defender Became the Attack Surface
A Windows PoC that blends private RPC, Object Manager symlinks, and offline registry tricks to show how a protection service can be steered into doing the wrong thing.
Security & Supply Chain
Knockoff: The Browser Extension That Judges Amazon by Its Brand Names
A no-build, local-first filter that scores suspicious listings, separates pseudo-brands from real ones, and turns Amazon search results into something closer to a curated shelf.
Security & Supply Chain
safe-chain: Aikido Safe Chain and the Art of the Benevolent MITM
How a local proxy intercepts your package manager to manipulate registry metadata and block zero-day supply chain attacks before they hit your disk.
Security & Supply Chain
Inside EggShell: The iOS Surveillance Time Capsule
How a Python script and a handful of Objective-C hooks turned jailbroken iPhones and locked Macs into remote sensor arrays.
Security & Supply Chain
RoguePlanet: When Windows Defender Becomes the Exploit Path
A race-condition PoC turns a trusted security scan into `SYSTEM` access, and the weird part is how ordinary the trigger looks.
Security & Supply Chain
elder-plinius/ST3GG: How Vectorized Python Weaponized a 90s Spy Trick
By replacing fragile loops with matrix operations, this multi-modal toolkit makes data exfiltration invisible to modern EDRs, LLM filters, and social media compression.